
The Cloud Security Alliance (CSA) Guide to Cloud Computing serves as a foundational framework for organizations aiming to design, deploy, and secure cloud environments. It provides standardized security controls, risk assessment methodologies, and governance models that allow IT professionals and stakeholders to navigate the complex shared responsibility landscape of modern cloud infrastructure.
Understanding the Role of the Cloud Security Alliance
The Cloud Security Alliance (CSA) is a non-profit organization dedicated to defining and raising awareness of best practices to help ensure a secure cloud computing environment. Established in 2008, the organization has since become a global authority on cloud security, publishing research, tools, and certifications that serve as the industry standard.
The CSA Guide to Cloud Computing is not a single static document but rather an overarching collection of resources, most notably the Cloud Controls Matrix (CCM). This matrix acts as a security control framework, providing organizations with a detailed set of fundamental security principles across various cloud technology domains. By aligning with the CSA’s guidance, businesses move away from ad-hoc security measures and toward a structured, defensible compliance posture that satisfies auditors and stakeholders alike.
Key Pillars of the CSA Security Framework
The CSA framework is built upon several critical documents that collectively define the lifecycle of cloud security. To effectively utilize these resources, professionals must understand how these pillars interact with one another.
The Cloud Controls Matrix (CCM)
The CCM is the cornerstone of the CSA’s offerings. It provides a controls framework that is mapped to leading industry standards, regulations, and control frameworks such as ISO 27001, NIST, and COBIT. The 2026 iteration of the CCM continues to serve as the primary tool for performing gap analyses and security assessments in cloud environments. It categorizes controls into domains such as Application & Interface Security, Cryptography, Governance, and Threat Management.
The Consensus Assessments Initiative Questionnaire (CAIQ)
While the CCM provides the "what" in terms of security requirements, the CAIQ provides the "how." It is a standardized set of questions that organizations can use to assess the security capabilities of a cloud service provider (CSP). By using the CAIQ, procurement and security teams can solicit consistent, comparable information from potential vendors, reducing the administrative burden of vendor risk management.
The STAR Program
The Security, Trust, Assurance, and Resilience (STAR) program is the registry where cloud providers list their security posture. Level 1 involves a self-assessment using the CAIQ. Level 2 involves third-party audits against the CCM, and Level 3 focuses on continuous monitoring. For an organization using the guide, leveraging the STAR registry is a critical step in verifying the compliance claims of the vendors they intend to use.

Implementing the Guide in Your Organization
Moving from theory to practice requires a phased approach. Implementing the CSA guidance is not a one-time project but a continuous cycle of assessment and improvement.
Phase 1: Gap Analysis
Begin by auditing your current cloud infrastructure against the domains outlined in the Cloud Controls Matrix. Identify which controls are currently implemented, which are partially implemented, and which are entirely absent. This baseline report becomes your roadmap for remediation.
Phase 2: Responsibility Mapping
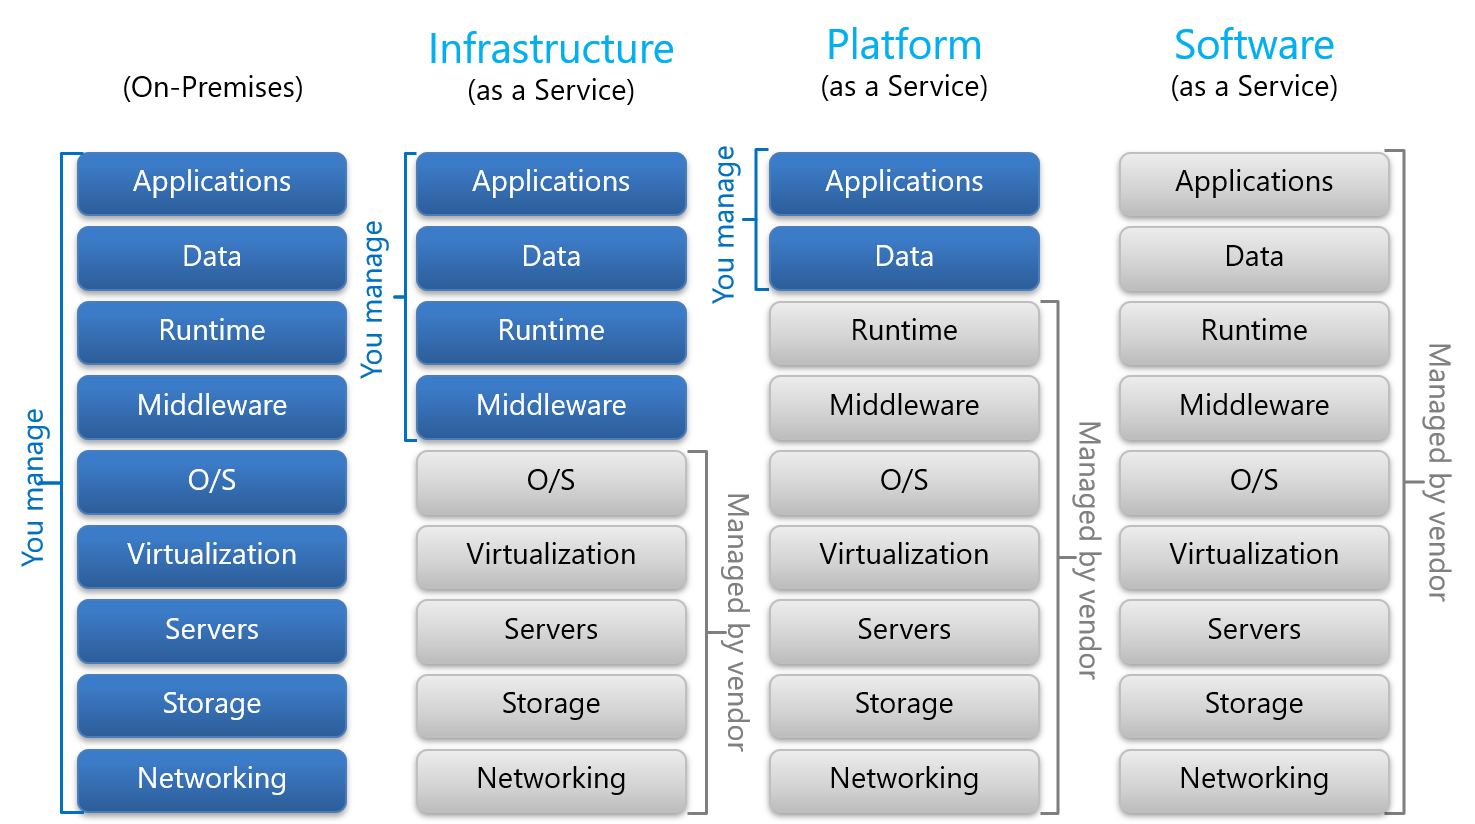
Cloud computing functions on the "Shared Responsibility Model." The CSA guide emphasizes the necessity of defining exactly which security tasks are the responsibility of the cloud provider and which remain with the customer. Use the CCM to document these boundaries. For example, in an IaaS (Infrastructure as a Service) model, the provider secures the underlying physical hardware, but the user is responsible for the operating system and data security.
Phase 3: Continuous Monitoring and Auditing
Once controls are in place, they must be validated. Periodic review of your architecture against the latest CSA guidance ensures that you remain aligned with evolving security threats. This phase often involves automating security checks to ensure that cloud configuration drift does not leave your environment exposed to vulnerabilities.
Comparison of Cloud Security Frameworks
Organizations often weigh the CSA framework against other global standards. While no single framework is superior, the CSA is uniquely tailored to the nuance of cloud-native architectures.
| Feature | CSA Cloud Controls Matrix | ISO 27001 | NIST SP 800-53 |
|---|---|---|---|
| Primary Scope | Cloud-specific security | General Information Security | Federal/Government Security |
| Adaptability | Highly flexible for SaaS/PaaS/IaaS | Requires extensive customization | Highly technical and rigid |
| Compliance | Industry-standard mapping | Certification-based | Mandated for US Federal |
| Audience | Cloud architects/CISOs | Compliance officers | Government contractors |
Navigating Common Challenges
Adopting the CSA guidance is rarely without friction. Organizations frequently face hurdles that can derail security initiatives if not anticipated.
- Complexity of Hybrid Environments: Many organizations operate across multiple cloud providers and on-premises data centers. The CSA framework is robust enough to cover these, but applying it consistently across disparate systems requires a high level of orchestration.
- Lack of Internal Expertise: Implementing the CCM requires a deep understanding of cloud architecture. Organizations often find that they need to invest in training their staff or hiring third-party consultants to bridge the knowledge gap.
- Shadow IT: Employees often provision cloud services without IT oversight. The CSA guide recommends strict governance policies to ensure that all cloud assets are visible to the security team and subjected to the same rigorous control framework.
Integrating CSA into Governance, Risk, and Compliance (GRC)
Integrating the CSA framework into your broader GRC strategy allows for better visibility at the executive level. By mapping the CCM controls to your organization's internal policies, you can report on your security posture in terms that business leaders understand: risk reduction and regulatory compliance.
Furthermore, when an organization prepares for an external audit—whether for SOC 2, GDPR, or HIPAA—the work performed using the CSA guide provides a significant head start. Because the CCM is mapped to these standards, a successful CSA implementation satisfies a large portion of the evidence requirements for these broader certifications.
Frequently Asked Questions
Is the CSA Guide to Cloud Computing mandatory for all companies? No, it is not a legal mandate. However, it is considered a best-practice framework. Many industries and government contracts require adherence to frameworks like those provided by the CSA to ensure vendors meet a baseline security posture.
How often should I update my security based on CSA guidelines? You should conduct a full gap analysis at least annually or whenever there is a significant change in your cloud architecture (e.g., migrating to a new provider or deploying a major new service). Continuous monitoring should be constant.
Can the CAIQ be used for non-cloud vendors? While the CAIQ is designed specifically for cloud services, its focus on infrastructure and data security makes it a useful reference for assessing any third-party technology provider that handles sensitive data, though it may require tailoring.
What is the difference between the CSA and NIST? The CSA provides cloud-specific guidance that is highly practical and operational. NIST SP 800-53 is a comprehensive catalog of security controls, often used by federal agencies. The CSA actually maps its controls to NIST, meaning they are complementary rather than contradictory.
Where can I find the latest version of the Cloud Controls Matrix? The latest versions of the CCM and other CSA tools are available through the official Cloud Security Alliance website. They are typically provided free of charge to the public as part of the organization's mission to improve global cloud security.
Does the CSA offer training for their framework? Yes, the CSA provides the Certificate of Cloud Security Knowledge (CCSK), which is specifically designed to validate an individual's proficiency in using the CSA framework and cloud security best practices.
Recommended Next Steps
To begin your journey with the CSA guide, start by downloading the latest version of the Cloud Controls Matrix from the official website. Once you have the document, perform a preliminary self-assessment of your most critical cloud environment. Identify the "low-hanging fruit"—the security controls that are currently missing but could be easily implemented—and prioritize those for your next sprint. By establishing this foundation, you move your organization toward a more secure, compliant, and resilient cloud posture in 2026 and beyond.
Image Gallery
Select an image to open it in a new tab.


Lars Thomsen
Global Labor Markets and Economic Strategy Editor
