
HIPAA compliant secure cloud faxing is a digital communication service that enables healthcare providers to transmit Protected Health Information (PHI) via encrypted internet protocols instead of traditional analog phone lines. To achieve compliance, these services must utilize end-to-end encryption (AES-256), provide a signed Business Associate Agreement (BAA), maintain granular audit trails, and enforce strict user access controls to ensure data integrity and privacy throughout the transmission lifecycle.
The Evolution of Faxing in the 2026 Healthcare Landscape
In 2026, the healthcare industry remains significantly reliant on fax technology despite the proliferation of Electronic Health Records (EHR) and interoperable APIs. The persistence of faxing is largely due to its status as a legally recognized method of document exchange and its universal compatibility across disparate medical systems. However, the traditional analog fax machine—connected to a physical copper phone line (POTS)—is increasingly obsolete. The transition to secure cloud faxing represents a critical modernization step for clinics, hospitals, and pharmacies seeking to balance legacy requirements with modern cybersecurity standards.
Cloud faxing, also known as e-faxing or IP faxing, removes the physical hardware vulnerabilities associated with paper documents sitting on an output tray. Instead, it treats faxes as digital data packets. In the context of the Health Insurance Portability and Accountability Act (HIPAA), the move to the cloud introduces new responsibilities. Organizations must ensure that their service providers are not merely "secure" but are legally and technically structured to meet the specific mandates of the HIPAA Privacy and Security Rules.
Regulatory Framework: HIPAA, HITECH, and the Role of PHI
Understanding secure cloud faxing requires a firm grasp of the regulatory environment. HIPAA was designed to protect the privacy and security of health information. The Health Information Technology for Economic and Clinical Health (HITECH) Act later strengthened these protections by increasing the penalties for non-compliance and expanding the responsibilities of Business Associates (service providers).
Protected Health Information (PHI) includes any information in a medical record that can be used to identify an individual and that was created, used, or disclosed in the course of providing a healthcare service. When this data is transmitted via a cloud fax service, it is categorized as Electronic Protected Health Information (ePHI). Under the HIPAA Security Rule, covered entities must ensure the confidentiality, integrity, and availability of all ePHI they create, receive, maintain, or transmit.
Secure cloud faxing addresses three primary areas of the Security Rule:
- Administrative Safeguards: Implementation of policies and procedures to manage conduct and security measures.
- Physical Safeguards: Protection of the physical data centers where the cloud servers reside.
- Technical Safeguards: Technology and the policy and procedures for its use that protect ePHI and control access to it.
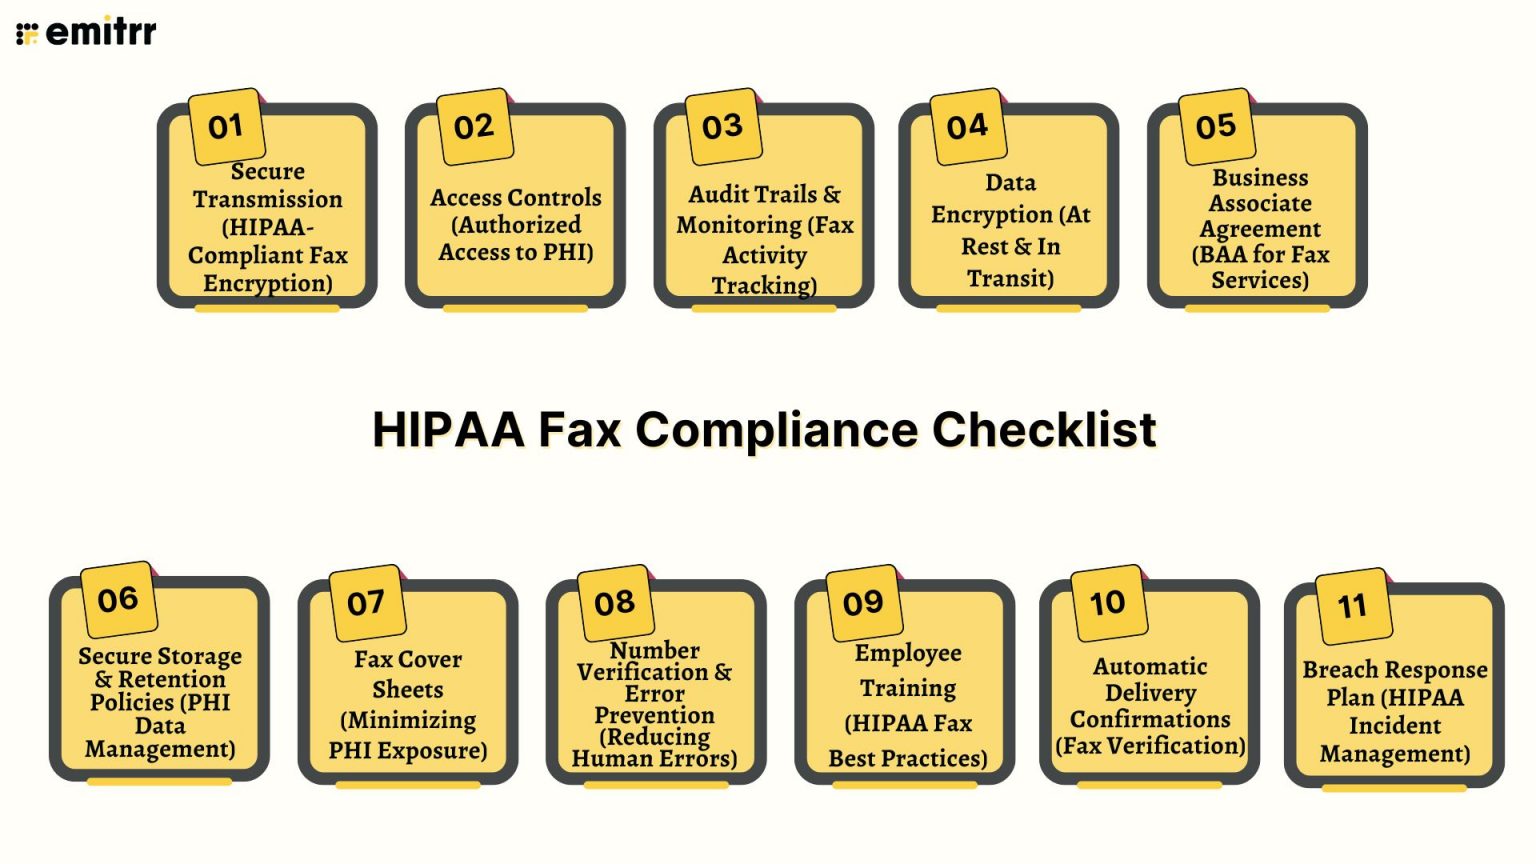
The Critical Necessity of the Business Associate Agreement (BAA)
The most significant differentiator between a standard cloud fax service and a HIPAA compliant one is the Business Associate Agreement (BAA). A BAA is a legal contract between a covered entity (the healthcare provider) and a business associate (the fax service provider). This document specifies the responsibilities of each party regarding PHI and requires the business associate to adhere to the same security and privacy standards as the covered entity.
In 2026, utilizing a service for PHI transmission without a signed BAA is a direct violation of HIPAA, regardless of how robust the encryption might be. The BAA serves as the legal foundation for compliance, ensuring that if a breach occurs, the responsibilities and liabilities are clearly defined. Many consumer-grade fax services claim to be "secure" but refuse to sign a BAA; these services are unsuitable for healthcare use.
Core Technical Requirements for Secure Cloud Faxing
To meet the rigorous demands of the modern threat landscape in 2026, a cloud fax solution must implement specific technical features.
Encryption Standards: At Rest and In Transit
Encryption is the process of converting information into a code to prevent unauthorized access. For cloud faxing, encryption must occur in two phases:
- In Transit: When a fax is sent from a user’s computer to the cloud server, and then from the server to the recipient, it must be protected by Transport Layer Security (TLS) 1.2 or 1.3. This prevents "man-in-the-middle" attacks where hackers intercept data packets.
- At Rest: Once the fax is received and stored on the cloud provider’s servers, it must be encrypted using Advanced Encryption Standard (AES) with 256-bit keys. This ensures that even if a data center’s physical storage is compromised, the files remain unreadable.
User Authentication and Access Control
HIPAA requires that only authorized personnel have access to ePHI. Secure cloud faxing platforms achieve this through:
- Multi-Factor Authentication (MFA): Requiring a password plus a second form of verification (like a mobile app code or biometric scan).
- Role-Based Access Control (RBAC): Assigning permissions based on a user’s job function. For example, a receptionist might be able to send faxes but not delete them, while an administrator has full control.
- Automatic Session Timeouts: Ensuring that if a workstation is left unattended, the fax portal automatically logs out the user.
Audit Logs and Traceability
Detailed logging is essential for forensic analysis and compliance audits. Every action taken within the fax system—logging in, viewing a fax, sending a document, or changing a password—must be recorded in an immutable audit log. These logs must include the user identity, the date and time of the action, and the specific data accessed. According to HHS guidelines, these records must be maintained for at least six years.
Comparing Leading HIPAA Compliant Cloud Fax Providers in 2026
The following table summarizes the capabilities of top-tier providers currently serving the healthcare sector.
| Provider Feature | SRFax Healthcare | RightFax Cloud | mFax by Bitly | Concord Technologies |
|---|---|---|---|---|
| BAA Offered | Yes (Standard) | Yes (Enterprise) | Yes (Healthcare Plan) | Yes (Standard) |
| Encryption (Rest) | AES-256 | AES-256 | AES-256 | AES-256 |
| Authentication | MFA / SSO | SSO / Active Directory | MFA / SSO | MFA / SSO |
| API Integration | High (REST API) | High (SDKs) | Moderate | High (Direct Interop) |
| Storage Limits | Unlimited (Tiered) | Custom / Enterprise | Tiered | Tiered / Custom |
| Compliance Focus | HIPAA/SOC 2 Type II | HIPAA/PCI-DSS | HIPAA/HITRUST | HIPAA/SOC 2 Type II |
Implementation Steps for Healthcare Organizations
Transitioning to a secure cloud faxing solution requires more than just a software subscription; it involves a systematic approach to change management and security configuration.
Phase 1: Needs Assessment and Vendor Selection
Begin by auditing your current fax volume and identifying where PHI is most vulnerable. Evaluate vendors based on their security certifications, such as SOC 2 Type II or HITRUST CSF, which provide third-party validation of their security controls. Always verify the vendor's willingness to sign a BAA before proceeding with a trial.
Phase 2: Configuration and Security Hardening
Once a vendor is selected, configure the system to its maximum security settings. Disable any "legacy" features that allow unencrypted transmissions. For example, if the service offers "email-to-fax," ensure it is configured to use encrypted SMTP or forced TLS. Set up Single Sign-On (SSO) if your organization uses an identity provider like Microsoft Azure AD or Okta to centralize user management.
Phase 3: Workflow Integration
Integrate the cloud fax service with your existing EHR system. Many modern providers offer "print-to-fax" drivers or direct API integrations that allow clinicians to send faxes directly from the patient’s digital chart. This reduces the risk of manual errors and ensures that sent faxes are automatically archived within the patient's record.
Phase 4: Training and Policy Updates
Technological safeguards are only effective if users follow proper protocols. Update your organization’s HIPAA policies to include cloud faxing procedures. Train staff on how to verify recipient numbers, how to handle failed transmissions, and the importance of never sharing login credentials.
Cost Analysis and ROI of Cloud vs. Analog Faxing
While secure cloud faxing involves a monthly subscription fee, the return on investment (ROI) is often significantly higher than maintaining analog infrastructure.
- Hardware Elimination: Organizations save on the purchase, maintenance, and repair of physical fax machines and multi-function printers.
- Consumables: The cost of paper, toner, and ink is virtually eliminated.
- Telephony Costs: Cloud faxing operates over the internet, allowing organizations to cancel expensive dedicated analog phone lines.
- Administrative Efficiency: Digital faxes are searchable and easier to file, saving staff hours previously spent scanning and manually indexing paper documents.
- Risk Mitigation: The potential cost of a HIPAA violation—which can reach millions of dollars in 2026—far outweighs the cost of a compliant cloud subscription.
Common Security Risks and Pitfalls
Even with a compliant provider, human error remains the primary cause of data breaches. Organizations must be vigilant against the following risks:
- Wrong Number Errors: Sending a fax to the wrong recipient is a common HIPAA breach. Cloud systems often mitigate this through pre-configured address books and "confirm before send" prompts.
- Unsecured Endpoints: If a user accesses the cloud fax portal from an unsecured public Wi-Fi or a personal device without encryption, the data is at risk. Organizations should enforce Mobile Device Management (MDM) policies.
- Shadow IT: Employees may sometimes use free, non-compliant fax apps because they are "easier." Strict policy enforcement and providing user-friendly compliant tools are necessary to prevent this.
- Incomplete Deletion: When decommissioning an old cloud fax account, ensure all stored PHI is either migrated or securely deleted according to NIST SP 800-88 guidelines for media sanitization.
Frequently Asked Questions
Can I use a standard email service to send faxes if I have a HIPAA compliant fax provider?
Only if the email transmission itself is encrypted. Standard email is typically not HIPAA compliant because it travels through various servers in plain text. To send faxes via email securely, you must use a provider that supports forced TLS or provides a dedicated secure portal for document uploads.
Does the recipient also need to have a secure cloud fax service for the transmission to be compliant?
No. The HIPAA Security Rule focuses on the sender’s responsibility to protect the data during transmission. Once the fax reaches the recipient’s system, it becomes their responsibility to manage it according to their own compliance protocols. However, the sender must ensure the destination number is correct.
Is "HIPAA Certified" software a real thing?
No. The U.S. Department of Health and Human Services (HHS) does not certify software or service providers as "HIPAA compliant." Compliance is a matter of how the software is configured and used within an organization’s broader security framework. When a vendor says they are "certified," they usually mean they have undergone a third-party audit (like SOC 2) that aligns with HIPAA requirements.
How long should I keep faxes stored in the cloud?
HIPAA requires healthcare organizations to retain certain documentation for six years from the date of its creation or the date when it was last in effect. While the cloud provider may store these for you, it is best practice to move these documents into your primary EHR or a long-term secure archive and then delete them from the fax portal to minimize the "data footprint."
Can I port my existing fax number to a cloud service?
Yes. In almost all cases, current regulations allow for "Local Number Portability" (LNP). You can move your existing healthcare fax number from a traditional carrier to a secure cloud provider, ensuring continuity for your patients and partners who already have your number on file.
Strategic Recommendation
For healthcare organizations operating in 2026, the transition to HIPAA compliant secure cloud faxing is no longer optional; it is a fundamental requirement for operational security and regulatory adherence. To begin, perform a thorough audit of your current communication workflows. Select a vendor that not only provides AES-256 encryption but also prioritizes a transparent BAA and offers HITRUST-certified infrastructure. By integrating these services directly into your EHR and enforcing multi-factor authentication, you can protect patient privacy while significantly reducing the administrative burden of traditional paper-based faxing.
Image Gallery
Select an image to open it in a new tab.
Zara El-Hashem
Sociocultural Dynamics and Academics Writer
