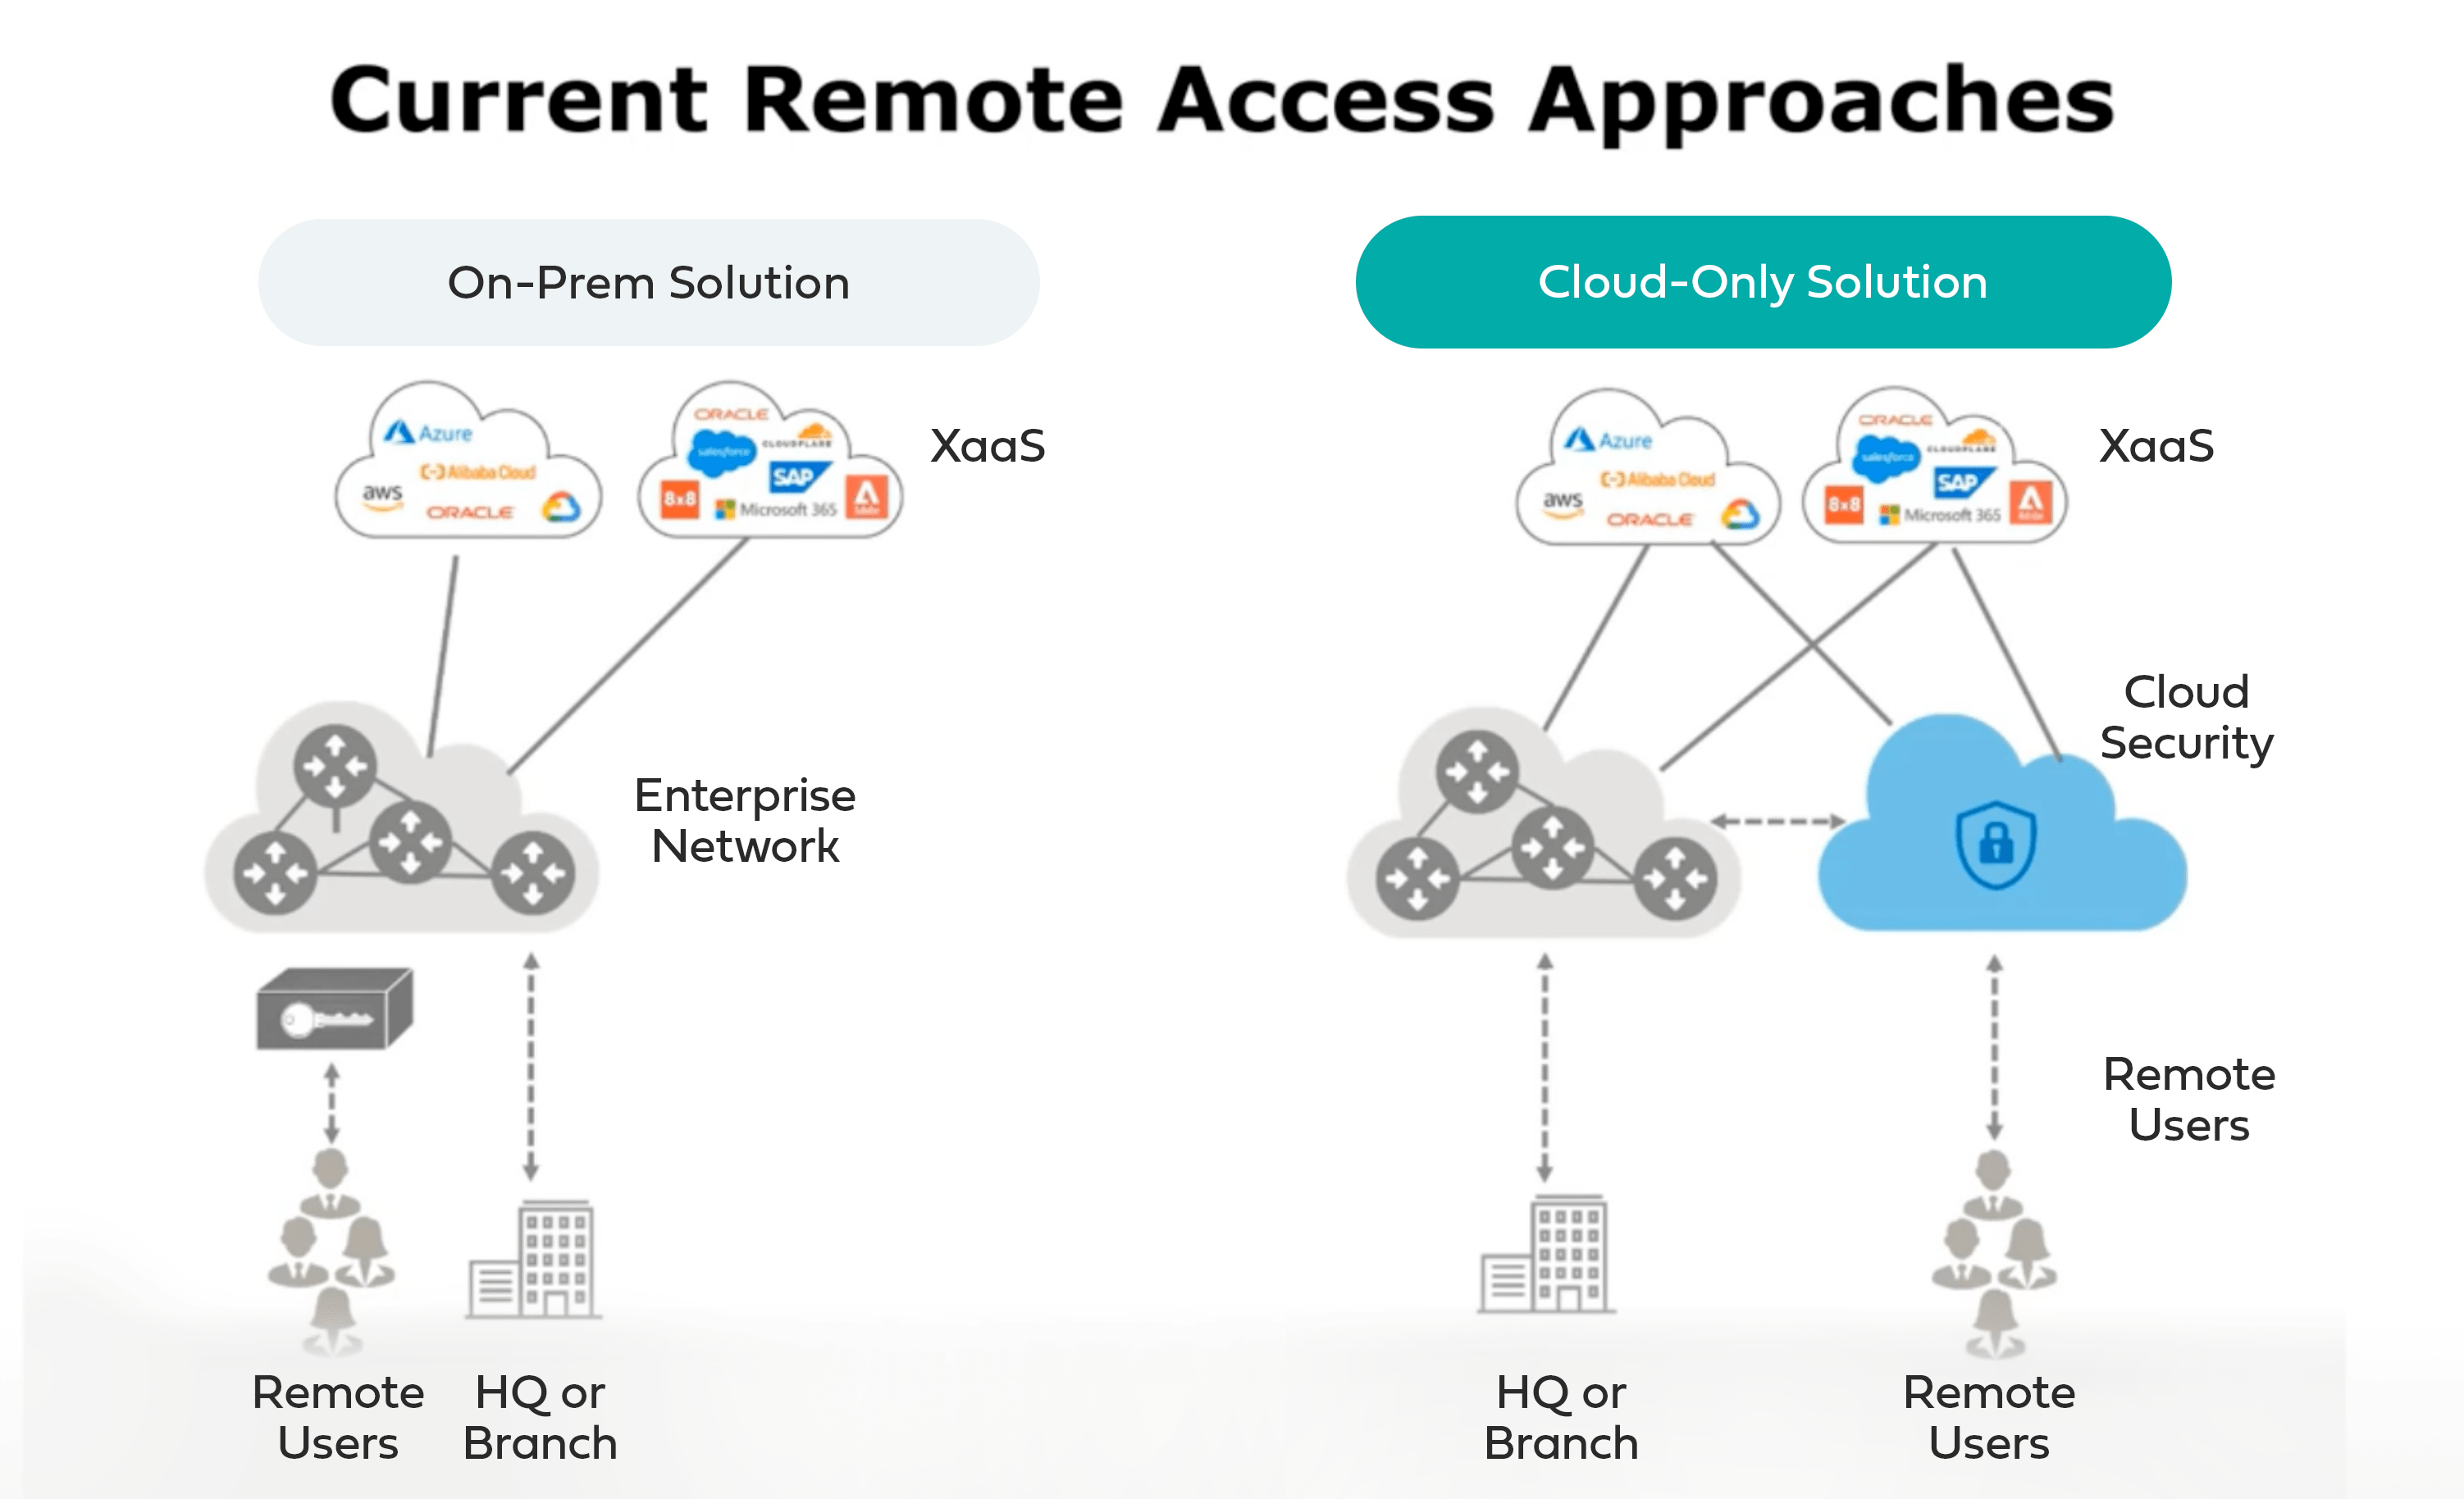
Setting up remote access for the XR2 interface—typically associated with specific enterprise-grade industrial controllers or custom embedded media management systems—requires a structured approach to network authentication, port forwarding, and security protocol enforcement. This process enables authorized users to interface with the XR2 control module from an external network, ensuring that operational commands and data monitoring remain accessible outside the local area network (LAN) environment.
Understanding the XR2 Architecture and Remote Access Requirements
Before attempting to establish remote access, it is critical to understand the architecture of the XR2 system. The XR2 is generally deployed in environments where low-latency command execution and hardware monitoring are paramount. Because these systems often function as headless servers or controller nodes, they rely on a web-based GUI or a specialized binary communication protocol to facilitate remote interaction.
Remote access to an XR2 unit is not a simple "plug-and-play" operation. Because these devices often manage critical infrastructure or sensitive hardware, they are typically configured with strict firewall rules that block unsolicited inbound traffic. To successfully configure remote access, you must satisfy several prerequisite conditions:
- Static IP Assignment: The XR2 device must have a static IP address assigned within your local network. Relying on DHCP is problematic because a lease renewal could change the IP address, effectively breaking your remote connection.
- Network Hardware Compatibility: Your router or firewall must support Port Forwarding or, preferably, the establishment of a Virtual Private Network (VPN) tunnel.
- Authentication Protocols: The XR2 interface must have its own internal security layer, such as password-protected access or multi-factor authentication, to prevent unauthorized control of the hardware once the port is exposed or the tunnel is established.
- Public IP Status: You must determine if your Internet Service Provider (ISP) provides a static public IP address. If your public IP is dynamic, you will require a Dynamic DNS (DDNS) service to ensure your remote connection string remains updated.
Step-by-Step Configuration for XR2 Remote Access
The most secure and recommended method for accessing an XR2 system remotely is through a VPN rather than direct port forwarding. Exposing a device directly to the public internet via port forwarding increases the risk of brute-force attacks and unauthorized exploitation. The following steps outline the setup process using a secure tunnel approach.
1. Configure the Static Local IP
Log into your local router's administrative dashboard. Navigate to the DHCP Reservation or Static IP settings section. Identify your XR2 device by its MAC address and assign it a permanent, non-conflicting IP address within your subnet (e.g., 192.168.1.50). Once saved, reboot the XR2 to ensure it adopts the new address consistently.
2. Establish a VPN Tunnel
Rather than forwarding a raw port to the device, configure a VPN server on your home or office router (such as an OpenVPN or WireGuard server).
- Generate Credentials: Create a user profile within the router’s VPN settings.
- Install Client Software: Download the corresponding VPN client onto your remote computer or mobile device.
- Configure Tunneling: Import the configuration file into your client. When activated, this tunnel places your remote device "virtually" onto your local network, allowing you to access the XR2 via its local IP (192.168.1.50) as if you were physically present.
3. Implementing Port Forwarding (Alternative Method)
If you cannot use a VPN, you may use port forwarding, though this is inherently less secure.
- Identify the Service Port: Consult your XR2 technical manual to find the specific port the service uses (often 80, 443, or a custom port like 8080).
- Create a Rule: In your router’s "Port Forwarding" or "Virtual Server" section, create a new rule.
- Map Traffic: Direct all incoming traffic on a chosen external port (e.g., 50050) to the internal IP of the XR2 on its specific service port.
- Verify Access: Test the connection by navigating to your Public IP address followed by the external port (e.g., http://your-public-ip:50050).

Comparative Analysis: Remote Access Methods
The choice between a VPN and direct port forwarding significantly impacts the security posture of your XR2 deployment.
| Feature | VPN (Recommended) | Port Forwarding |
|---|---|---|
| Security Level | High (Encrypted Tunnel) | Low (Exposes Port to Web) |
| Complexity | Moderate to High | Low |
| Ease of Use | Requires Client App | Browser-based |
| Exposure Risk | Minimal | High (Vulnerable to Scans) |
| Performance | High (depending on tunnel) | Direct |
Troubleshooting Common Connectivity Issues
When remote access fails, the issue usually lies in a misconfiguration of the network layer or an authentication block on the device itself.
The Connection Timeout
If you receive a connection timeout, the most likely cause is an incorrect IP address or a closed port. Check your router’s Port Forwarding logs to see if traffic is hitting the router but being dropped. If using a VPN, verify that the tunnel is "Handshaking"—if the status stays at "Connecting," your credentials or the router’s VPN service settings are likely incorrect.
Authentication Failures
If you can reach the interface but cannot log in, the XR2 may be configured to restrict access based on the source IP. Ensure that the XR2 firewall settings (if applicable) allow connections from the VPN subnet. Many XR2 systems are hardened to block "non-local" traffic; you may need to adjust the device’s internal access control list (ACL) to include your VPN’s virtual IP range.
DDNS Sync Problems
If your connection works for a few days and then stops, your ISP has likely rotated your public IP address. Access your router's DDNS settings and ensure it is communicating correctly with your provider. Ensure the DDNS client is active and that the "Last Update" timestamp is recent.
Security Best Practices for Remote Management
Exposing hardware to the internet requires a defense-in-depth strategy. Even when using a VPN, you should treat the XR2 as a high-value asset.
- Firmware Updates: Regularly check for firmware releases for your XR2. Vulnerabilities in the web interface are common targets for automated exploit bots.
- Disable Default Credentials: Never leave the default administrative password on your XR2. Use a unique, complex passphrase.
- Limit Login Attempts: If the XR2 supports it, enable an account lockout policy that disables the login page after five failed attempts.
- Use Non-Standard Ports: If you must use port forwarding, map the internal port to an obscure external port (e.g., 49212) to reduce the likelihood of being identified by port scanners looking for standard administrative ports.
Frequently Asked Questions
Is it safe to leave XR2 remote access enabled 24/7?
It is generally safe if you are using a VPN tunnel. If you are using port forwarding, it is not recommended unless you have an exceptionally robust firewall and keep the device firmware strictly updated. A VPN adds a layer of encryption and authentication that significantly mitigates risk.
Do I need a static IP address from my ISP to reach my XR2?
You do not strictly need a static IP, but it is highly recommended. If you have a dynamic IP, you must use a DDNS service, which acts as a bridge, mapping a domain name (e.g., mydevice.ddns.net) to your current IP address, ensuring your connection remains stable even when the ISP changes your address.
Can I access the XR2 via a mobile app?
Many XR2 iterations offer companion mobile applications for monitoring. If the app supports remote functionality, you typically just need to point the app to your DDNS address or the VPN tunnel's IP address. Always check the official documentation to see if the app requires a specific port to be opened.
Why is my port forwarding rule not working?
First, ensure that your ISP is not utilizing CGNAT (Carrier-Grade NAT). If your router’s WAN IP is in the 100.64.x.x range, you are behind a CGNAT and port forwarding will not work. In this case, a VPN (like Tailscale or ZeroTier) is a necessary alternative to circumvent ISP-level NAT restrictions.
What should I do if my XR2 is compromised?
Immediately disconnect the device from the network to prevent lateral movement to other connected hardware. Perform a factory reset, update the firmware to the latest version, change all administrative passwords, and audit your router’s configuration to remove any suspicious port forwarding rules.
Recommended Next Actions
To successfully implement your remote access solution, begin by verifying your router's capabilities. Log into your router’s administrative console and check for "VPN Server" or "OpenVPN/WireGuard" options. If these are available, prioritize configuring these over simple port forwarding. Once established, test your connection from a cellular network (disconnecting from your local Wi-Fi) to ensure the tunnel correctly simulates an external remote environment. If your router lacks these features, consider upgrading to a firmware version that supports them or adding a dedicated hardware firewall to your network.
Image Gallery
Select an image to open it in a new tab.


Lars Thomsen
Global Labor Markets and Economic Strategy Editor
