
Investment advisors managing sensitive client financial records require secure cloud storage that complies with regulatory frameworks like SEC Rule 204-2 (the Books and Records Rule) and FINRA guidelines. This infrastructure must integrate AES-256 encryption, zero-knowledge architecture, multi-factor authentication, robust access controls, and immutable audit logs to protect personally identifiable information against unauthorized access and cyber threats.
Selecting and maintaining secure cloud storage for investment advisors in practice is an essential operational requirement. Registered Investment Advisors (RIAs) and broker-dealers handle vast amounts of sensitive client data, including Social Security numbers, tax returns, account statements, and strategic financial plans. Transitioning from legacy on-premises servers to modern cloud environments offers operational flexibility, scalability, and enhanced disaster recovery capabilities. However, this shift also introduces complex cybersecurity challenges and strict regulatory oversight. Financial professionals cannot rely on consumer-grade file-sync-and-share applications. Instead, they must implement enterprise-grade solutions specifically engineered to meet high standards of confidentiality, integrity, and availability.
Regulatory Landscape and Compliance Requirements
Investment advisors operate under stringent regulatory scrutiny regarding how they collect, transmit, store, and dispose of electronic records. Understanding these mandates is the first step in designing a secure data storage infrastructure.
SEC Rule 204-2 and the Books and Records Rule
The Securities and Exchange Commission (SEC) mandates under Rule 204-2 that investment advisors retain all books and records relating to their investment advisory business in an easily accessible place for a specified number of years. When these records are maintained in electronic format, the SEC expects advisors to implement controls that prevent unauthorized alteration or destruction. Furthermore, advisors must be able to produce these records promptly during an examination. Cloud storage solutions must support this by maintaining version histories, undeletable archival tiers, and rapid retrieval mechanisms.
FINRA Regulations on Electronic Records
While the Financial Industry Regulatory Authority (FINRA) primarily regulates broker-dealers, many dual-registrants or advisors affiliated with broker-dealers must adhere to FINRA guidelines, particularly Rule 4511. This rule mirrors SEC recordkeeping standards and historically required records to be stored in a "Write Once, Read Many" (WORM) format. Modern cloud storage providers comply with WORM requirements by offering immutable object storage buckets that physically or logically lock data against modification or deletion for a predetermined retention period, regardless of user privileges.
Privacy Frameworks: Regulation S-P and Beyond
Regulation S-P (Privacy of Consumer Financial Information and Safeguard Policies) requires financial institutions to adopt written policies and procedures addressing administrative, technical, and physical safeguards for customer records. Secure cloud storage acts as a critical technical safeguard. Advisors must ensure their cloud vendors sign Business Associate Agreements (BAAs) where applicable, or provide comprehensive Service Organization Control (SOC) 2 Type II reports validating their security controls. State-level regulations, such as the California Consumer Privacy Act (CCPA) and various state data security laws, further reinforce these mandates.
Core Technical Specifications for Financial Cloud Storage
Not all cloud storage platforms are created equal. To safeguard client assets and maintain compliance, investment advisors must verify that their chosen storage architecture incorporates specific technical controls.
- End-to-End Encryption (AES-256 & Zero-Knowledge Keys)
- Identity & Access Management (MFA, RBAC, SSO)
- Immutable Storage / WORM Compliance
- Comprehensive Audit Logging & Monitoring
Encryption Standards: In-Transit and At-Rest
Data must be encrypted continuously. At-rest encryption should utilize Advanced Encryption Standard (AES) with 256-bit keys, the gold standard for protecting classified information. In-transit encryption must rely on modern Transport Layer Security (TLS 1.3) protocols to prevent interception during synchronization and file sharing. Crucially, advisors should evaluate whether the provider employs zero-knowledge architecture. In a zero-knowledge model, the cloud provider does not possess the decryption keys; only the advisor or firm holds the master key, preventing unauthorized data access even by cloud infrastructure administrators.
Access Control and Authentication
Granular access control is vital for preventing lateral movement within a compromised network. Secure platforms implement Role-Based Access Control (RBAC), ensuring that junior staff, compliance officers, and senior partners only access folders and files necessary for their specific job functions. Multi-Factor Authentication (MFA)—preferably utilizing hardware security keys (FIDO2/WebAuthn) or time-based one-time passwords (TOTP)—must be enforced across all user accounts. Single Sign-On (SSO) integrations with identity providers (IdPs) like Okta or Azure AD streamline user lifecycle management while maintaining strict security perimeters.
Audit Trails and Activity Logging
Regulators frequently examine whether a firm can reconstruct past actions or investigate potential data breaches. Secure cloud storage solutions must generate immutable audit logs that record every user action, including file creation, modification, deletion, sharing link generation, and login attempts. These logs should feed directly into Security Information and Event Management (SIEM) tools or centralized logging platforms to enable real-time anomaly detection and alert generation.

Evaluating Consumer vs. Enterprise vs. Specialized Cloud Storage
Investment advisors often struggle with choosing the right tier of cloud infrastructure. The following table contrasts common storage categories across dimensions critical to financial advisory practices.
| Evaluation Metric | Consumer Cloud Storage (e.g., Standard Consumer Drives) | Enterprise General Cloud Storage (e.g., Enterprise Sync Tools) | Specialized Financial Cloud Storage (e.g., FinTech Vaults) |
|---|---|---|---|
| Encryption Model | Provider-managed keys; potential decryption by platform. | Robust at-rest/in-transit; optional customer-managed keys. | Zero-knowledge architecture; client-held encryption keys. |
| Regulatory Compliance | Generally unsuitable; lacks formal SEC/FINRA readiness. | Configurable for compliance; requires careful administrative setup. | Out-of-the-box compliance documentation and WORM support. |
| Client Portal Integration | Typically limited to basic, unsecured link-sharing. | Moderate; requires third-party add-ons for secure portals. | Built-in secure client intake portals and encrypted messaging. |
| Audit & Reporting | Minimal logging; basic activity feeds. | Detailed administrative consoles and log exporting. | Comprehensive, immutable audit trails tailored for audits. |
| Cost Structure | Low monthly subscription or freemium model. | Moderate per-user monthly licensing fees. | Premium pricing reflecting specialized security features. |
Implementation Roadmap for Investment Advisory Practices
Migrating an advisory practice's file repository to a secure cloud environment requires a methodical approach to minimize business disruption and maintain regulatory compliance.
Phase 1: Data Discovery and Classification
Before moving files, advisors must audit existing data stores. Catalog all client files, research reports, operational documentation, and compliance archives. Classify data based on sensitivity:
- Restricted: Client PII, social security numbers, account numbers, tax documents.
- Confidential: Internal financial models, proprietary trading strategies, employee records.
- Internal: General operational procedures, templates, marketing collateral.
This classification dictates which files require the highest encryption tiers and strictest access controls.
Phase 2: Vendor Selection and Due Diligence
Select a cloud storage vendor that aligns with the firm's size, technical expertise, and regulatory obligations. Request and review the vendor’s SOC 2 Type II audit reports, ISO/IEC 27001 certifications, and penetration testing summaries. Verify data residency options to ensure that client data remains within authorized geographic jurisdictions (e.g., United States-based data centers for SEC-regulated entities). Establish a formal Service Level Agreement (SLA) covering uptime guarantees, data redundancy, and breach notification timelines.
Phase 3: Policy Formulation and User Training
Technology alone cannot guarantee security. Advisors must update their written supervisory procedures (WSPs) to reflect the new cloud storage workflow. Explicitly define acceptable use policies, prohibit the use of unapproved shadow IT tools (such as personal consumer storage accounts or unencrypted messaging apps), and establish protocols for secure external collaboration. Conduct mandatory cybersecurity training for all personnel, emphasizing phishing recognition, credential hygiene, and the importance of reporting suspicious activity immediately.
Phase 4: Migration, Testing, and Decommissioning
Execute the data migration in phases, beginning with non-sensitive internal documents before moving active client vaults. Maintain strict chain-of-custody documentation during the transfer. Test data integrity by verifying checksums post-migration. Conduct simulated retrieval drills to ensure staff can access records quickly under examination conditions. Once verification is complete, securely wipe and decommission legacy hard drives or servers in accordance with NIST SP 800-88 guidelines for media sanitization.
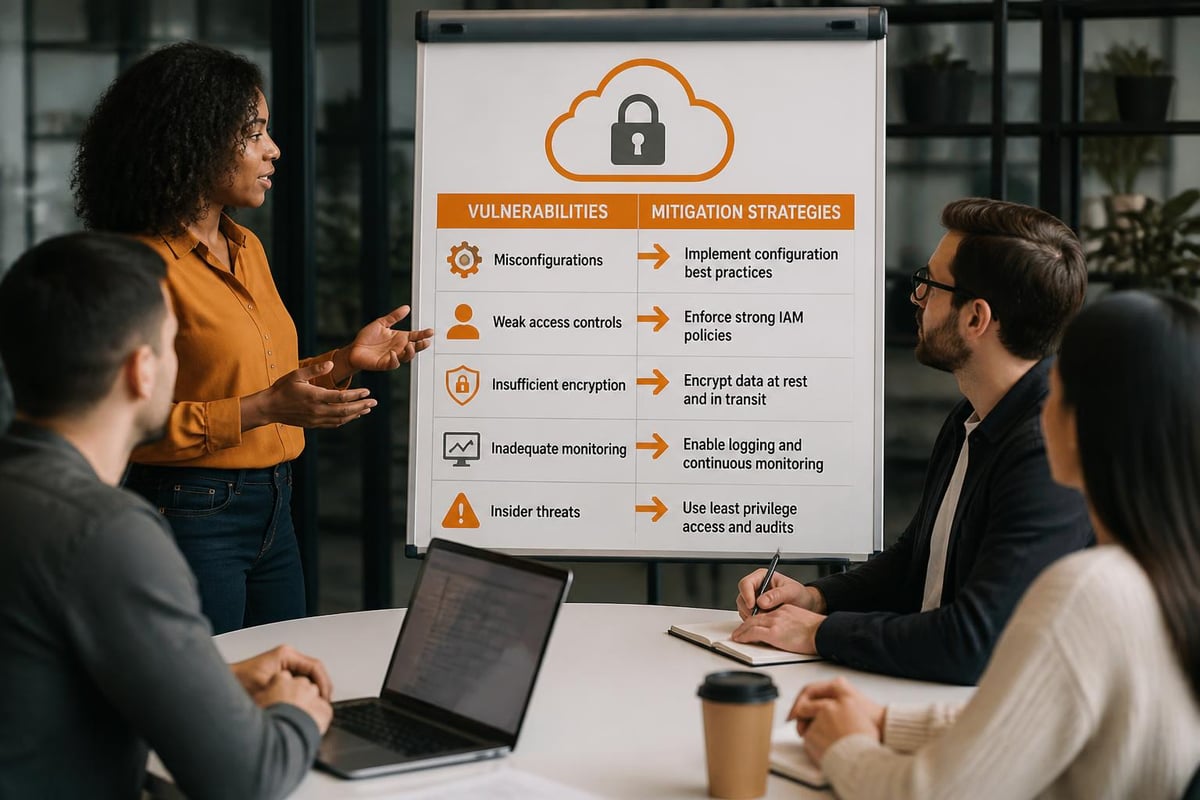
Common Operational Pitfalls and Mitigation Strategies
Advisory practices frequently encounter avoidable obstacles when deploying cloud storage. Recognizing these pitfalls helps maintain operational resilience.
Over-Reliance on Default Vendor Settings
Many cloud platforms ship with permissive default settings designed for ease of use rather than maximum security. Public link sharing, open folder permissions, and disabled MFA are common out-of-the-box vulnerabilities. Mitigation: Implement a hardening checklist, disable public link generation globally, and require explicit administrator approval for external sharing permissions.
Inadequate Backup and Disaster Recovery Redundancy
A common misconception is that storing data in the cloud eliminates the need for backups. Cloud providers protect against hardware failure and data center outages, but they do not inherently protect against user error, malicious deletion, or ransomware encryption that propagates across synchronized folders. Mitigation: Implement automated, air-gapped or immutable secondary backups independent of the primary cloud storage repository.
Neglecting Offboarding and Access Revocation
When employees or independent contractors leave an advisory firm, failure to instantly revoke cloud access creates significant vulnerability windows. Mitigation: Integrate cloud storage access controls with centralized identity management systems to automate offboarding and ensure immediate credential invalidation across all applications.
Frequently Asked Questions
Can investment advisors use standard consumer cloud storage for client data?
Using standard consumer cloud storage violates SEC and FINRA expectations regarding the safeguarding of non-public personal information. Consumer platforms typically lack enterprise-grade encryption key management, robust audit logging, immutable storage tiers, and formal compliance certifications like SOC 2 Type II. Advisors should use dedicated enterprise or specialized financial cloud solutions.
What is WORM storage, and why is it necessary for RIAs?
WORM stands for "Write Once, Read Many." It is a data storage technology that prevents files from being altered or deleted once written, until a predetermined retention period expires. It is necessary for investment advisors because regulatory bodies like the SEC and FINRA mandate that certain records be maintained in unalterable formats to prevent tampering or spoliation during investigations.
How does zero-knowledge encryption protect an advisory firm?
Zero-knowledge encryption ensures that the cloud storage provider cannot decrypt or view the files stored on their servers because the encryption keys are held exclusively by the client. Even if the cloud provider's servers suffer a data breach or are subpoenaed, the underlying data remains unreadable without the advisor's master decryption key.
What documentation should an advisor request from a cloud vendor during due diligence?
Advisors should request a recent SOC 2 Type II report covering security, availability, and confidentiality trust services criteria. Additionally, firms should review ISO 27001 certifications, penetration testing summaries conducted by third-party auditors, business continuity and disaster recovery plans, and details regarding data residency and encryption key management.
How often should access permissions to client cloud storage be reviewed?
Access permissions should be audited at least quarterly, as well as immediately following any staffing changes, role transitions, or organizational restructuring. This ensures that the principle of least privilege is maintained and that former employees or external contractors no longer retain access to sensitive client portfolios.
Conclusion and Next Actions
Securing cloud storage is a foundational pillar of modern investment advisory practice. By moving beyond consumer-grade applications and establishing robust technical controls—such as zero-knowledge encryption, multi-factor authentication, and immutable WORM storage—advisors protect their clients' sensitive data while satisfying strict SEC and FINRA regulatory mandates. To begin, conduct an immediate data inventory, review existing vendor agreements against compliance standards, and establish comprehensive written supervisory procedures to govern cloud usage across the firm.
Image Gallery
Select an image to open it in a new tab.

Omar Farooq
EdTech Innovation and Virtual Pedagogy Journalist
