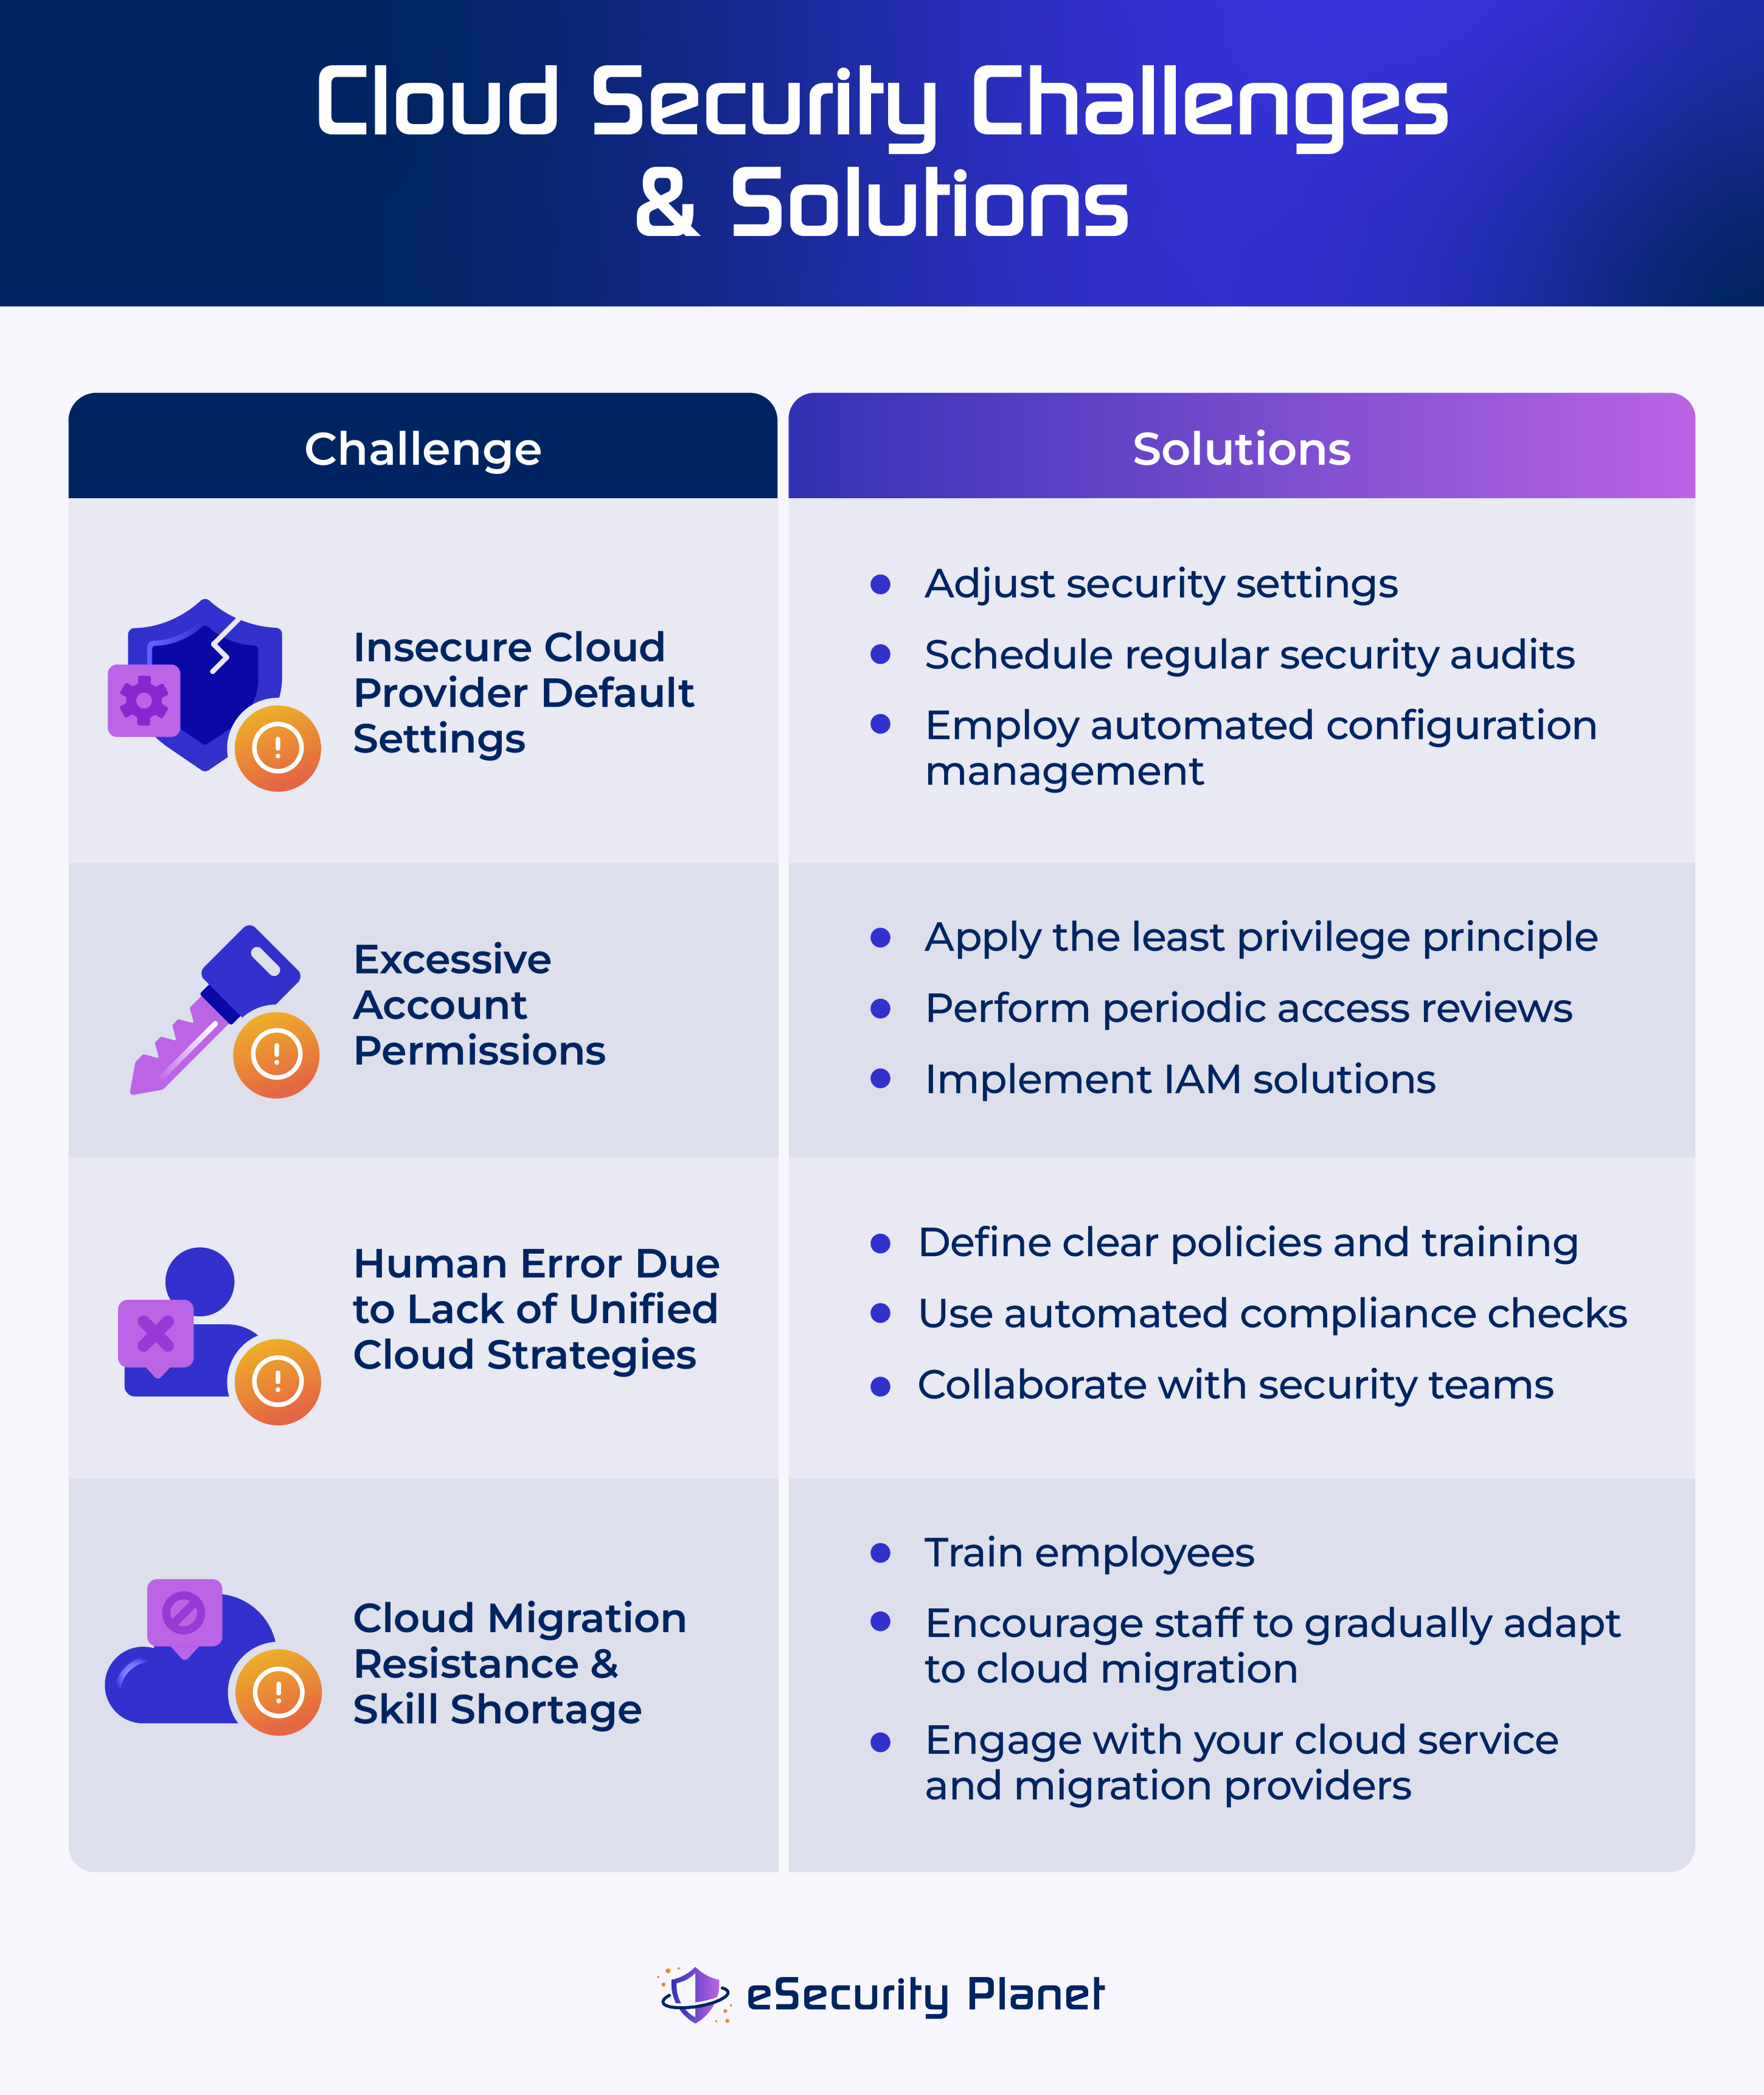
The cloud computing security issue matters because it represents the primary defense mechanism for the world’s most critical data, infrastructure, and services. As of 2026, cloud environments host the vast majority of enterprise workloads, meaning a single security failure can lead to massive data theft, catastrophic financial losses, and the total cessation of essential business operations.
The Centrality of Cloud Infrastructure in 2026
By 2026, the transition from on-premises hardware to cloud-native environments is nearly universal for mid-to-large-scale enterprises. This shift has fundamentally changed the perimeter of cybersecurity. In the past, security was defined by physical walls and local firewalls; today, the perimeter is identity-based and distributed across global data centers.
The reason this issue matters so urgently is that the cloud is no longer just a storage repository. it is the engine for artificial intelligence (AI), the backbone of the Internet of Things (IoT), and the platform for critical infrastructure, including power grids and healthcare systems. When cloud security is compromised, the impact is not localized to a single server—it ripples through interconnected APIs, third-party integrations, and global supply chains.
The complexity of these environments has outpaced the traditional security skill sets of many IT departments. Multi-cloud and hybrid-cloud strategies are now standard, which increases the "attack surface"—the total number of points where an unauthorized user can enter or extract data. Managing security across different providers like AWS, Microsoft Azure, and Google Cloud requires a unified strategy that many organizations still struggle to implement effectively.
The Shared Responsibility Model: A Critical Misunderstanding
One of the most persistent reasons why the cloud computing security issue matters is the widespread misunderstanding of the Shared Responsibility Model. Many business leaders incorrectly assume that once they migrate to a major cloud provider, the provider is responsible for all security.
In reality, cloud security is a partnership. The Cloud Service Provider (CSP) is responsible for the security of the cloud (the physical data centers, the underlying hardware, and the virtualization layer). However, the customer is responsible for security in the cloud. This includes:
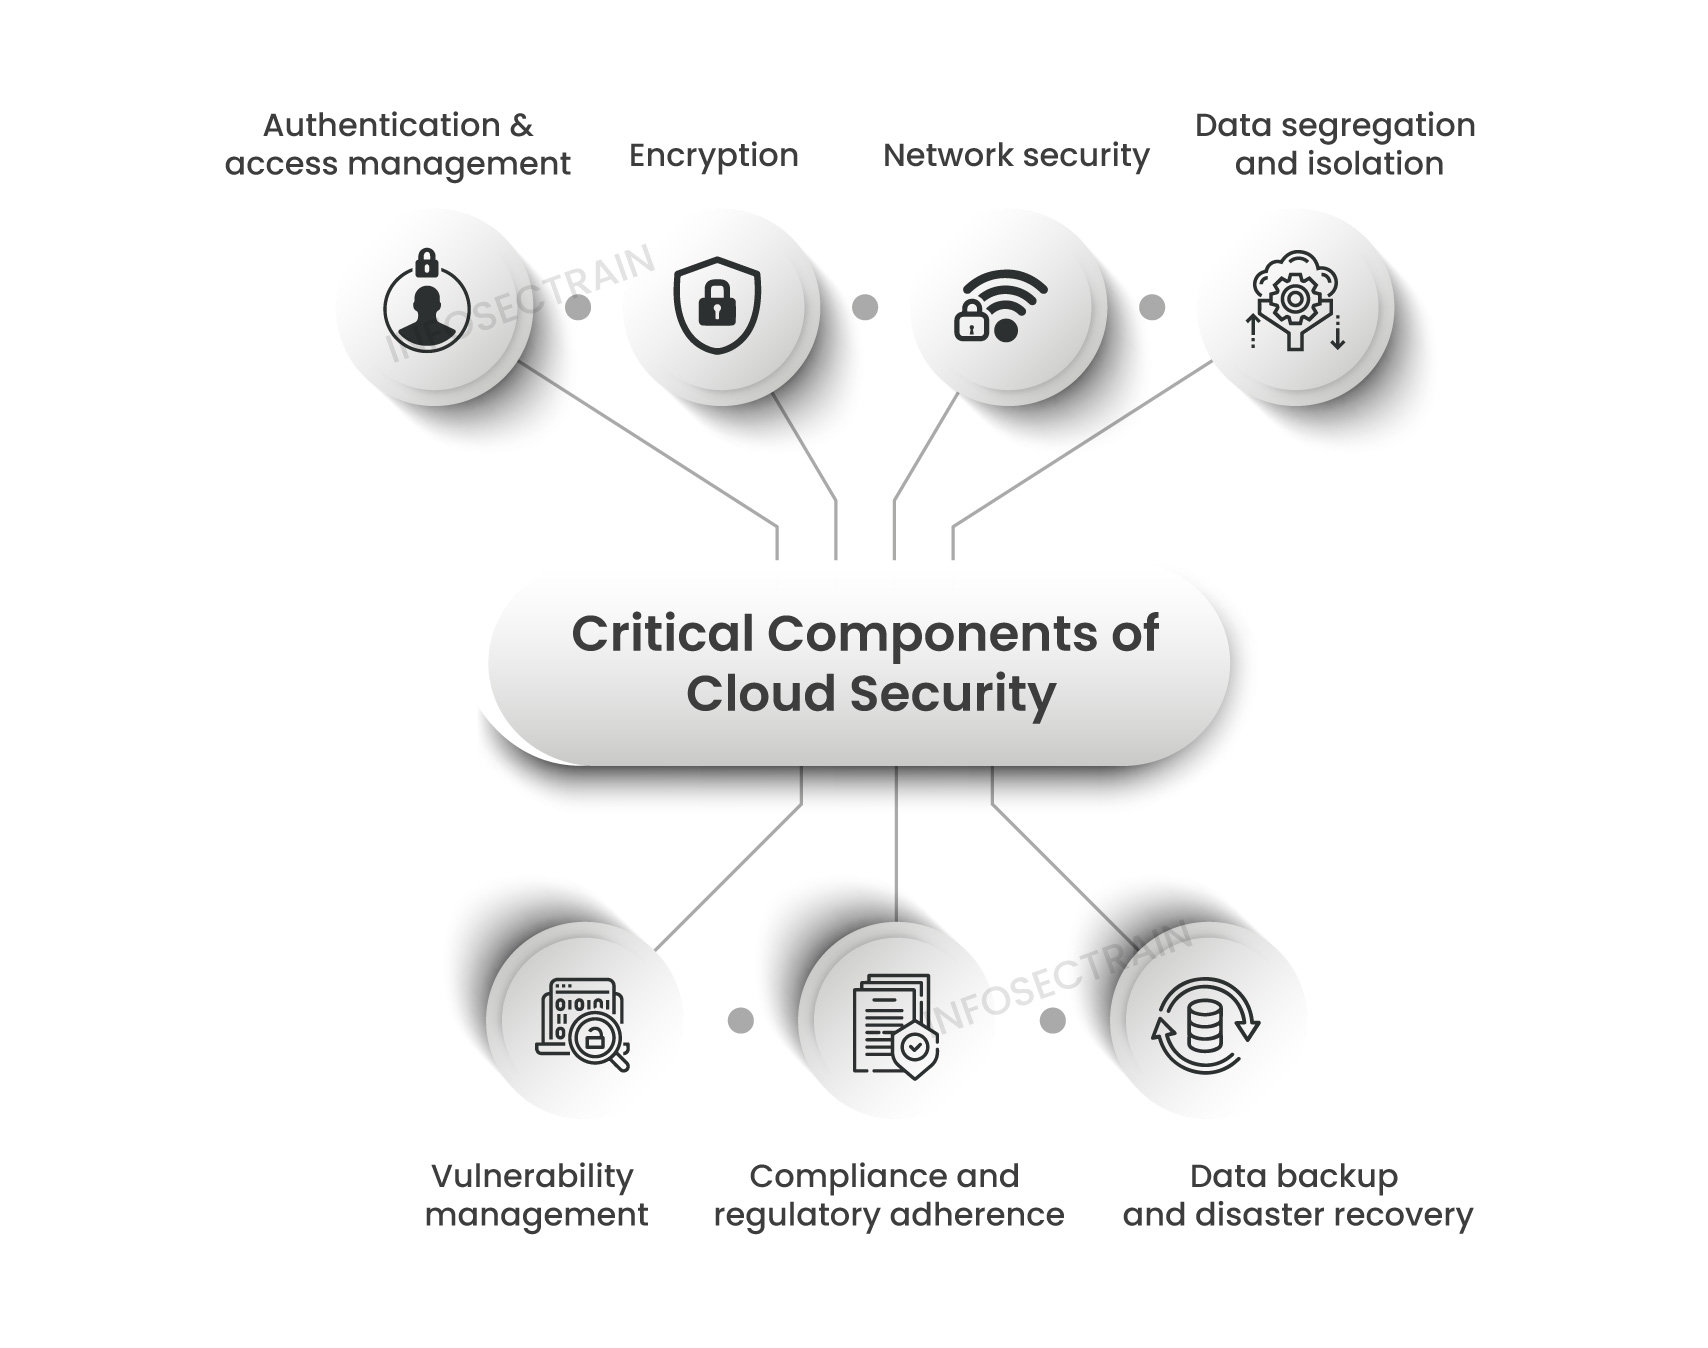
- Data Protection: Encrypting data at rest and in transit.
- Identity and Access Management (IAM): Ensuring only authorized users have access to specific resources.
- Application Security: Patching and securing the software run within the cloud environment.
- Configuration: Properly setting up buckets, databases, and network rules.
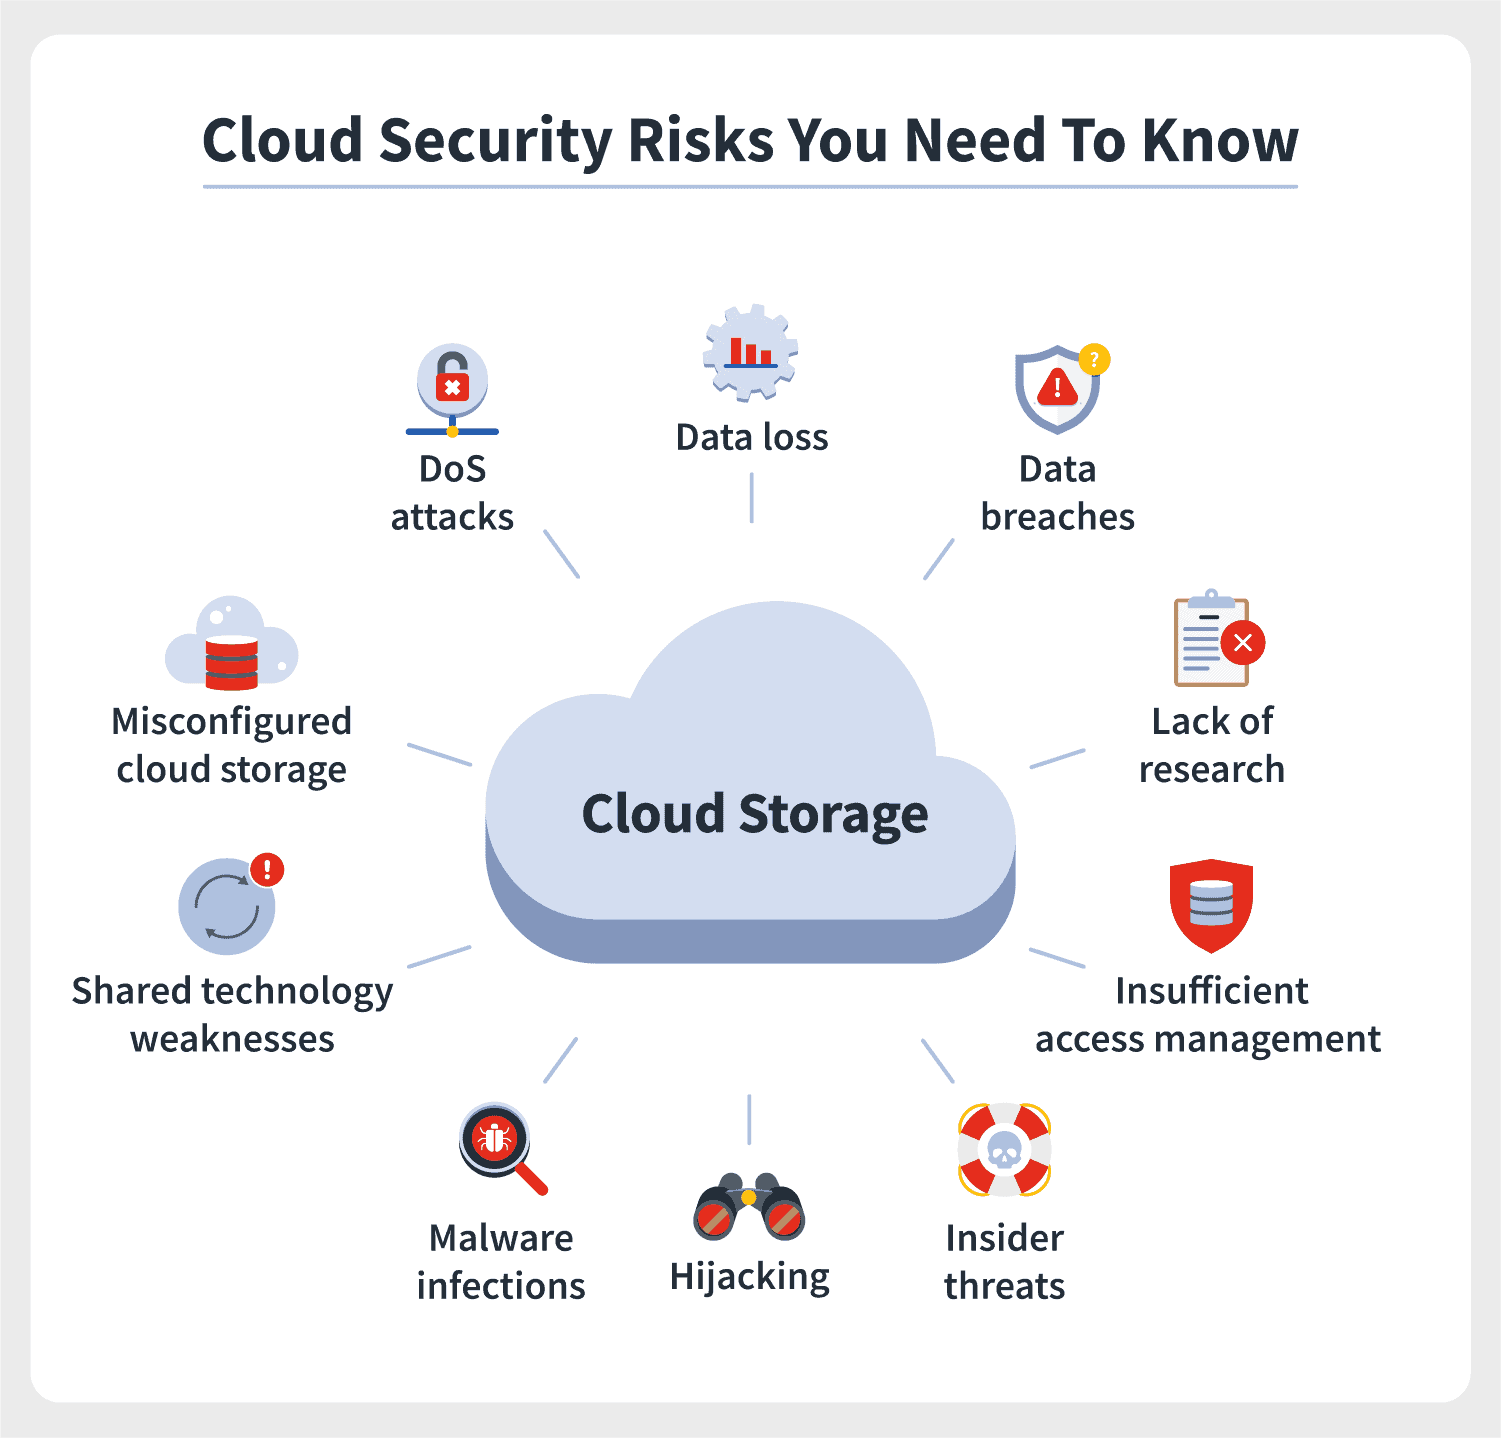
Statistics from the Cloud Security Alliance (CSA) consistently show that the majority of cloud breaches are not the result of a provider's failure, but rather customer misconfigurations. A single "publicly readable" setting on an S3 bucket or an exposed API key can lead to the exposure of millions of records.

Regulatory Compliance and the Legal Weight of Security
In 2026, the legal landscape regarding data privacy has become significantly more punitive. Regulations such as the General Data Protection Regulation (GDPR) in Europe, the California Privacy Rights Act (CPRA), and newer frameworks like the EU AI Act have created a high-stakes environment for data handling.
Cloud security is the technical manifestation of legal compliance. If an organization fails to secure its cloud environment, it is not just a technical error; it is a violation of federal and international law. The fines for non-compliance can reach up to 4% of a company's global annual turnover. Furthermore, 2026 has seen an increase in "class-action" style litigation following data breaches, where consumers hold corporations accountable for negligence in cloud configuration.
Beyond fines, there is the issue of Data Sovereignty. Many nations now require that data generated within their borders stay within those borders. Cloud security teams must implement "geofencing" and specialized encryption to ensure that data does not migrate to unauthorized regions during automated cloud backups or load-balancing processes.
The Economic Impact of Cloud Insecurity
The financial consequences of cloud security failures have reached record highs. According to industry reporting, the average cost of a data breach in 2026 has surpassed $5 million, with cloud-specific incidents often costing more due to the complexity of forensics and the scale of the data involved.
Financial loss manifests in several ways:
- Ransomware Payments: While law enforcement discourages it, many companies still face existential threats from ransomware that encrypts cloud-native backups.
- Operational Downtime: Cloud-based SaaS (Software as a Service) platforms are the lifeblood of modern work. If a security issue takes these offline, productivity drops to zero.
- Reputational Damage: Trust is the hardest asset to rebuild. Once a company is known for "leaky" cloud storage, partners and customers migrate to competitors who demonstrate better security posture.
- Insurance Premiums: Cyber insurance providers in 2026 require rigorous proof of Cloud Security Posture Management (CSPM) before issuing policies. Poor security leads to uninsurable risks or exorbitant premiums.
Modern Technical Threats: AI and Automation
The cloud computing security issue matters because the "adversaries" have evolved. In 2026, hackers are using AI-driven bots to scan the entire IPv4 and IPv6 address space for cloud misconfigurations in minutes.
Automated Vulnerability Discovery means that if you launch a cloud instance with a default password or an open port, it will likely be identified by a malicious actor within seconds. Furthermore, "living off the cloud" attacks have become common. In these scenarios, attackers do not install malware; instead, they use the victim's own cloud management tools (like PowerShell or CLI) to move laterally through the network, making detection by traditional antivirus software nearly impossible.
Comparative Responsibilities Across Cloud Models
To understand why security management varies, it is essential to look at how responsibilities shift depending on the service model used.
| Feature | Infrastructure as a Service (IaaS) | Platform as a Service (PaaS) | Software as a Service (SaaS) |
|---|---|---|---|
| Physical Security | Provider | Provider | Provider |
| Network Infrastructure | Provider | Provider | Provider |
| Operating System | Customer | Provider | Provider |
| Application Logic | Customer | Customer | Provider |
| Identity & Access | Customer | Customer | Customer |
| Data & Content | Customer | Customer | Customer |
| End-point Security | Customer | Customer | Customer |
As shown in the table, regardless of the model, the Customer always retains responsibility for the data and the identities used to access it. This is why "Identity is the new perimeter" is a core tenet of 2026 cybersecurity.
Solving the Issue: The Zero Trust Mandate
To address why cloud security matters, organizations have moved toward a Zero Trust Architecture (ZTA). Zero Trust is a security framework based on the realization that "internal" networks are no longer inherently safe. In a cloud environment, every request for access must be verified, regardless of where it originates.
Implementing Zero Trust involves:
- Micro-segmentation: Breaking the cloud network into small, isolated zones to prevent lateral movement by attackers.
- Least Privilege Access: Giving users only the minimum level of access required to perform their jobs.
- Continuous Monitoring: Using AI-enhanced tools to analyze user behavior in real-time. If a user normally logs in from New York but suddenly attempts to download a database from an IP address in a different country, the system automatically revokes access.
This proactive approach is the only way to manage the inherent risks of cloud computing. Without Zero Trust, a single stolen credential could grant an attacker the "keys to the kingdom."
Practical Steps for Organizations
If you are managing cloud resources in 2026, the following actions are considered mandatory for maintaining a secure posture:
- Enable Multi-Factor Authentication (MFA): Use hardware-based keys or biometrics rather than SMS-based codes, which are susceptible to SIM-swapping.
- Audit Permissions Regularly: Use automated tools to find "zombie" accounts—old employee accounts that were never deactivated.
- Encrypt Everything: Encrypt data at rest using AES-256 and data in transit using TLS 1.3 or higher. Ensure that you, not the provider, manage the encryption keys through a Key Management Service (KMS).
- Implement CSPM Tools: Cloud Security Posture Management tools provide a "single pane of glass" view to identify misconfigurations across multiple cloud providers.
- Develop an Incident Response Plan: Assume a breach will happen. Have a tested plan for how to isolate affected cloud instances and restore from immutable backups.
Frequently Asked Questions
Is the public cloud less secure than on-premises servers?
Not necessarily. Large cloud providers like AWS, Azure, and Google spend billions on security, often far exceeding what a private company can afford. However, the complexity of cloud configuration makes it easier for users to make mistakes. The cloud is "secure by design" but often "insecure by implementation."
What is the most common cause of cloud security breaches?
Misconfiguration remains the leading cause. This includes leaving database ports open to the public internet, failing to enable encryption, and granting overly broad permissions to users or applications.
How does AI affect cloud security in 2026?
AI is a double-edged sword. It allows defenders to detect anomalies and threats at machine speed (AIOps). Conversely, attackers use AI to craft highly convincing phishing emails and to automate the discovery of zero-day vulnerabilities in cloud software.
What is "Shadow IT" and why is it a cloud security risk?
Shadow IT refers to employees using cloud services (like file-sharing apps or project management tools) without the approval or knowledge of the IT department. This creates unmonitored "pockets" of data that do not follow the company’s security or compliance policies.
Can cloud providers see my data?
Most major providers use technical controls to prevent their employees from accessing customer data. However, for maximum security, organizations use "Client-Side Encryption" or "Confidential Computing" (using TEEs - Trusted Execution Environments), which ensures data is encrypted even while it is being processed in the cloud's memory.
Moving Forward: The Future of Cloud Security
The cloud computing security issue matters because it is the foundation of our digital future. As we move further into 2026, the integration of Post-Quantum Cryptography (PQC) will become the next major hurdle as organizations prepare for the threat that quantum computers pose to current encryption standards.
For now, the priority must remain on the basics: visibility, identity, and configuration. Organizations that master these elements will flourish in the cloud, while those that ignore them will face increasingly severe consequences in an unforgiving digital landscape. The goal is to move from a state of "unconscious risk" to "informed resilience."
Image Gallery
Select an image to open it in a new tab.


Zara El-Hashem
Sociocultural Dynamics and Academics Writer
