Securing Cloud Environments with Sherwood Business Security Architecture and SABSA
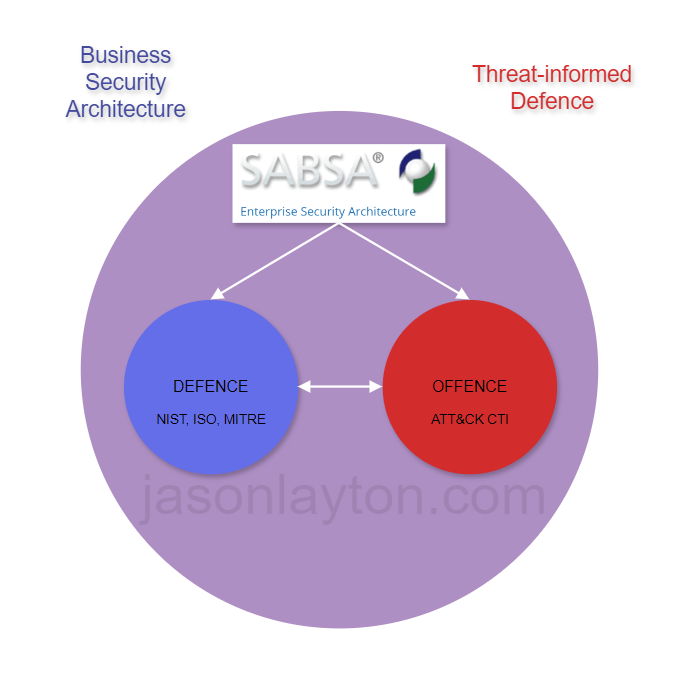
Sherwood Business Security Architecture, combined with the Sherwood Applied Business Security Architecture (SABSA) framework, provides a comprehensive methodology for aligning enterprise cloud security with business objectives, ensuring risk management, governance, and traceability from strategy down to technical implementation.
Introduction to Sherwood Business Security Architecture and SABSA in the Cloud
Modern cloud computing introduces unprecedented agility, scalability, and efficiency to enterprise operations, but it simultaneously expands the digital attack surface. Traditional, perimeter-based security models often fail in decentralized, multi-cloud, and hybrid environments. To address these complex challenges, organizations increasingly turn to structured enterprise security architectures. Among these, the integration of Sherwood Business Security Architecture—built upon the SABSA framework—offers a top-down, business-driven approach to cloud security.
Developed by John Sherwood, Andrew Clark, and David Lynas, SABSA is widely recognized as the Sherwood Applied Business Security Architecture. It mirrors the Zachman Framework for enterprise architecture but focuses exclusively on information security. When applied to cloud environments, SABSA shifts the perspective of security from a purely technical barrier to an enabler of business value. This article explores how organizations can leverage Sherwood Business Security Architecture and SABSA principles to design, implement, and maintain robust cloud security models that scale alongside corporate growth.
Understanding the SABSA Framework and Its Core Philosophy
At its heart, SABSA is not a rigid set of technical controls or compliance checklists; rather, it is a methodology for developing information security architectures that map directly to the needs of the business. The framework operates on the principle that security must be an enabler of business strategy rather than an impediment to productivity.
The architecture is built on a six-layer, six-question matrix. The columns represent the fundamental architectural perspectives—What, How, Where, Who, When, and Why—while the rows represent the abstraction layers, moving from the conceptual executive level down to the physical component level.
| Abstraction Layer | What | How | Where | Who | When | Why |
|---|---|---|---|---|---|---|
| 6. Operational | Assets | Mech. | Loc. | Sub. | Time | Mot. |
| 5. Component | Data | Soft. | Node | User | Sched | Reas. |
| 4. Physical | Inf. | Proc. | Site | Org. | Cycle | Obj. |
| 3. Logical | Schema | App. | Domain | Role | Event | Policy |
| 2. Conceptual | Entity | Func. | Locat. | Act. | Time | Goal |
| 1. Contextual | Asset | Oper. | Place | People | Time | Value |
By applying this matrix to cloud computing, organizations can systematically address every facet of cloud adoption. Instead of asking how to configure a specific Amazon Web Services (AWS) S3 bucket or Microsoft Azure virtual network first, a SABSA-aligned approach begins at the contextual layer by asking why the business is moving to the cloud, what value it aims to create, and who is accountable for the associated risks.

The Six Layers of SABSA Applied to Cloud Architecture
Translating business requirements into secure cloud environments requires traversing each layer of the SABSA framework systematically. Each layer builds upon the previous one, ensuring complete traceability from board-level business goals to cloud infrastructure configurations.
Layer 1: Contextual Architecture (The Business View)
The contextual layer defines the business context and the overarching security strategy. In a cloud migration scenario, this layer identifies the business drivers—such as reducing capital expenditure, increasing operational agility, or entering new geographic markets. Security architects collaborate with executive leadership to establish the risk appetite, regulatory obligations, and strategic value of migrating critical workloads to Infrastructure-as-a-Service (IaaS), Platform-as-a-Service (PaaS), or Software-as-a-Service (SaaS) environments.
Layer 2: Conceptual Architecture (The Architect's View)
At the conceptual level, the security architecture is translated into an abstract model of information flow, business processes, and trust zones. For cloud environments, this involves defining multi-tenant boundaries, shared responsibility models between the cloud service provider (CSP) and the enterprise, and overarching trust domains. Concepts such as Zero Trust architecture are established here, defining that no entity—inside or outside the cloud perimeter—is trusted implicitly.
Layer 3: Logical Architecture (The Designer's View)
The logical layer specifies the abstract system design, defining security domains, identity management structures, and data classification schemas without tying them to specific vendors. In a cloud context, this includes designing abstract identity federations, role-based access control (RBAC) and attribute-based access control (ABAC) models, and logical network segmentation that can span multiple cloud providers and on-premises data centers.
Layer 4: Physical Architecture (The Implementer's View)
Here, abstract logical designs are mapped onto physical or virtual infrastructure blueprints. This layer specifies concrete technologies, such as choosing between specific key management services (KMS), hardware security modules (HSMs), software-defined networking (SDN) appliances, and cloud-native monitoring tools. The physical architecture translates abstract trust zones into concrete virtual private clouds (VPCs), subnets, and security groups.
Layer 5: Component Architecture (The Builder's View)
The component layer deals with individual products, configurations, and code snippets. This includes the specific JSON or YAML templates used in Infrastructure as Code (IaC) tools like Terraform or AWS CloudFormation, specific encryption algorithms (e.g., AES-256 for data at rest, TLS 1.3 for data in transit), and API security gateways. Every component is tied back to the higher layers to verify its business justification.
Layer 6: Operational Architecture (The Administrator's View)
The final layer addresses the ongoing operations, maintenance, monitoring, and governance of the cloud security architecture. This encompasses security information and event management (SIEM) integration, cloud workload protection platforms (CWPP), continuous compliance monitoring, incident response playbooks, and regular vulnerability management routines.
Addressing Cloud Security Challenges Through the Sherwood-SABSA Methodology
Cloud computing introduces unique architectural challenges that traditional data center security models cannot adequately resolve. Utilizing the Sherwood Business Security Architecture framework helps mitigate these challenges through structured governance.
The Shared Responsibility Model and Governance
One of the most persistent challenges in cloud security is navigating the shared responsibility model. While cloud providers secure the underlying infrastructure, enterprises remain responsible for data security, identity and access management, operating system updates, and application security. SABSA provides a mechanism to map these responsibilities clearly, ensuring that no operational gap exists between internal IT teams, third-party managed service providers, and the cloud vendor.
Multi-Cloud and Hybrid Complexity
As enterprises adopt multi-cloud strategies—leveraging AWS, Microsoft Azure, Google Cloud Platform, and SaaS applications simultaneously—managing disparate security controls becomes exponentially difficult. A SABSA-based cloud security architecture establishes a unified policy framework. By defining security policies at the conceptual and logical layers first, organizations can enforce consistent access controls, logging standards, and data protection rules across heterogeneous cloud environments.
Identity as the New Perimeter
In cloud environments, traditional network boundaries dissolve. Users access applications from unmanaged devices, and workloads communicate across internet boundaries. SABSA emphasizes the "Who" and "What" dimensions across all abstraction layers, facilitating a seamless transition to Identity-Centric Security. By tying identity governance directly to business roles and risk profiles, organizations can implement adaptive multi-factor authentication (MFA) and granular authorization mechanisms.
Comparing Traditional Security Frameworks with SABSA in Cloud Migrations
To understand the unique value proposition of Sherwood Business Security Architecture in cloud deployments, it is helpful to compare it with standard compliance-driven frameworks.
| Feature / Dimension | Compliance-Driven Frameworks (e.g., NIST, ISO 27001) | SABSA / Sherwood Business Security Architecture |
|---|---|---|
| Primary Driver | Regulatory compliance and audit readiness. | Business strategy, risk optimization, and value creation. |
| Perspective | Bottom-up or control-based; focuses on implementing specific technical safeguards. | Top-down; begins with business objectives and traces down to technical controls. |
| Customization | Often treated as a static checklist applied uniformly across assets. | Highly tailored to enterprise risk appetite, culture, and operational context. |
| Cloud Adaptability | Requires mapping new cloud services to existing static control sets. | Naturally accommodates dynamic cloud environments through abstraction layers. |
| Traceability | Limited visibility into why a specific technical control exists relative to business value. | Complete traceability from business goals to operational configurations. |
Implementing a SABSA-Aligned Cloud Security Strategy: Step-by-Step
Deploying a Sherwood Business Security Architecture within a cloud-first or hybrid enterprise requires a disciplined, phased approach.
Step 1: Establish Business Alignment and Sponsorship
Secure executive sponsorship by framing security architecture as a business enabler. Define the financial, operational, and strategic goals of the cloud initiative. Establish Key Risk Indicators (KRIs) and Key Performance Indicators (KPIs) that measure security effectiveness against business velocity and cost efficiency.
Step 2: Execute the Contextual and Conceptual Analysis
Map the enterprise's data assets, business processes, and regulatory mandates. Determine the appropriate cloud deployment models (public, private, hybrid, or multi-cloud) based on data sensitivity, residency requirements, and latency needs. Design high-level trust boundaries and authorization models.
Step 3: Develop Logical and Physical Blueprints
Translate conceptual requirements into logical security domains. Define enterprise-wide identity and access management (IAM) strategies, encryption standards, and network segmentation rules. Select appropriate cloud services, security tooling, and automation pipelines that align with the physical and component layers.
Step 4: Implement Infrastructure as Code and Automation
Embed security policies directly into Infrastructure as Code (IaC) templates. By utilizing automated policy-as-code tools (such as OPA/Rego or AWS Config rules), organizations can enforce SABSA-derived constraints automatically during deployment, preventing misconfigurations before workloads go live.
Step 5: Establish Continuous Monitoring and Governance
Deploy cloud-native logging, monitoring, and threat detection mechanisms. Continuously audit cloud configurations against the established architecture to detect drift, unauthorized changes, or emerging vulnerabilities, feeding operational insights back into the architectural lifecycle.
Common Pitfalls and Troubleshooting in Cloud Security Architecture
Even with a robust methodology like SABSA, organizations often encounter common pitfalls during implementation.
Pitfall 1: Over-Engineering the Abstraction Layers
Organizations sometimes treat SABSA as a purely academic exercise, producing massive documentation sets that fail to connect with daily engineering operations.
- Solution: Keep the architectural iterations lean. Ensure every layer directly informs the layer below it, culminating in actionable Infrastructure as Code templates and automated guardrails.
Pitfall 2: Treating Cloud Security as a One-Time Project
Cloud environments evolve rapidly, with providers releasing hundreds of new features annually. A static security architecture quickly becomes obsolete.
- Solution: Establish a continuous architecture review board that updates conceptual and logical models in tandem with cloud provider roadmap updates and shifting business requirements.
Pitfall 3: Ignoring Developer Friction
If security architecture introduces excessive bureaucracy or slows down deployment pipelines, development teams will bypass security controls, leading to shadow IT and severe vulnerabilities.
- Solution: Integrate security guardrails directly into CI/CD pipelines as automated checks, ensuring developers receive immediate, constructive feedback without manual bottlenecks.
Frequently Asked Questions
What is the primary difference between NIST/ISO frameworks and SABSA for cloud security?
NIST and ISO 27001 provide prescriptive catalogs of security controls and best practices, focusing heavily on what controls must be in place. SABSA is a methodology for designing custom security architectures from the top down, starting with business objectives and risk management before selecting appropriate controls.
How does Sherwood Business Security Architecture support multi-cloud strategies?
SABSA provides an abstract, business-driven policy framework (Layers 1-3) that remains consistent regardless of the underlying cloud vendor. Organizations can map these unified business policies to the specific physical and component mechanisms (Layers 4-6) of AWS, Azure, Google Cloud, or on-premises infrastructure.
Is SABSA suitable for agile and DevOps-driven cloud environments?
Yes, when implemented correctly. While SABSA appears structured and hierarchical, its top-down traceability allows organizations to codify architectural policies into automated CI/CD pipelines, ensuring speed and agility do not compromise security governance.
Who should be involved in developing a SABSA-aligned cloud security architecture?
Successful implementation requires cross-functional collaboration involving executive leadership (defining business goals), enterprise and security architects (mapping the SABSA layers), cloud engineers and developers (building components), and compliance officers (validating regulatory alignment).
How does SABSA address the cloud shared responsibility model?
SABSA explicitly maps responsibilities across all six abstraction layers and six operational perspectives. This ensures that every task—whether managed by the cloud service provider or the internal enterprise—is accounted for, leaving no ambiguity in risk ownership.
Conclusion and Next Actions
Implementing Sherwood Business Security Architecture and SABSA in cloud environments bridges the persistent gap between executive business strategy and technical cloud engineering. By shifting the focus from rigid compliance checklists to value-driven risk management, organizations can build secure, resilient, and scalable cloud infrastructures. To begin, audit your current cloud estate against the six SABSA layers, identify gaps in business alignment, and transition security policies into automated, code-driven guardrails.
Image Gallery
Select an image to open it in a new tab.

Simon Caldwell
Enterprise Technology and Systems Editor
