Understanding Avanan Cloud Security Services: A Comprehensive Guide to API-Based Email Protection
Avanan, now a core component of Check Point Harmony Email & Collaboration, provides a cloud-native security platform that protects enterprise email and SaaS applications from sophisticated threats. By utilizing an API-based architecture, it secures environments like Microsoft 365 and Google Workspace from within, blocking phishing, malware, and account takeover attempts before they reach the user's inbox.
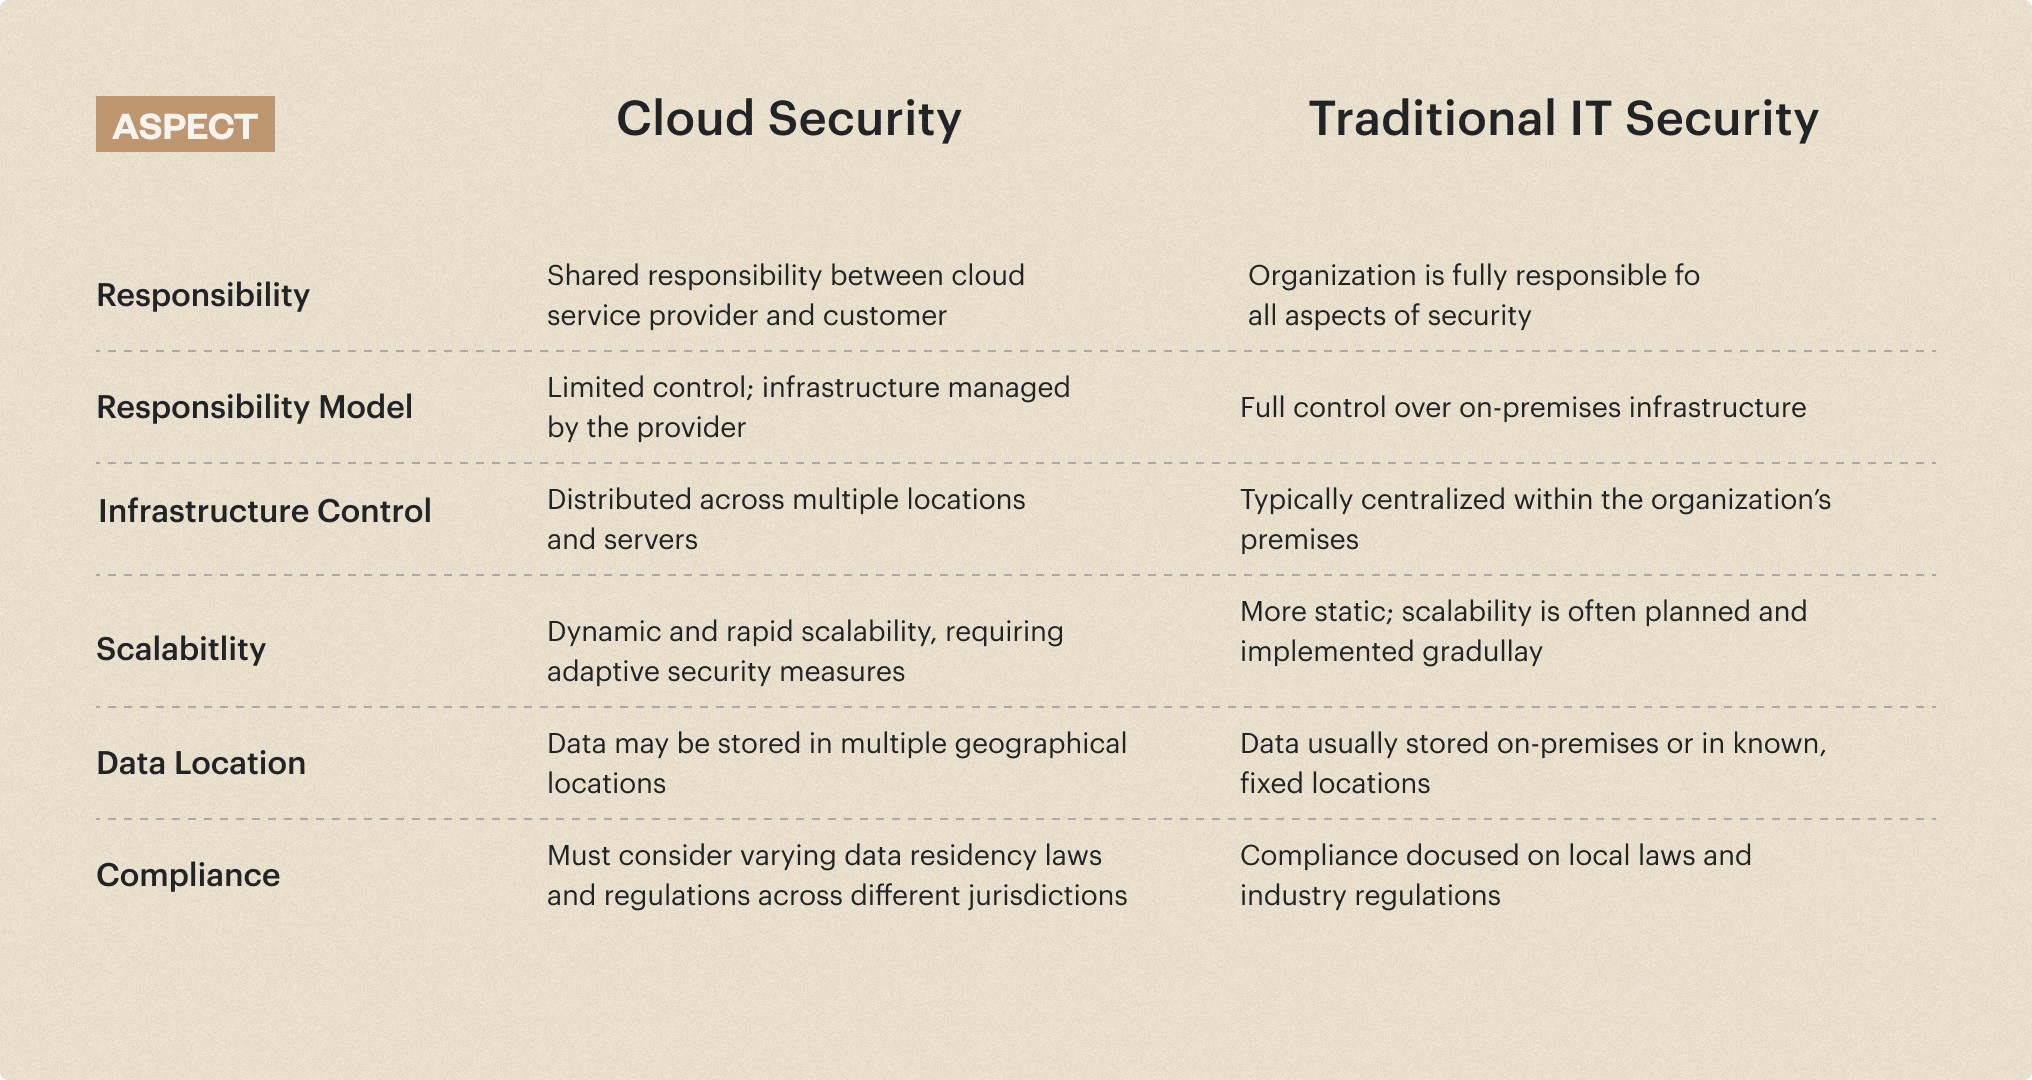
The evolution of cloud security has moved beyond the traditional perimeter. As organizations migrated to Microsoft 365 and Google Workspace, the limitations of legacy Secure Email Gateways (SEGs) became apparent. These legacy systems, which rely on redirecting Mail Exchange (MX) records, often struggle with internal-to-internal email threats and are easily bypassed by attackers who "fingerprint" the gateway to find vulnerabilities.
Understanding Avanan cloud security services requires a shift in perspective from external "gatekeeping" to internal "integrity monitoring." By 2026, the integration of Avanan’s patented technology into the broader Check Point ecosystem has solidified its position as a leader in Integrated Cloud Email Security (ICES). This guide explores the architecture, core features, deployment strategies, and comparative advantages of Avanan in the modern cybersecurity landscape.
The Architectural Differentiator: Inline API Security
The fundamental difference between Avanan and traditional security solutions lies in its deployment method. While traditional SEGs sit in front of the email provider, Avanan connects via API. However, unlike many API-based tools that only scan mail after it has been delivered (post-delivery remediation), Avanan operates inline.
How Inline API Works
When an email is sent to an organization using Avanan, it first passes through the native security layers of the provider (e.g., Microsoft Defender for Office 365). Before the email is visible to the user, Avanan intercepts the message via API. It analyzes the content, attachments, and metadata in a fraction of a second. If the message is deemed malicious, Avanan cleanses or quarantines it.
This "Catch-All" approach ensures that Avanan sees exactly what the cloud provider sees, but with an additional, more rigorous layer of AI-driven analysis. Because it sits inside the cloud environment, it can also scan internal communications—emails sent from one employee to another—which traditional gateways typically ignore.
Visibility and Stealth
Attackers often use tools to determine which security gateway a company uses. If they see a Mimecast or Proofpoint MX record, they can tailor their phishing kits to bypass those specific filters. Because Avanan does not require an MX record change, it is invisible to external attackers. This "stealth mode" prevents hackers from testing their exploits against the organization's specific defenses before launching a campaign.
Core Features of Avanan Cloud Security
Avanan is not a single-function tool; it is a multi-layered security suite designed to address the most common vectors of cloud-based attacks.
1. Advanced Anti-Phishing (SmartPhish)
The SmartPhish engine is the heart of Avanan’s defense. It utilizes machine learning trained on millions of emails to identify patterns that indicate a phishing attempt.
- Indicator Analysis: It examines over 300 indicators per email, including the sender's reputation, domain age, hidden links, and even the "sentiment" of the text (e.g., creating a false sense of urgency).
- Brand Spoofing Protection: Avanan is particularly effective at catching "look-alike" domains and impersonation attempts that target high-level executives (Business Email Compromise or BEC).
2. Malware and Ransomware Protection
Through its integration with Check Point’s SandBlast technology, Avanan provides industry-leading sandboxing and threat extraction.
- Sandboxing: Suspicious attachments are detonated in a secure virtual environment to observe their behavior before they are allowed into the user's hands.
- Threat Extraction: For organizations that cannot afford the delay of sandboxing, Avanan can "cleanse" documents. It strips out active content (like macros or embedded scripts) and delivers a safe PDF version of the file to the user instantly, while the original undergoes deeper analysis.
3. Account Takeover (ATO) Prevention
One of the greatest risks in 2026 remains the compromise of legitimate user credentials. Avanan monitors user behavior across the entire SaaS suite, not just email.
- Anomalous Behavior: If a user logs in from an unusual geographic location, uses a new device, or suddenly starts creating inbox rules to hide outgoing mail, Avanan flags this as a potential ATO.
- Cross-App Correlation: If an account is compromised in Microsoft Teams and then used to send a malicious link in Outlook, Avanan correlates these events to lock down the compromised account automatically.
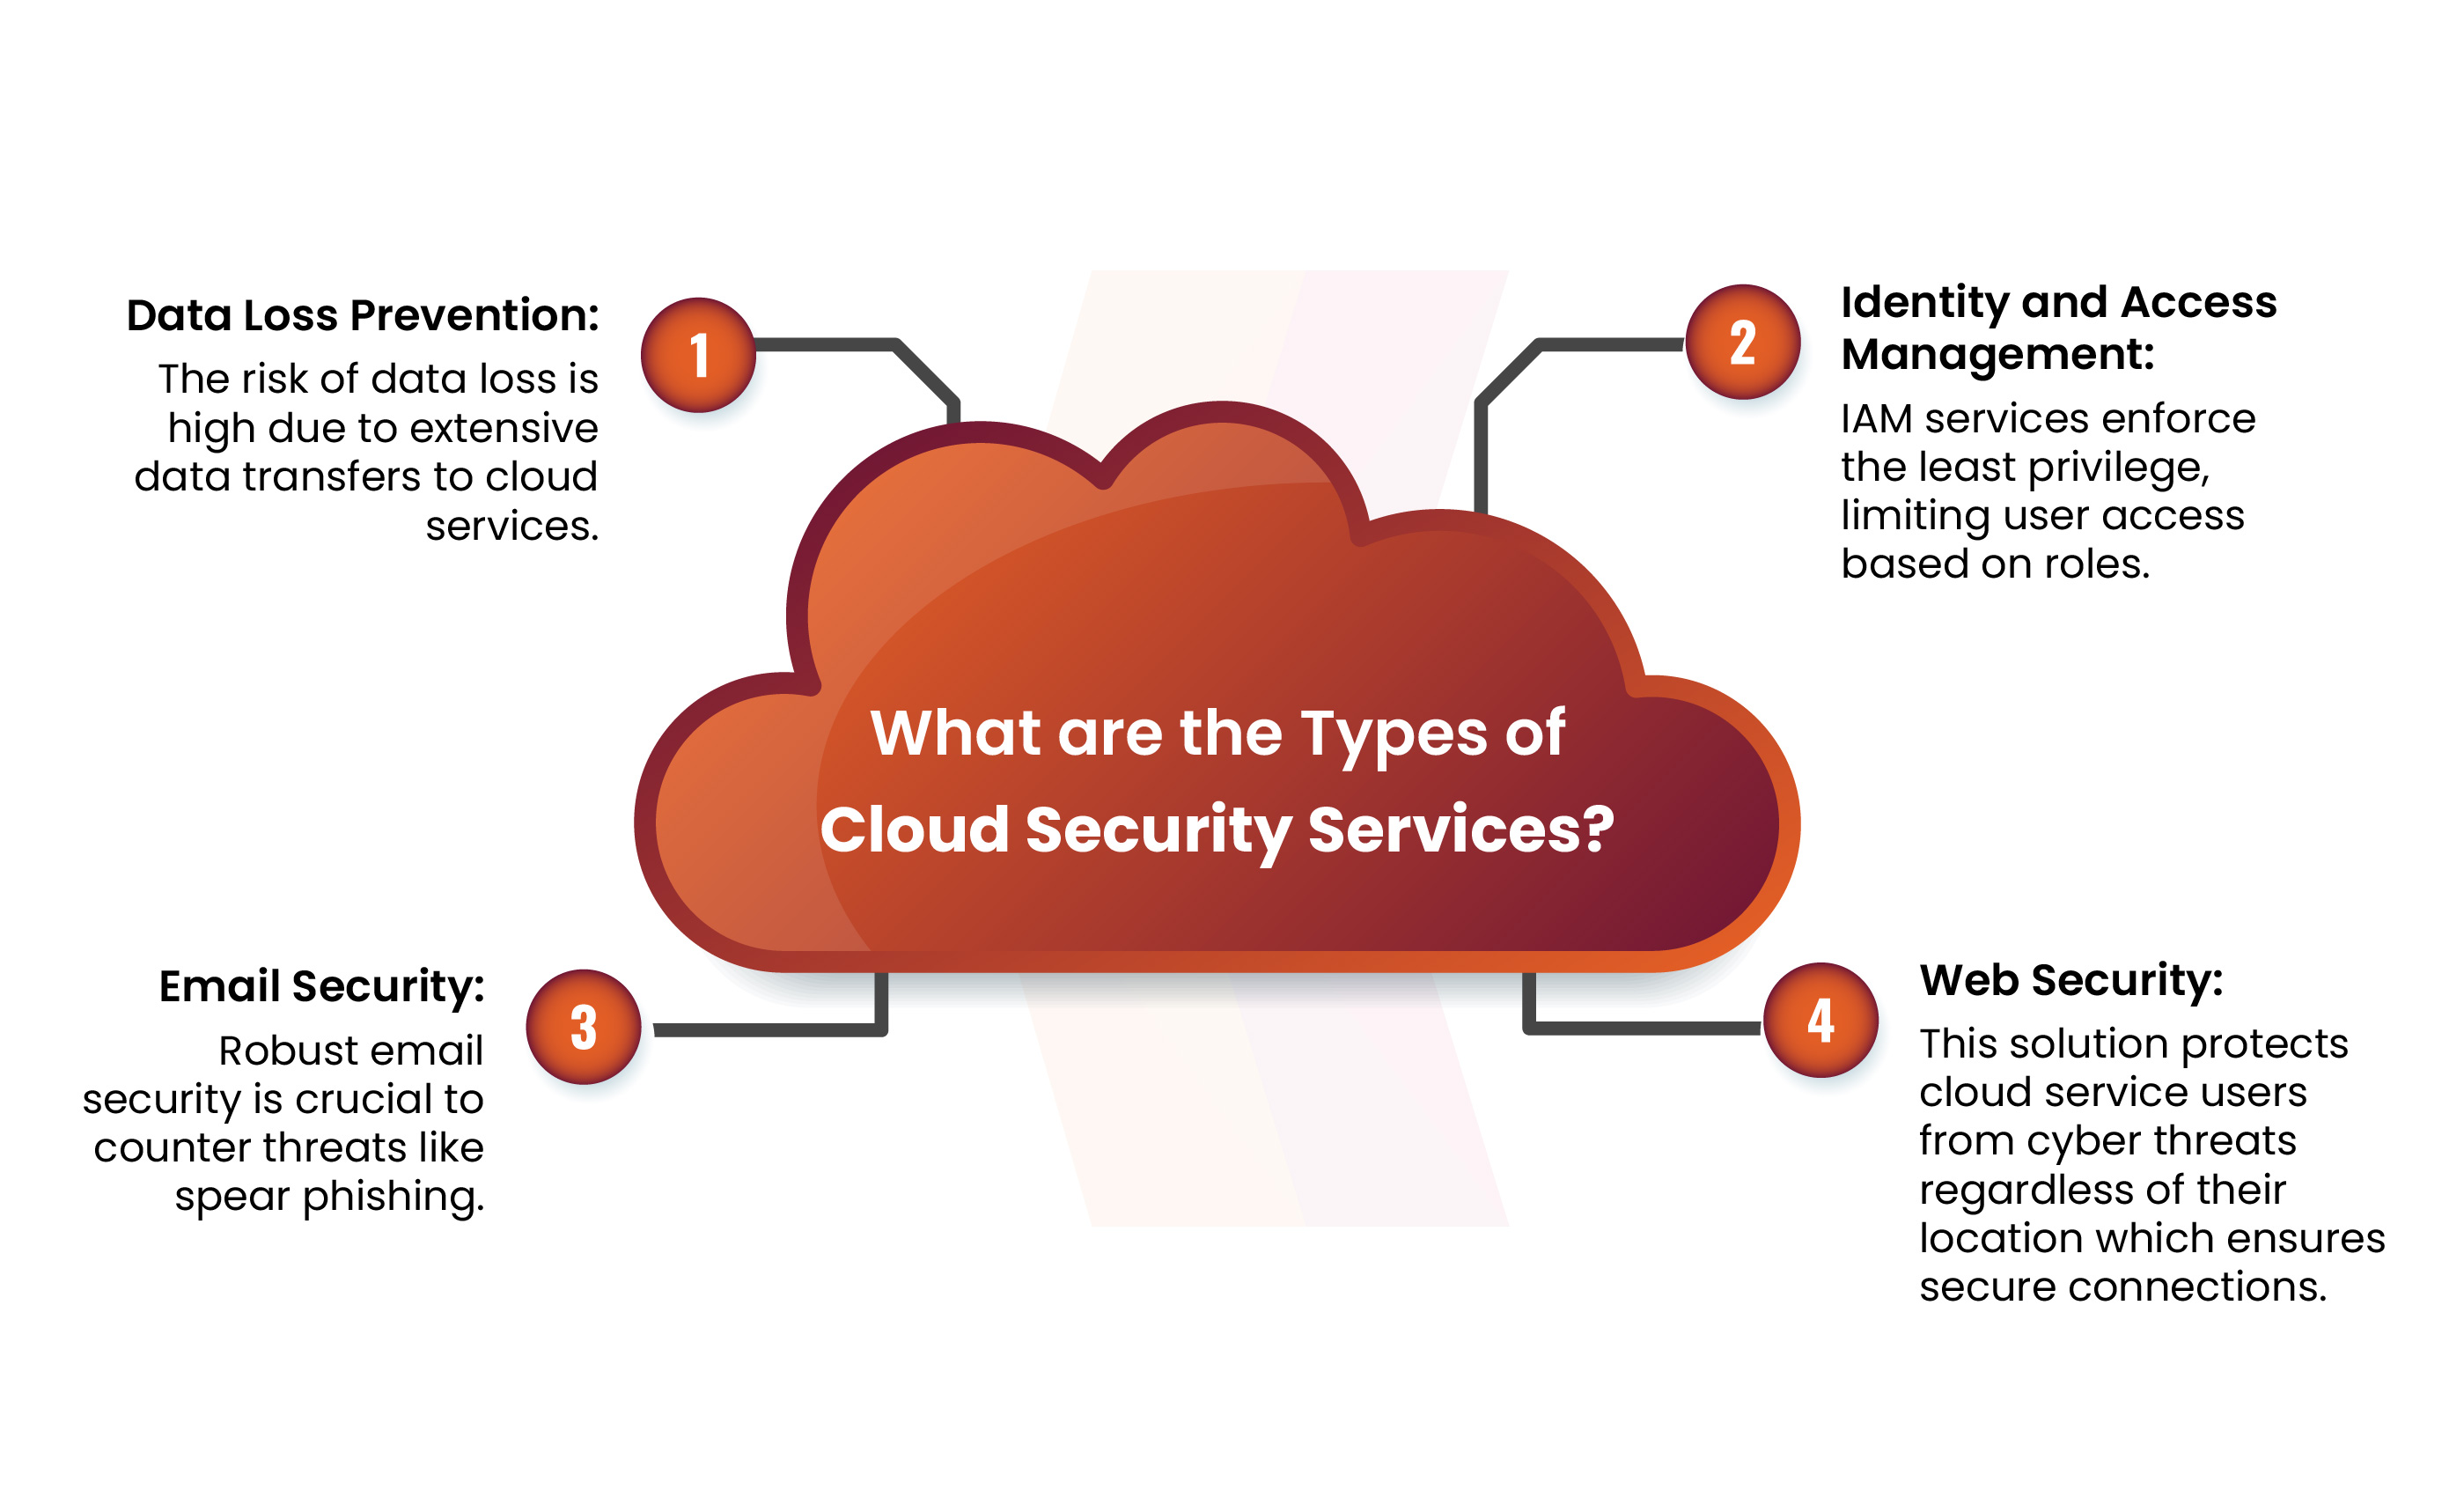
4. Data Loss Prevention (DLP) and Compliance
Avanan extends security to data integrity. It scans outgoing and internal messages for sensitive information such as Social Security numbers, credit card data, or proprietary source code.
- Custom Policies: Administrators can set granular policies that automatically encrypt, block, or notify management when sensitive data is shared inappropriately.
- SaaS Integration: This DLP functionality extends to file-sharing apps like OneDrive, Google Drive, and Box, ensuring that "public links" to sensitive documents are identified and revoked.
Comparing Avanan to Traditional Gateways and Native Security
Choosing a security posture requires understanding how Avanan fits into the existing stack. Many organizations ask why they need Avanan if they already pay for Microsoft Defender or Google Workspace's built-in security.
| Feature | Legacy SEG (MX-Based) | Native Cloud Security | Avanan (API-Based) |
|---|---|---|---|
| Deployment | Requires MX record change | Built-in | API Connection (5 mins) |
| Internal Email Scan | No | Yes | Yes |
| Stealth | No (Visible via MX) | Yes | Yes |
| Anti-Phishing | Signature/Reputation based | Basic/Moderate | Advanced AI (SmartPhish) |
| SaaS Protection | Email Only | Varies by license | Teams, Slack, OneDrive, etc. |
| User Experience | External Quarantines | Native Folders | Native Folders/Inline |
Why Native Security Isn't Always Enough
Microsoft and Google provide excellent foundational security, but their scale makes them a primary target. Hackers specifically design their malware to bypass the default filters of these giants. Avanan acts as a specialized second opinion. According to Gartner’s research on Market Guide for Email Security, organizations are increasingly adopting a "defense-in-depth" strategy that supplements native cloud security with specialized ICES providers like Avanan.
Protecting the Broader SaaS Ecosystem
While email remains the primary threat vector, collaboration tools have become the new frontier for social engineering. Avanan’s architecture allows it to protect more than just the inbox.
Microsoft Teams and Slack
In these environments, users often have a higher level of trust. A link sent through a Teams chat is more likely to be clicked than one sent via email. Avanan scans links and files shared in these channels in real-time. If a user uploads a malicious file to a public Slack channel, Avanan can delete it before other members download it.
File Storage (OneDrive, SharePoint, Google Drive)
"Shared file" phishing is a common tactic where an attacker shares a legitimate-looking document from a compromised account. Avanan scans the metadata and the contents of these shared files, applying the same DLP and malware policies that govern email. This prevents the cloud environment from being used as a distribution hub for malware.
Implementation and Operational Workflow
One of Avanan's most cited benefits is its ease of use. From a technical standpoint, the deployment process is significantly less disruptive than traditional solutions.
- Connection: An administrator grants Avanan permissions via OAuth to the Microsoft 365 or Google Workspace tenant. No downtime or mail flow interruption occurs.
- Learning Mode: For the first 24-72 hours, Avanan typically runs in "Monitor Only" mode. It analyzes historical data and current mail flow to build a baseline of "normal" behavior for the organization.
- Policy Configuration: Administrators select from pre-defined templates (e.g., "Strict Phishing Protection" or "Standard DLP") and apply them to specific groups or the entire organization.
- Inline Enforcement: Once switched to "Protect" mode, the API begins intercepting and neutralizing threats before they reach users.
Managed Service Options
By 2026, many organizations opt for managed versions of Avanan, where Check Point’s SOC (Security Operations Center) analysts review flagged items. This reduces the burden on internal IT teams who may not have the expertise to distinguish between a sophisticated phishing attempt and a false positive.
Common Challenges and Troubleshooting
Despite its advanced AI, no security system is perfect. Users and administrators should be aware of potential operational nuances.
- False Positives: Highly aggressive AI settings can occasionally flag legitimate marketing emails or automated system notifications as phishing. Avanan provides an "Allow List" that can be updated globally or per-user.
- Latency: Because the API must scan the email before the user sees it, there is a theoretical delay. In practice, this is usually under one second, making it imperceptible to the end-user.
- Integration Conflicts: In rare cases, if another third-party tool is also trying to manage the mailbox via API, conflicts can occur. It is best practice to ensure Avanan is the primary security API.
Expert Recommendation: Who is Avanan For?
Avanan is particularly well-suited for mid-to-large enterprises that have fully embraced cloud collaboration. If your organization relies heavily on Microsoft 365 or Google Workspace and has seen an uptick in BEC or internal phishing, the API-based approach is superior to a traditional gateway.
Furthermore, for organizations subject to strict regulatory requirements (HIPAA, GDPR, SOC2), Avanan’s integrated DLP and detailed audit logs provide the necessary compliance framework without requiring a separate, complex DLP solution.
FAQ: Frequently Asked Questions
Does Avanan replace Microsoft Defender for Office 365?
Avanan can either replace or complement Microsoft Defender. Most organizations choose to keep the basic Microsoft protection enabled as a first layer and use Avanan as the primary defense for advanced threats. This creates a multi-vendor security strategy that is harder for attackers to penetrate.
How does Avanan handle encrypted emails?
Avanan can integrate with various encryption standards. If an email is encrypted using Microsoft’s native encryption, Avanan (with the correct permissions) can decrypt the content to scan for threats before re-encrypting it for delivery. For external encrypted mail, it relies on metadata and sender reputation analysis.
Can Avanan protect personal Gmail or Outlook accounts?
No. Avanan is an enterprise-grade solution designed for managed tenants (Google Workspace and Microsoft 365 Business/Enterprise). It requires administrative access to the domain's cloud environment to function.
What happens if the Avanan service goes down?
Because Avanan uses an API-based "fail-open" architecture, if the service were to become unavailable, mail flow would continue through the native provider (Microsoft or Google) uninterrupted. While you would temporarily lose the advanced Avanan protection, you would not lose the ability to send or receive emails.
Does Avanan scan attachments inside password-protected ZIP files?
Yes, Avanan employs advanced heuristics to identify password-protected files. It can often find the password within the body of the email itself or use a dictionary of common passwords to "unlock" and scan the contents of the file.
How does Avanan impact the user experience?
For the average employee, Avanan is invisible. There are no separate login portals for quarantines and no "External Mail" banners unless the admin chooses to enable them. Users simply receive fewer malicious emails. If an email is quarantined, the user can receive a digest or notification directly in their inbox to request a release.
Final Actionable Steps
To begin understanding how Avanan fits into your specific environment, the first step is to conduct a Threat Gap Analysis. Most Avanan providers offer a "trial mode" where the software scans your environment for 14 days in monitor-only mode. This often reveals thousands of threats that current defenses—whether they are legacy gateways or native filters—have missed. Reviewing this report will provide a data-driven foundation for deciding whether to transition to an API-based cloud security model.
Image Gallery
Select an image to open it in a new tab.


Mateo Castillo
Decentralized Finance and E-Payments Strategist
