CompTIA Security+ SY0-701 Book PDF Overview: A Complete Guide to Study Resources

To prepare for the CompTIA Security+ SY0-701 exam, choosing a comprehensive study guide or PDF overview is essential for mastering the five updated domains. Leading resources include the Official CompTIA Content, the Sybex Study Guide by Mike Chapple, and the Exam Cram series. These books provide deep technical insights into cloud security, automation, and zero-trust architecture, ensuring candidates meet the 750-point passing threshold on the 90-question exam.
The CompTIA Security+ certification remains the industry standard for establishing a career in cybersecurity. As of 2026, the SY0-701 version is the mature, definitive standard for baseline security skills. For many candidates, the search for a "book PDF overview" is the first step in a rigorous journey toward professional validation. This guide provides a detailed analysis of the available literature, the technical shifts in the SY0-701 objectives, and how to utilize digital PDF resources to maximize study efficiency.
The Evolution of the SY0-701 Curriculum
The transition from the previous SY0-601 to the SY0-701 reflected a significant shift in the global threat landscape. While the 601 version focused heavily on the implementation of security controls, the SY0-701 (released in late 2023 and remaining the primary exam through 2026) places a greater emphasis on the "why" and "how" of security operations within modern, decentralized environments.
In 2026, the cybersecurity field has moved beyond simple perimeter defense. The SY0-701 exam objectives reflect this by integrating more content regarding cloud-native security, hybrid work environments, and the automation of security tasks. When evaluating a book or PDF overview, it is critical to ensure it covers these specific evolutions:
- Cloud Security Integration: Unlike older versions where cloud was a standalone topic, SY0-701 weaves cloud security through every domain.
- Zero Trust Architecture: The exam now treats Zero Trust as a fundamental design principle rather than an advanced concept.
- Automation and Orchestration: There is a deeper focus on how scripts and automated tools (like SOAR) assist in incident response.
- Supply Chain Risk: Increased scrutiny on third-party vendors and the security of the software development lifecycle (SDLC).
Top Recommended Books and PDF Study Guides
Selecting the right study material depends on your current experience level and preferred learning style. Most top-tier publishers offer their content in both physical and PDF/eBook formats to cater to mobile learners.
1. The Official CompTIA Security+ Study Guide (Exam SY0-701)
Published directly by CompTIA, this is the primary source of truth. It is designed to follow the exam objectives exactly, making it an indispensable resource for those who want to ensure no topic is missed.
- Strengths: Includes the exact terminology used in the exam and provides access to the CompTIA learning portal.
- Format: Available as a high-quality, searchable PDF or through an interactive eBook reader.
- Technical Depth: High. It covers the theoretical "why" behind security protocols alongside practical "how-to" scenarios.
2. CompTIA Security+ Study Guide: Exam SY0-701 (Sybex)
Written by Mike Chapple and David Seidl, this book is arguably the most popular third-party resource. Chapple is a well-known figure in the certification world, and his writing style is accessible for beginners.
- Strengths: Excellent practice questions and a focus on real-world application. The Sybex online test bank is included with the purchase.
- Format: PDF, EPUB, and hardcover.
- Technical Depth: Balanced. It simplifies complex encryption and network security concepts without sacrificing the detail required for the exam.
3. CompTIA Security+ SY0-701 Exam Cram
Marty Pacyga’s "Exam Cram" series is designed for learners who already have a baseline of knowledge and need a condensed, high-impact review.
- Strengths: Includes "Cram Sheets"—ideal PDF overviews for last-minute memorization of ports, protocols, and acronyms.
- Format: Often sold as a bundle including a physical book and a digital PDF.
- Technical Depth: Focused. It avoids "fluff" and focuses strictly on what is required to pass the test.

Technical Breakdown of the SY0-701 Domains
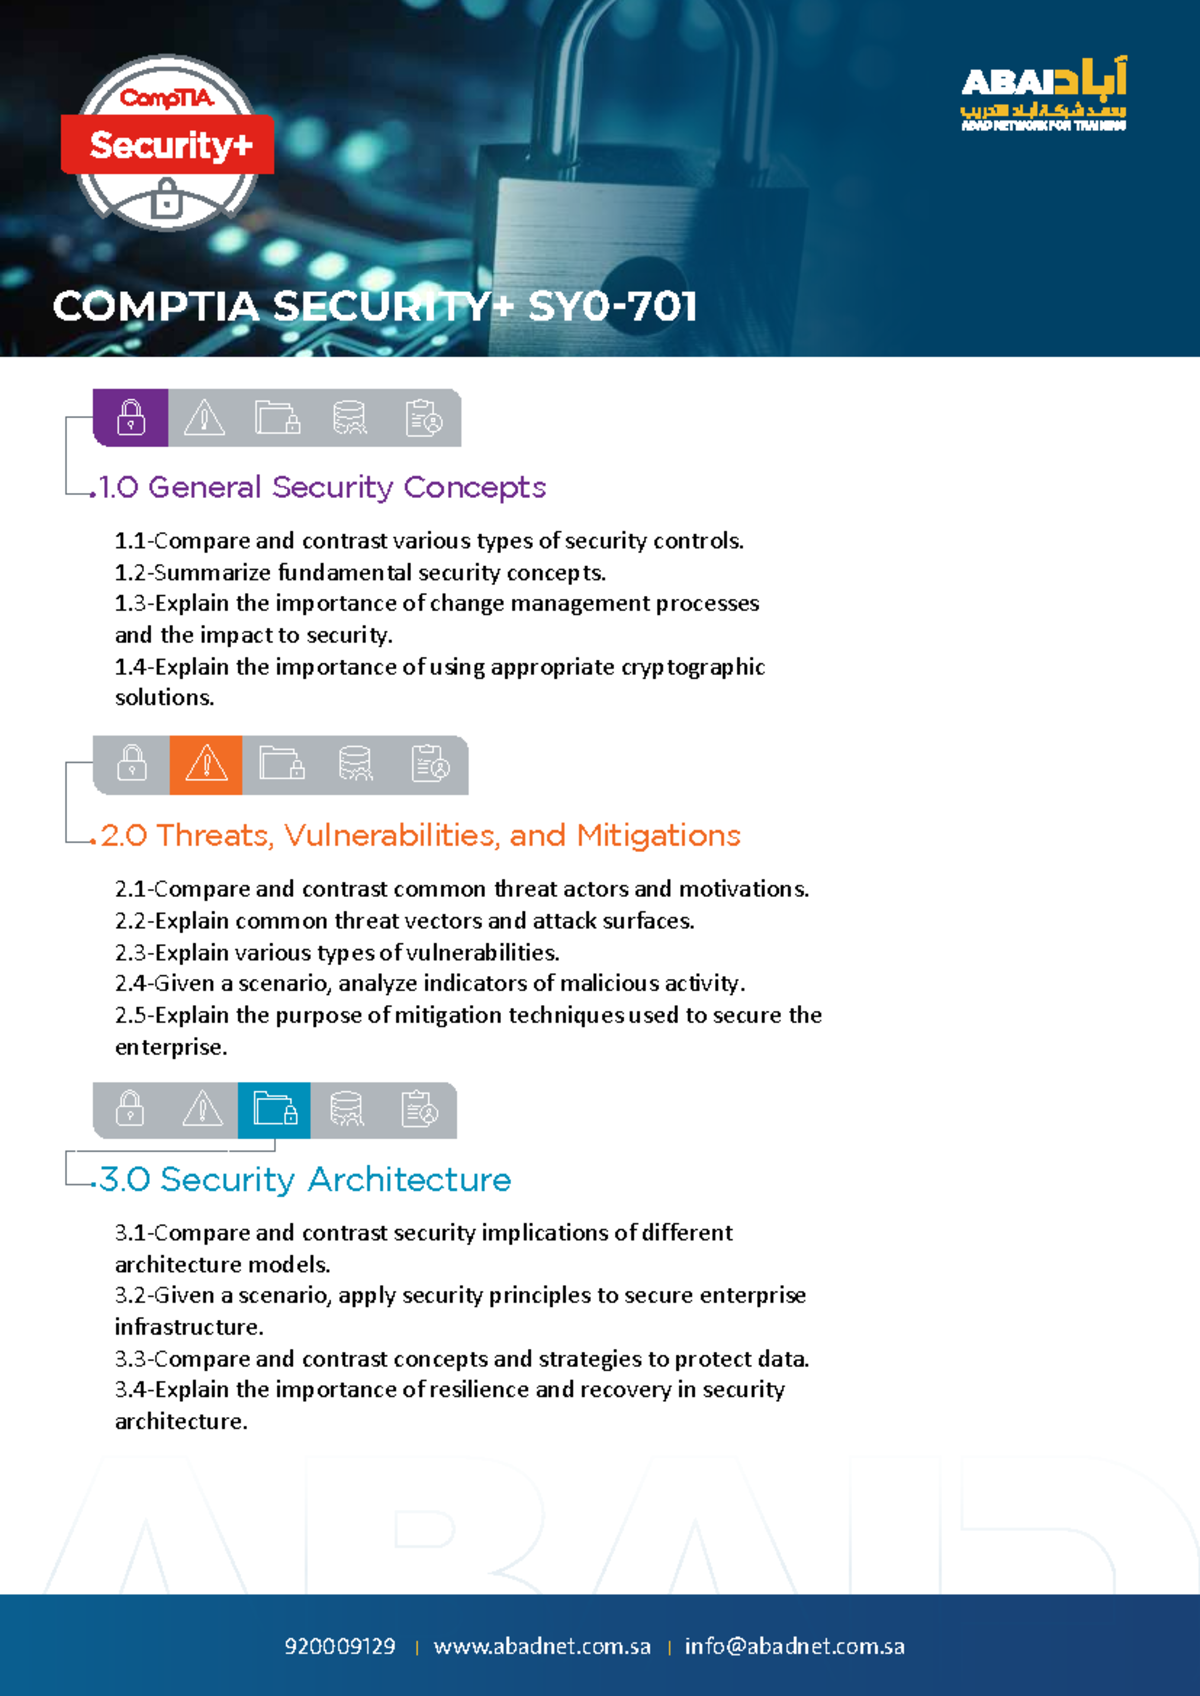
A high-quality book or PDF overview must be structured around the five domains defined by CompTIA. In 2026, these domains represent the core competencies expected of a security professional with two years of experience.
Domain 1.0: General Security Concepts (12%)
This domain covers the foundational principles that underpin all cybersecurity efforts. It includes the CIA Triad (Confidentiality, Integrity, and Availability), non-repudiation, and various security control types (managerial, operational, and technical). A good PDF overview will provide a clear table comparing these control types to help candidates distinguish them during the exam.
Domain 2.0: Threats, Vulnerabilities, and Mitigations (22%)
This is one of the largest sections of the exam. It requires candidates to identify types of malware, social engineering attacks, and application-level vulnerabilities (such as SQL injection or Cross-Site Scripting). The 701 version emphasizes threat actors and their motivations, ranging from script kiddies to state-sponsored Advanced Persistent Threats (APTs).
Domain 3.0: Security Architecture (18%)
Architecture focuses on the design of secure networks and systems. In 2026, this heavily involves Zero Trust principles, where "never trust, always verify" is the mantra. Books in this domain should explain the differences between Infrastructure as Code (IaC), serverless computing, and traditional data center security.
Domain 4.0: Security Operations (28%)
This is the most "hands-on" section of the exam. Candidates must understand how to use security tools for monitoring, incident response, and forensics. Key topics include:
- SIEM (Security Information and Event Management): Analyzing logs for anomalies.
- SOAR (Security Orchestration, Automation, and Response): Automating the response to common threats.
- Vulnerability Scanning: Using tools like Nessus or OpenVAS to identify weaknesses.
Domain 5.0: Security Program Management and Oversight (20%)
This domain deals with the "business" side of security. It covers risk management, governance, and compliance. Candidates must be familiar with frameworks like NIST CSF, ISO 27001, and regulations such as GDPR or HIPAA. Understanding the difference between qualitative and quantitative risk assessment is vital for this section.
Comparison of Leading SY0-701 Study Materials
| Resource Name | Best For | Included Features | Primary Focus |
|---|---|---|---|
| Official CompTIA Guide | Complete Beginners | Official Lab Access | Exam Objective Alignment |
| Sybex Study Guide | Self-Paced Learners | 1,000+ Practice Questions | Practical Application |
| Exam Cram | Quick Revision | Tear-out Cram Sheet | High-Frequency Topics |
| All-in-One (Conklin) | Technical Enthusiasts | Detailed Lab Exercises | Deep Technical Theory |
| Passport (Meyers) | On-the-go Study | Condensed Summaries | Exam Readiness Speed |
The Role of PDFs in Modern Certification Study
In 2026, the use of PDF-based study guides has largely surpassed physical textbooks for several practical reasons. A PDF overview allows for instant searchability, enabling a student to quickly find every instance of a term like "Diffie-Hellman" or "perfect forward secrecy."
Furthermore, PDF resources are easily integrated into tablet-based note-taking apps. This allows students to annotate diagrams, highlight critical exam tips, and insert their own research directly into the text. However, candidates should be wary of "brain dumps" or unauthorized PDF distributions. These often contain incorrect information and violate CompTIA’s candidate agreement, which can lead to a lifetime ban from holding CompTIA certifications.
Legitimate Sources for SY0-701 PDFs
To ensure the accuracy of the information, always acquire PDF overviews from authorized sources:
- CompTIA Store: The only source for the Official Study Guide.
- Pearson IT Certification: The publisher for the Exam Cram and several other high-quality guides.
- Amazon/VitalSource: Authorized retailers for digital versions of Sybex and McGraw Hill publications.
Strategic Approach to Using a Study Book
Simply reading a 600-page book from cover to cover is rarely the most effective way to pass the SY0-701. Instead, experts recommend a multi-phased approach using the book as a central hub for learning.
- The Initial Diagnostic: Most high-quality books include a "pre-assessment" quiz. Take this before reading to identify which of the five domains you already understand and where you have significant gaps.
- Objective-Based Reading: Instead of reading chronologically, read by domain. Use the official CompTIA SY0-701 Exam Objectives as a checklist. When you finish a chapter, cross off the corresponding sub-objective in the official PDF.
- Active Note-Taking: Convert the "Exam Tips" or "Notes" sections of your PDF overview into flashcards using tools like Anki or Quizlet. This leverages spaced repetition, which is scientifically proven to improve long-term retention of technical details.
- Lab Correlation: If the book mentions a tool like Nmap or Wireshark, don't just read about it. Open a virtual machine (such as Kali Linux) and run the commands described in the text. The SY0-701 includes Performance-Based Questions (PBQs) that require you to perform tasks, not just answer multiple-choice questions.
Common Mistakes When Choosing a Study Guide
Many candidates fail the Security+ exam not because they didn't study, but because they studied the wrong material or relied on outdated resources.
- Using SY0-601 Materials: Although there is overlap, roughly 20-25% of the content in SY0-701 is new or significantly revised. Using an old book will leave you unprepared for questions on current cloud security and governance standards.
- Relying Solely on "Cheat Sheets": A PDF overview or "cheat sheet" is a great supplement, but it cannot replace the depth of a full study guide. The exam tests your ability to apply concepts to scenarios, which requires a deeper understanding than simple memorization.
- Ignoring the Glossary: The SY0-701 introduces hundreds of acronyms. A significant portion of the exam difficulty comes from the language used. Ensure your chosen book has a comprehensive glossary and that you can identify every acronym in it.
Frequently Asked Questions
Is the SY0-701 harder than the SY0-601?
The SY0-701 is not necessarily "harder," but it is broader. It covers more modern technologies like AI in security and advanced cloud configurations. While the number of exam objectives was actually reduced in the 701 version, the depth required for each objective has increased to reflect 2026 industry standards.
Can I pass using only a PDF overview or summary?
For most candidates, a summary is not enough. The Security+ exam uses "Performance-Based Questions" (PBQs) that require you to configure firewalls or identify malicious code in a simulated environment. You generally need a full-length book or a video course to gain the context necessary to solve these problems.
Where can I find a free SY0-701 PDF overview?
CompTIA offers a free "Exam Objectives" PDF on their website. This is the most important free document you can own, as it lists every topic that could appear on the test. Many educators, such as Professor Messer, also provide free high-level study groups and summaries online.
How long does it take to study for the SY0-701 using a book?
The average candidate spends 60 to 90 days preparing for the exam. If you are studying for 1-2 hours a day, a standard 600-page study guide can be completed in about 6 weeks, leaving 2 weeks for practice exams and intensive review of your PDF notes.
Does the SY0-701 book cover the latest AI security threats?
Yes, most 2026 editions of the SY0-701 study guides have been updated to include the role of Artificial Intelligence in both offensive (AI-generated phishing) and defensive (AI-driven anomaly detection) cybersecurity operations.
Final Recommendation
For the most effective preparation, it is recommended to use a "two-pronged" approach. Purchase the Sybex CompTIA Security+ Study Guide for your deep-dive learning and keep a PDF overview or "Cheat Sheet" from a source like Exam Cram on your mobile device for quick review during downtime. Ensure that you supplement your reading with practice exams that mirror the actual testing environment. By focusing on the "Security Operations" and "Threats" domains, which carry the highest weight, you will be well-positioned to achieve your certification in 2026.
Image Gallery
Select an image to open it in a new tab.


Omar Farooq
EdTech Innovation and Virtual Pedagogy Journalist
