Comprehensive Software Kali Linux Overview: Tools, Features, and Capabilities in 2026
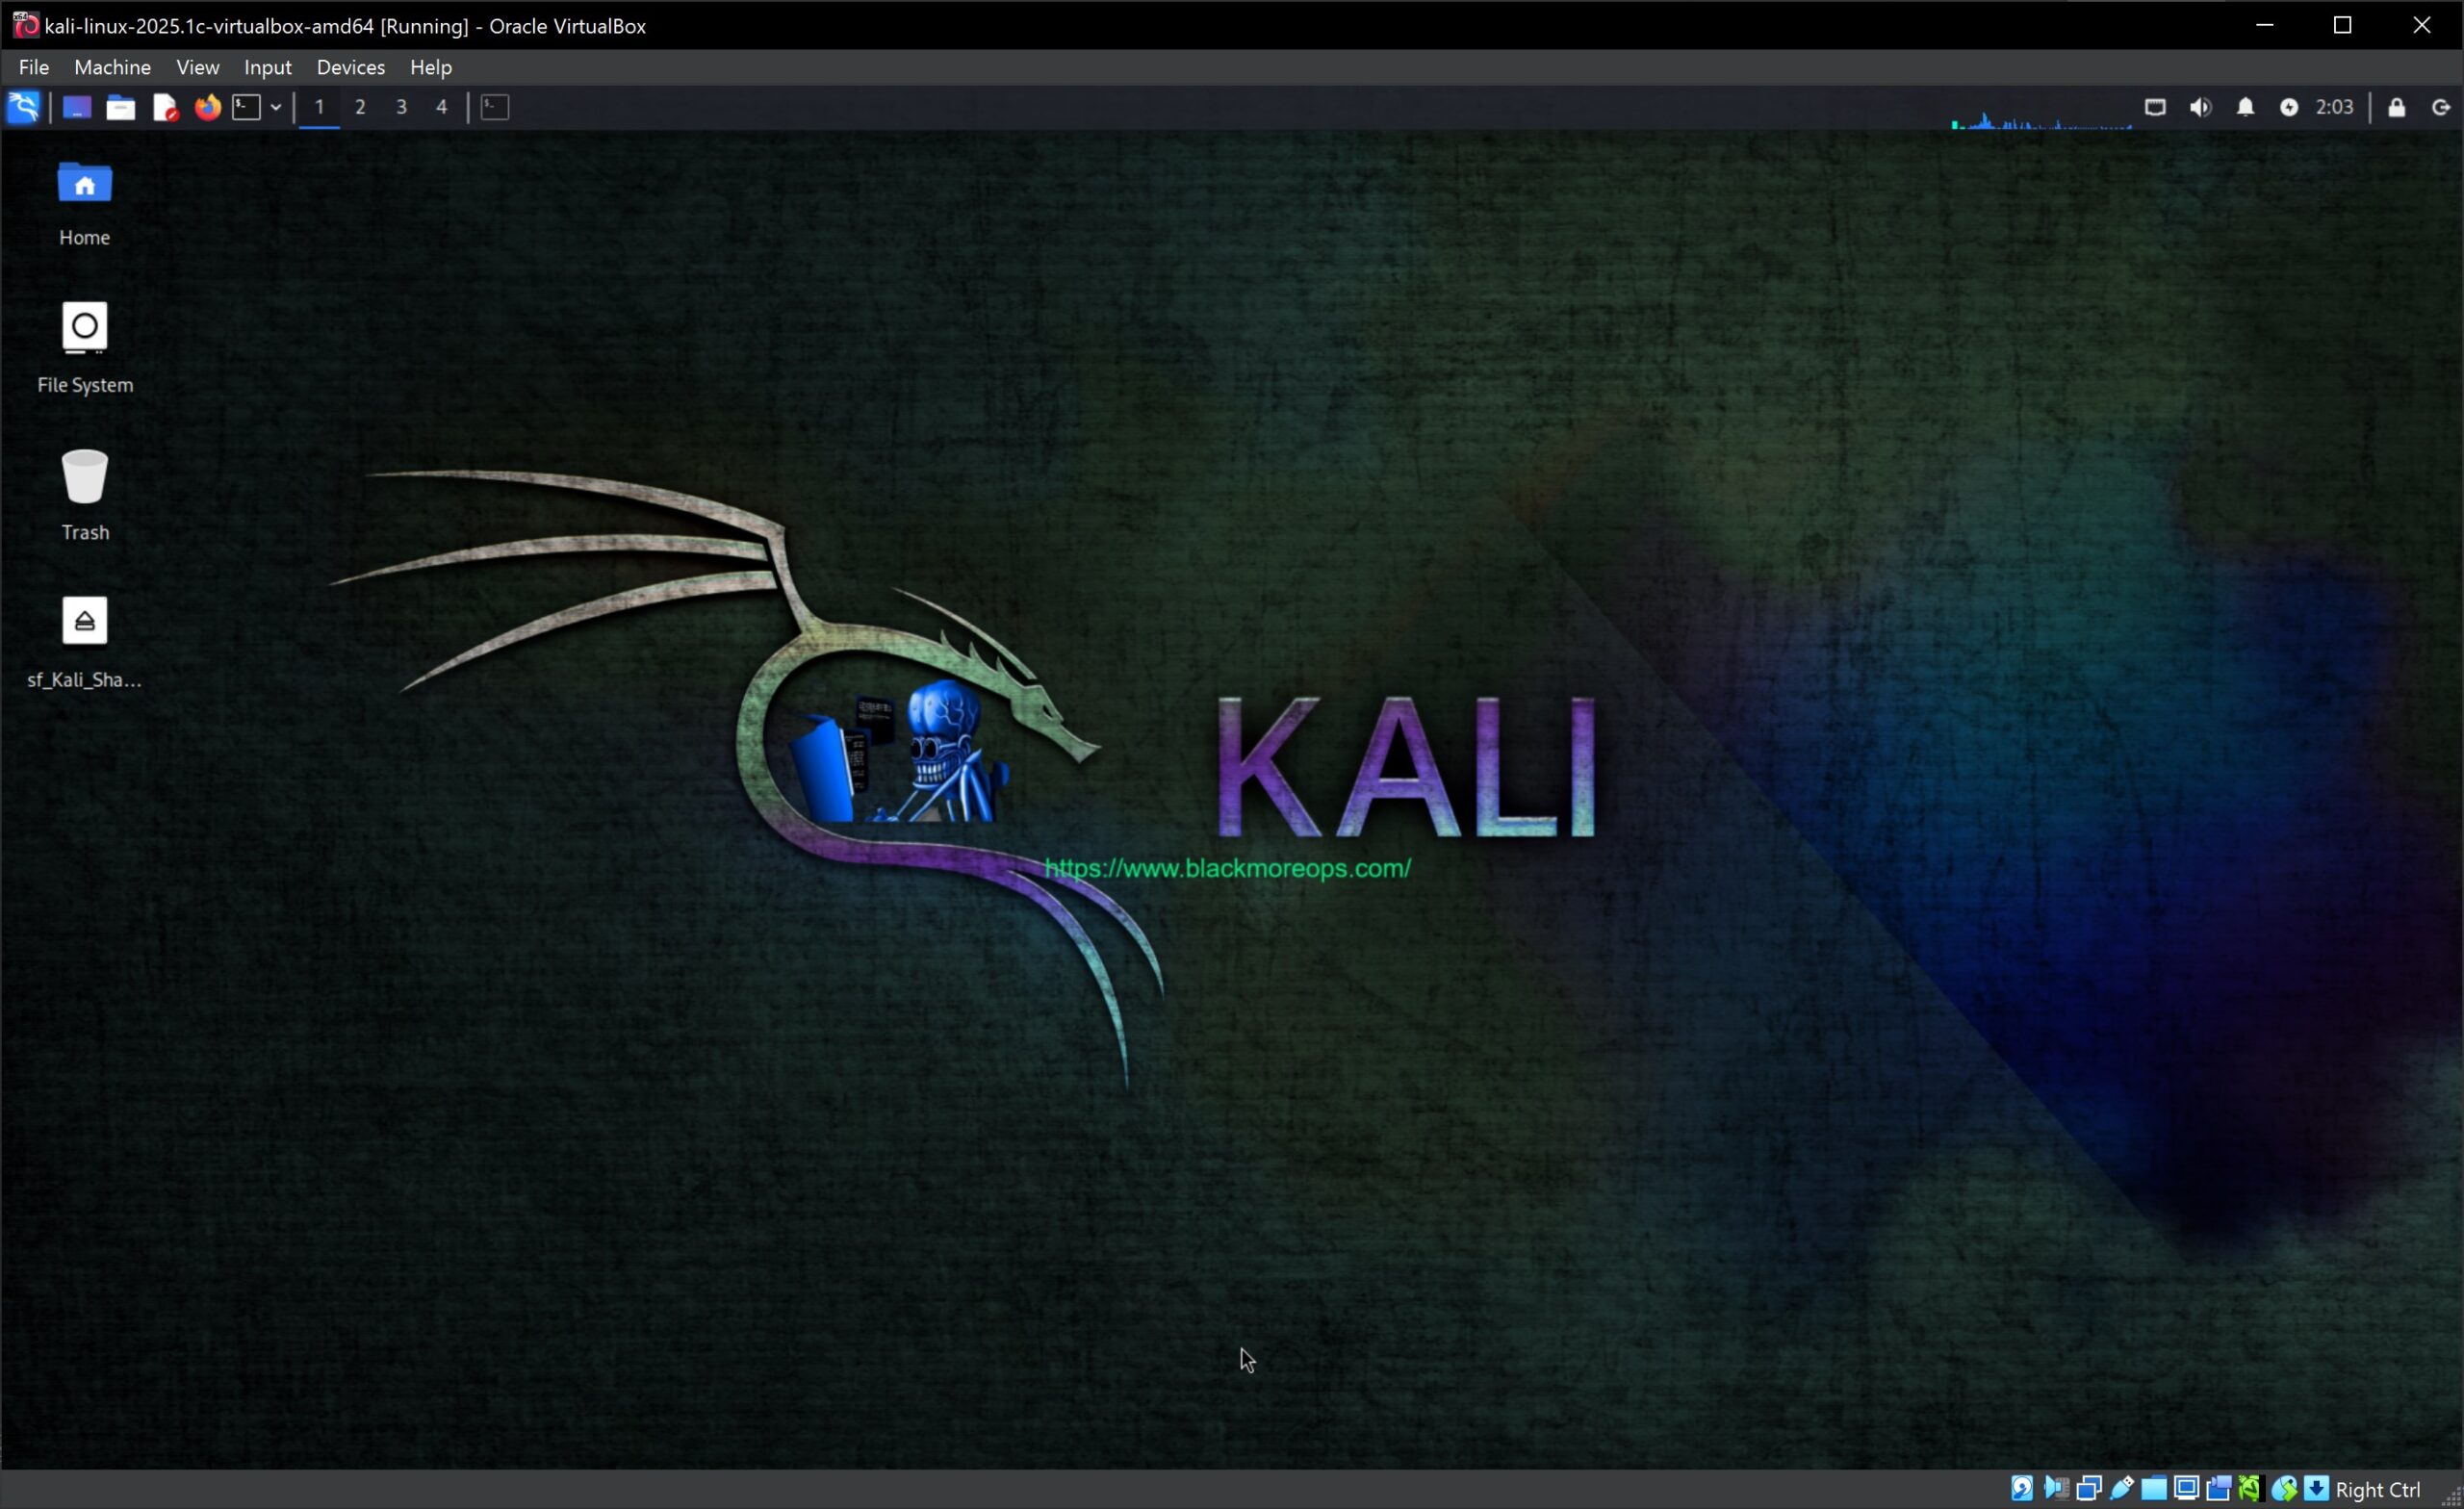
Kali Linux is a specialized Debian-derived distribution designed specifically for penetration testing, security auditing, and digital forensics. It integrates a curated ecosystem of over 600 professional-grade software tools, ranging from network scanners and password crackers to sophisticated exploitation frameworks, providing a standardized environment for cybersecurity professionals and researchers worldwide.
The Architecture of Kali Linux Software
To understand a software Kali Linux overview, one must first look at its foundation. Kali is not a general-purpose operating system; it is a highly tuned environment built on the Debian Testing branch. As of 2026, it continues to follow a rolling release model, ensuring that security practitioners have access to the latest versions of various tools without waiting for a major OS overhaul.
The core philosophy behind the Kali software suite is "efficiency through pre-configuration." While a user could theoretically install these tools on any Linux distribution, Kali simplifies the process by handling complex dependencies, kernel patches for wireless injection, and pre-configured environment variables. This allows security experts to focus on the task at hand—vulnerability assessment—rather than system administration.
The kernel itself is often modified to support specific hardware requirements that standard distributions ignore. This includes advanced drivers for wireless cards to support monitor mode and frame injection, which are critical for auditing Wi-Fi networks. The software architecture also prioritizes "Stealth Mode," a feature that prevents the system from generating any unsolicited outbound traffic, ensuring that the tester remains undetected during sensitive operations.
Categorizing the Kali Software Arsenal
The vast library of software within Kali Linux is organized into functional categories. This logical grouping helps users navigate the hundreds of available binaries based on the phase of a security assessment they are currently performing.
Information Gathering and Reconnaissance
The first phase of any security audit is reconnaissance. The software in this category is designed to map out the target's digital footprint. Tools like Nmap (Network Mapper) remain the gold standard for port scanning and service discovery. In 2026, Nmap continues to be used for identifying open ports, running services, and even the operating system of remote hosts. Other essential tools include theHarvester for OSINT (Open Source Intelligence) gathering and Maltego for visualizing complex relationships between people, companies, and network infrastructure.
Vulnerability Analysis
Once the target is mapped, the next step is identifying weaknesses. Software like Nikto provides comprehensive web server scanning, checking for outdated software and dangerous files. For more automated assessments, OpenVAS (Open Vulnerability Assessment System) offers a robust framework for scanning entire networks for known security flaws, comparing discovered services against massive databases of CVEs (Common Vulnerabilities and Exposures).
Web Application Analysis
As business logic moves to the browser, web application security has become a primary focus. Burp Suite is arguably the most critical piece of software in this category. While the Community Edition comes pre-installed, it serves as an intercepting proxy that allows testers to manipulate HTTP/S traffic between the browser and the server. Other tools like OWASP ZAP and sqlmap automate the detection of injection flaws and cross-site scripting (XSS) vulnerabilities.
Deep Dive into Essential Security Tools
A software Kali Linux overview would be incomplete without highlighting the "heavy hitters"—the tools that form the backbone of modern penetration testing.
The Metasploit Framework
Metasploit is more than just a tool; it is a modular exploitation platform. It contains thousands of exploits for various operating systems and applications. Its primary strength lies in its ability to deliver "payloads"—scripts that execute on a target system once a vulnerability is exploited. In the 2026 cybersecurity landscape, Metasploit remains the industry standard for verifying the "exploitability" of a discovered vulnerability, moving beyond mere theoretical risk.
Wireshark and Network Analysis
For deep packet inspection, Wireshark is unrivaled. It allows users to capture and interactively browse the traffic running on a computer network. It is used for troubleshooting network problems, but in a Kali context, it is used to analyze protocol behavior, intercept unencrypted credentials, and identify malicious traffic patterns.
Password Cracking and Cryptography
Kali includes powerful tools for testing the strength of authentication mechanisms. John the Ripper and Hashcat are the primary engines for password recovery. Hashcat, specifically, is designed to leverage GPU acceleration, making it incredibly fast at cracking modern hashing algorithms. These tools are used by professionals to demonstrate how easily weak passwords can be bypassed, emphasizing the need for robust MFA (Multi-Factor Authentication).
Software Categories and Primary Use Cases
The following table provides a quick reference for the major software groups found in a standard Kali Linux installation.
| Category | Primary Purpose | Key Example Tools |
|---|---|---|
| Information Gathering | Mapping networks and gathering OSINT. | Nmap, Maltego, Recon-ng |
| Vulnerability Research | Identifying known flaws in services. | OpenVAS, Legion, Nikto |
| Web Applications | Testing HTTP-based services and APIs. | Burp Suite, sqlmap, W3AF |
| Password Attacks | Testing credential strength/cracking. | Hashcat, John the Ripper, Hydra |
| Wireless Attacks | Auditing Wi-Fi and Bluetooth security. | Aircrack-ng, Kismet, Wifite |
| Exploitation Tools | Gaining access to remote systems. | Metasploit, Searchsploit, Social-Engineer Toolkit (SET) |
| Sniffing & Spoofing | Intercepting and manipulating traffic. | Wireshark, Bettercap, Ettercap |
| Post-Exploitation | Maintaining access and lateral movement. | Mimikatz, PowerShell Spy, Weevely |
| Forensics | Recovering data and analyzing evidence. | Autopsy, Sleuth Kit, Binwalk |
The Evolution of Kali: Specialized Software Editions
By 2026, Kali has evolved beyond a single ISO image. The software is now delivered in various flavors tailored to specific environments.
Kali Purple: The Defensive Pivot
While Kali was traditionally "Red Team" (offensive) software, Kali Purple represents a shift toward "Blue Team" (defensive) operations. It includes tools for incident response, malware analysis, and network monitoring. It is designed to be a "SOC-in-a-box," providing smaller organizations with a pre-configured suite of defensive software like Malcolm, Suricata, and TheHive.
Kali NetHunter: Mobile Security
For mobile penetration testing, the NetHunter project brings Kali software to Android devices. It includes a custom kernel and a suite of tools that allow for attacks such as "BadUSB" (keyboard injection) and Wi-Fi frame injection directly from a smartphone. This is particularly useful for physical security audits where carrying a laptop might be impractical.
Kali Everywhere: Cloud and Containers
The software ecosystem also extends to the cloud. Official Kali images are available on AWS, Azure, and Google Cloud Platform. Furthermore, the use of Kali in Docker containers has become a standard practice for developers who want to run specific security tools in an isolated environment without installing a full operating system.
Hardware Requirements and Installation Modes
Running the extensive Kali software suite requires appropriate hardware, although the base OS is surprisingly lightweight.
- Bare Metal Installation: For maximum performance, especially when using GPU-accelerated tools like Hashcat, installing Kali directly on hardware is recommended. In 2026, a minimum of 8GB of RAM and a quad-core processor are standard for a smooth experience.
- Virtual Machines (VMs): This is the most common way to run Kali. Using software like VMware or VirtualBox, users can run Kali inside their primary OS (Windows or macOS). This provides a "snapshot" feature, allowing users to revert the system to a clean state after an experiment.
- Live USB with Persistence: This allows users to boot Kali from a thumb drive. By adding "persistence," the software and any data generated during a session are saved to an encrypted partition on the USB drive, making it a portable security toolkit.
- WSL (Windows Subsystem for Linux): For Windows users, Kali can be installed as an app. While this doesn't support some low-level hardware interactions (like raw Wi-Fi injection), it is excellent for running web-based tools and script-heavy tasks.
Ethical and Legal Considerations
The power of the software in Kali Linux comes with significant responsibility. Most of the tools included in the distribution could be classified as "dual-use"—they can be used for both legitimate security testing and illegal activities.
Users must strictly adhere to local and international laws. Performing a penetration test without written authorization from the target owner is illegal in almost every jurisdiction. Organizations like Offensive Security and SANS Institute provide training and certifications (such as the OSCP) that teach the ethical use of these tools. The software should only be used in controlled environments, labs (like Hack The Box or TryHackMe), or on systems for which the user has explicit permission to test.
Frequently Asked Questions
Is Kali Linux software suitable for beginners?
While Kali is famous, it is not recommended for those who are new to Linux in general. The software suite assumes a high degree of familiarity with the Linux command line and networking protocols. Beginners should first learn Linux fundamentals using a distribution like Ubuntu or Debian before transitioning to the specialized tools in Kali.
Can I use Kali Linux as my daily operating system?
Technically, yes, but it is highly discouraged. Kali is configured for security, not user convenience or privacy. Many services are disabled by default to reduce the attack surface, and the software repositories are focused on security tools rather than productivity software like office suites or video editors.
How do I update the software in Kali Linux?
Since Kali follows a rolling release model, you should use the standard Debian package management tools. Running sudo apt update && sudo apt full-upgrade -y will update the entire system, including all specialized security tools, to their latest versions.
Why are some tools missing from the default installation?
The "Kali-Linux-Default" image includes the top 100 most used tools. To keep the ISO size manageable, hundreds of other tools are available in the repositories but not pre-installed. You can install the "Kali-Linux-Everything" meta-package if you have sufficient disk space and require the full library.
Does Kali Linux software work on M1/M2/M3 Mac chips?
Yes, Kali Linux provides official ARM64 images. When used with virtualization software like Parallels or UTM, the software suite runs efficiently on Apple Silicon, though some low-level hardware features may still have limitations compared to native x86 hardware.
Final Recommendations for Users
If you are looking to explore the software within Kali Linux, your first action should be to set up a Virtual Machine. This environment allows you to experiment safely without risking your primary operating system or personal data. Start by mastering Nmap for network discovery and Burp Suite for web analysis, as these provide the most immediate insight into how security auditing works. Always remember that the goal of using Kali is to identify and fix vulnerabilities, contributing to a more secure digital ecosystem.
Image Gallery
Select an image to open it in a new tab.




Lars Thomsen
Global Labor Markets and Economic Strategy Editor
