
Microsoft Cloud App Security Discovery—now a core component of Microsoft Defender for Cloud Apps—is a specialized process used to identify, monitor, and manage "Shadow IT" by analyzing traffic logs against a database of over 31,000 cloud applications. It provides visibility into which apps employees use, the risk levels associated with those services, and the volume of data being uploaded to unmanaged environments.
In the 2026 cybersecurity landscape, the perimeter has essentially dissolved. Organizations no longer operate within the safe confines of a physical office; instead, they rely on a sprawling web of Software-as-a-Service (SaaS), Platform-as-a-Service (PaaS), and Infrastructure-as-a-Service (IaaS) solutions. While these tools drive productivity, they also create a massive blind spot known as Shadow IT. Microsoft Cloud App Security (MCAS) Discovery is the primary mechanism within the Microsoft 365 ecosystem designed to eliminate this blind spot.
By leveraging network logs from firewalls and proxies, or by integrating directly with endpoint detection systems, Discovery allows security administrators to see exactly what is happening on their network. This guide explores the technical architecture, implementation strategies, and operational benefits of using Discovery to secure a modern enterprise.
The Evolution from MCAS to Microsoft Defender for Cloud Apps
While many practitioners still refer to the tool as Microsoft Cloud App Security (MCAS), Microsoft officially rebranded the service to Microsoft Defender for Cloud Apps several years ago to align it with the broader Defender XDR (Extended Detection and Response) suite. In 2026, this integration is tighter than ever.
Discovery is no longer a standalone feature but a foundational layer of the XDR stack. It works in tandem with Microsoft Defender for Endpoint, Microsoft Entra ID (formerly Azure AD), and Microsoft Purview to provide a holistic view of data travel. When we discuss "Discovery," we are specifically referring to the capability to ingest traffic data, parse it, and map it against the Cloud App Catalog to determine the security posture of an organization’s cloud usage.
How Cloud Discovery Works: The Technical Mechanics
Cloud Discovery operates by comparing your internal traffic logs against Microsoft’s vast Cloud App Catalog. This catalog is a curated list of cloud services, each ranked with a "Risk Score" based on more than 90 different factors, including regulatory compliance (GDPR, HIPAA, SOC2), security certificates, and legal terms of service.
The discovery process generally follows four distinct phases:
- Data Collection: Traffic logs are gathered from the network or endpoints.
- Log Parsing: The system identifies the source IP, destination URL, and the volume of data transferred.
- App Matching: The destination URLs are matched against the Cloud App Catalog.
- Risk Analysis: The identified apps are assigned a score from 1 (Risky) to 10 (Safe), allowing admins to prioritize their response.
Discovery Methods: Snapshot vs. Continuous
There are two primary ways to perform discovery, depending on the organization’s needs and infrastructure maturity.
Snapshot Reports
A Snapshot report is a manual upload of log files exported from a firewall or proxy. This is often the first step for organizations performing a "Cloud Security Assessment." It provides a point-in-time view of Shadow IT. While useful for initial audits, Snapshot reports become outdated the moment they are generated, as they do not capture real-time changes in user behavior.
Continuous Reports
Continuous reporting is the gold standard for modern security operations. It involves the automated streaming of logs to the Defender for Cloud Apps portal. This can be achieved through:
- Log Collectors: Small virtual machines (VMs) running Docker that sit on your network, receive Syslog or FTP streams from your firewalls, and securely transmit them to the Microsoft cloud.
- API-based Connectors: Direct integration with other cloud providers.
- Endpoint Integration: The most efficient method, which utilizes the Microsoft Defender for Endpoint sensor already installed on user devices.

The Role of Endpoint Discovery in 2026
In 2026, the reliance on traditional network-based log collectors has diminished in favor of Endpoint Discovery. Historically, if a user took their corporate laptop to a coffee shop and used a risky cloud storage provider, the corporate firewall would never see that traffic. Consequently, the Discovery process would miss that Shadow IT activity.
Endpoint Discovery solves this by using the Defender for Endpoint (MDE) sensor to monitor network activity directly on the device. Because the sensor lives on the OS, it captures traffic regardless of whether the user is on the corporate VPN, at home, or traveling. This data is then fed directly into the Defender for Cloud Apps portal.
This method offers several advantages:
- No Hardware/VM Overhead: There is no need to maintain log collector servers.
- Total Visibility: It captures "off-network" traffic that firewalls miss.
- Seamless Integration: If you are already using Microsoft 365 E5, the integration is often a single-toggle configuration in the Microsoft Defender portal.
Setting Up Microsoft Cloud App Security Discovery
Implementing Discovery requires a strategic approach to ensure data privacy and technical compatibility. As of 2026, the following prerequisites and steps are standard for a successful deployment.
Prerequisites and Licensing
To access the full suite of Discovery features, organizations typically require one of the following licenses:
- Microsoft 365 E5 / G5 / A5
- Microsoft 365 E5 Security
- Microsoft Defender for Cloud Apps (Standalone)
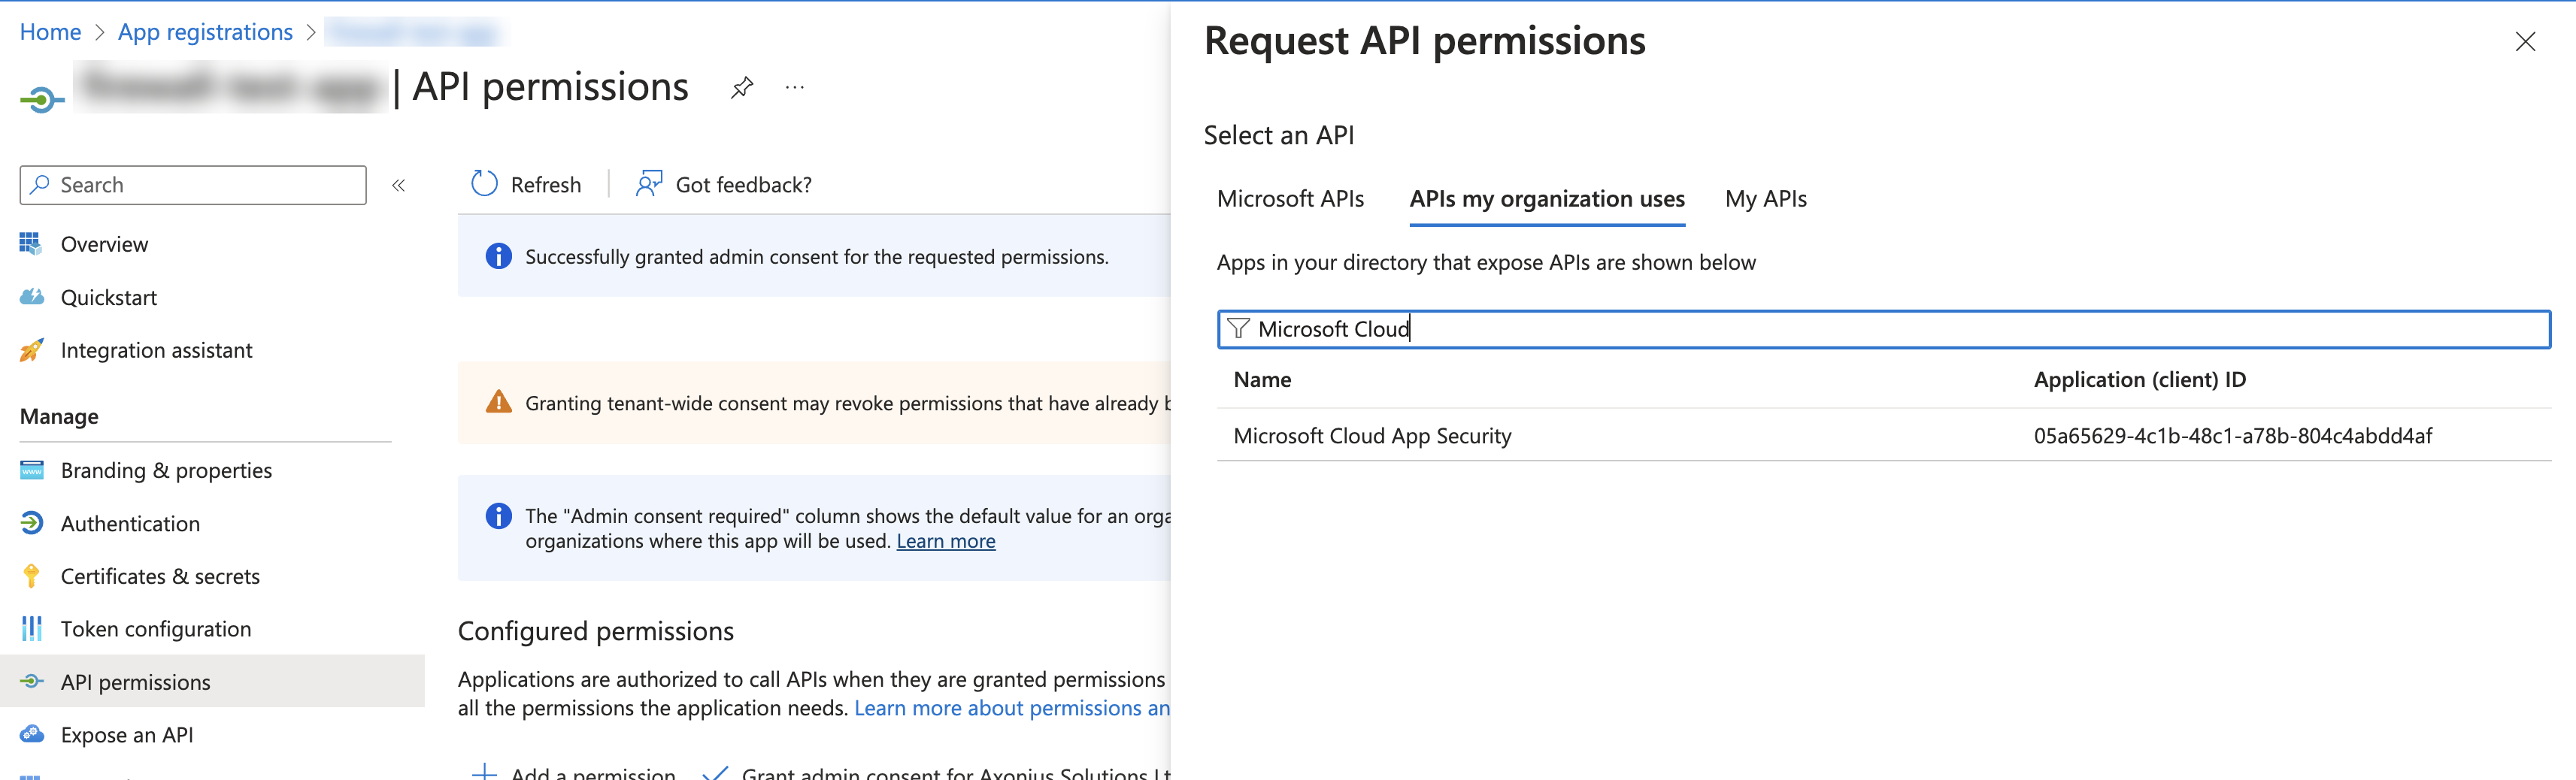
Users must also hold the Global Admin or Security Admin role within the Microsoft Entra tenant to configure data sources.
Step-by-Step Configuration (Log Collector Method)
- Define Your Data Sources: Identify which firewalls (Cisco, Palo Alto, Fortinet, etc.) or proxies (Zscaler, Blue Coat) will provide the logs.
- Set Up a Log Collector: Deploy a Linux-based VM (Ubuntu is commonly supported) and install the Docker engine.
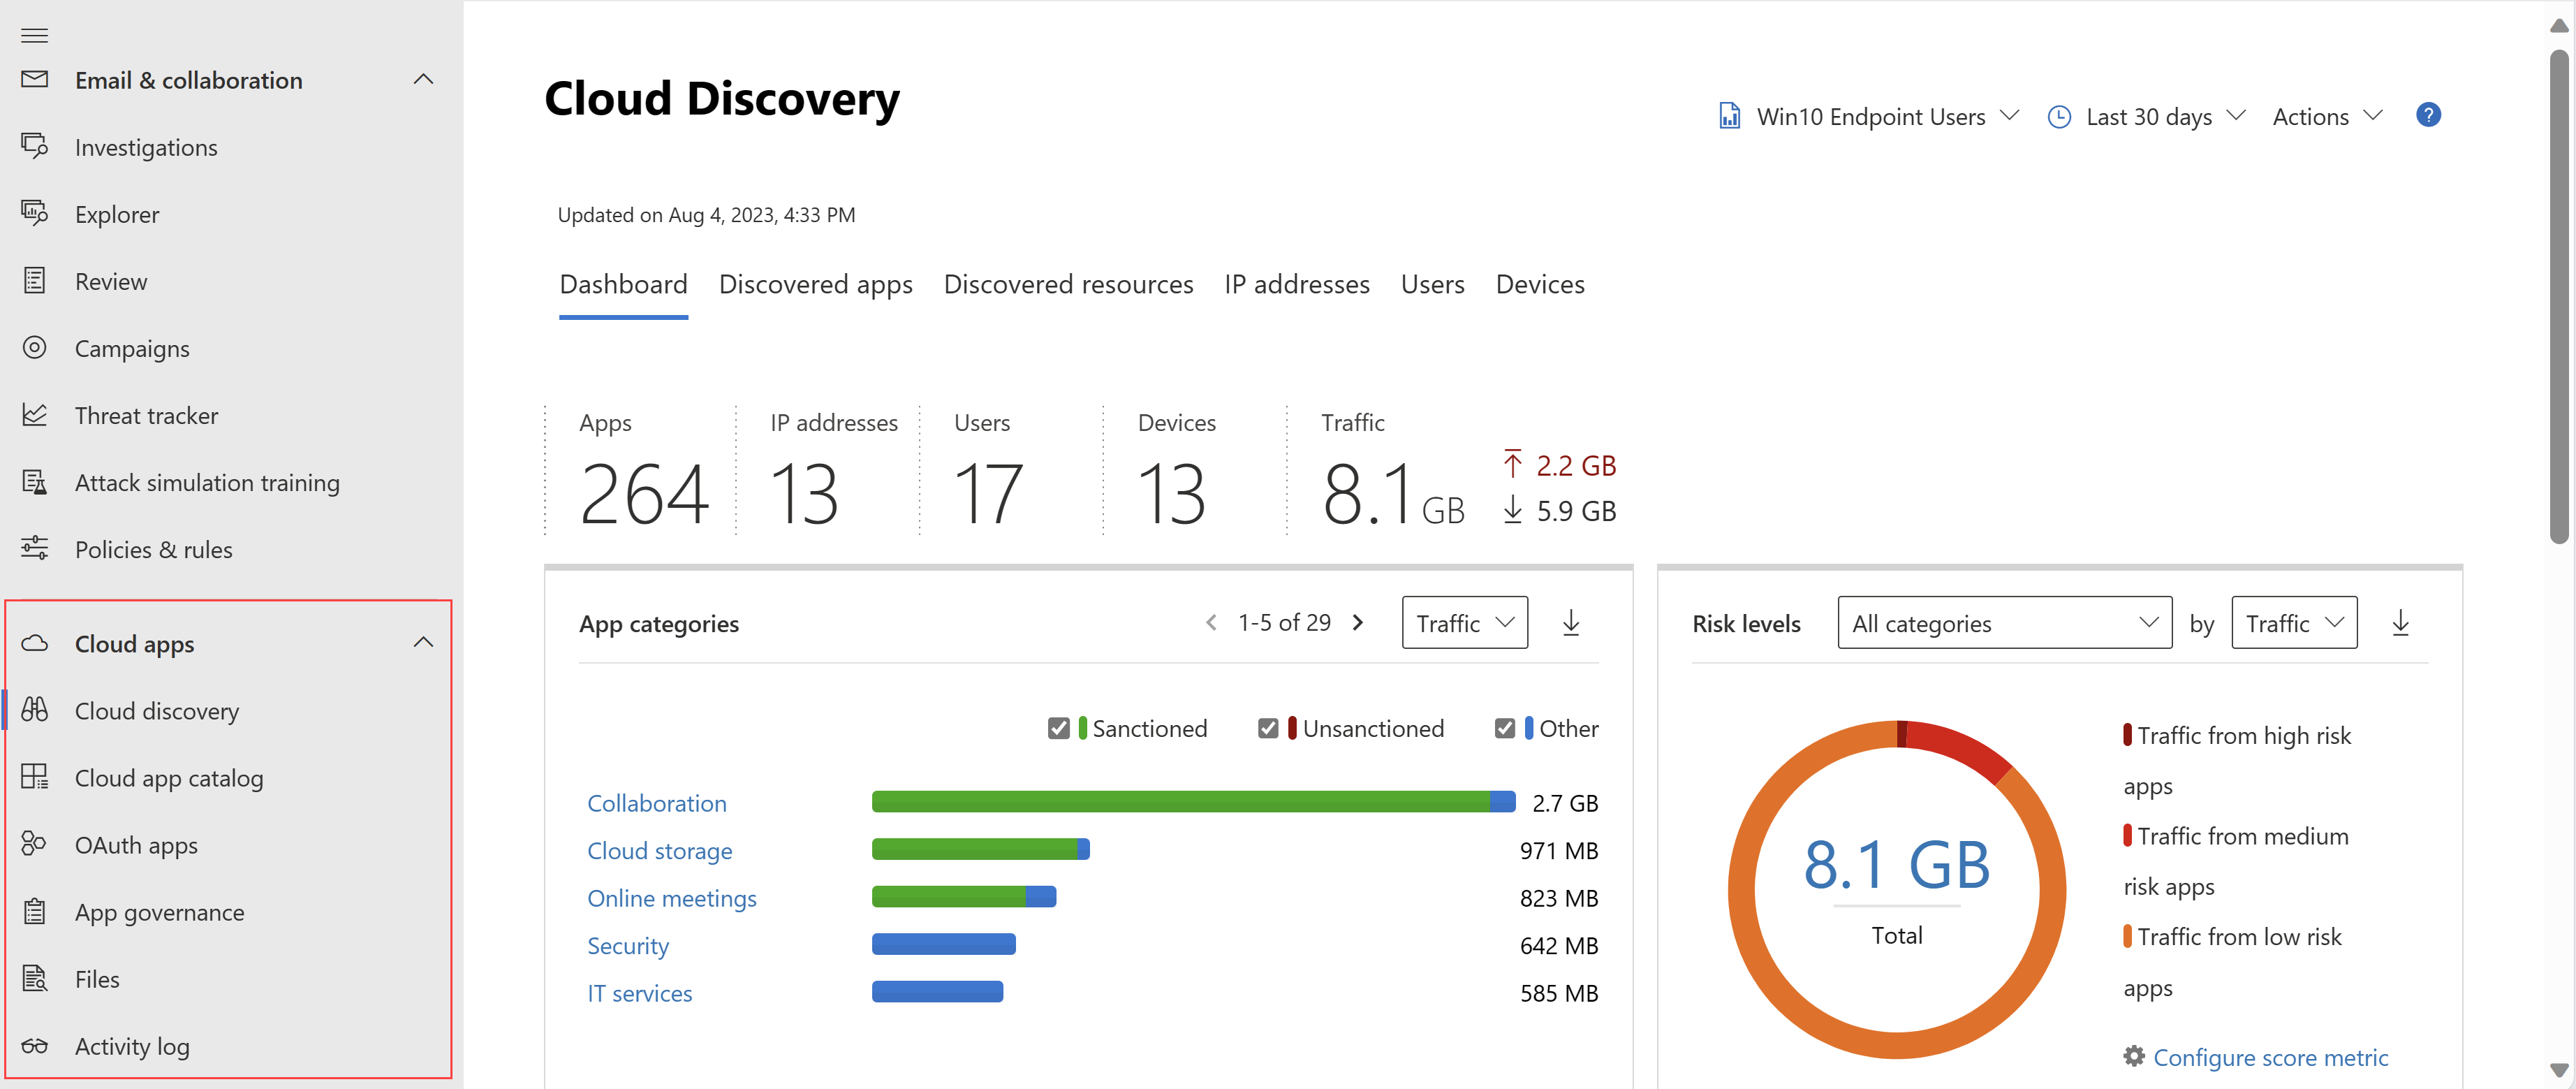
- Configure the Portal: In the Microsoft Defender portal, navigate to Cloud Apps -> Cloud Discovery -> Automatic Log Uploads. Generate a new API token for your collector.
- Network Configuration: Ensure your firewall is configured to send Syslog or FTP traffic to the IP address of the Log Collector VM on the designated port (usually 514 for Syslog).
- Verify Data Flow: Within 24 to 48 hours, the "Cloud Discovery Dashboard" should begin populating with discovered apps, user counts, and traffic volumes.
Analyzing the Cloud Discovery Dashboard
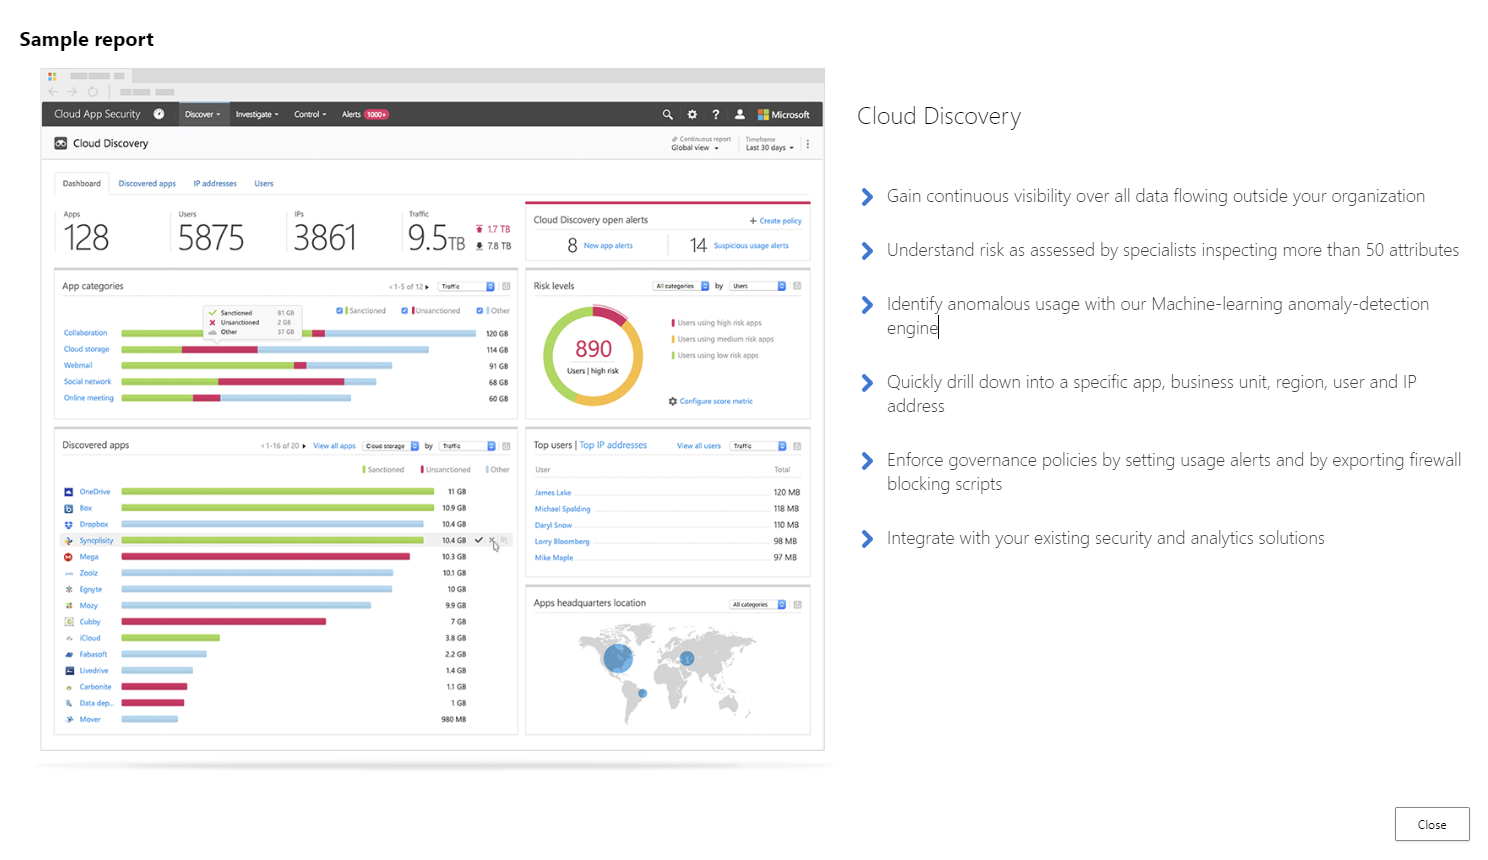
Once data begins flowing, the Cloud Discovery Dashboard becomes the central hub for Shadow IT governance. It provides several high-level views that are critical for risk management.
The Risk Score Explained
The 1-10 Risk Score is the heart of the discovery process. Microsoft’s researchers constantly update these scores based on:
- Security: Does the app support MFA? Is it vulnerable to known exploits?
- Compliance: Does the provider meet HIPAA, GDPR, or ISO 27001 standards?
- Legal: Who owns the data uploaded to the app? Is there a data retention policy?
An admin might decide that any app with a score below 4 is "Unsanctioned" and should be blocked at the firewall or endpoint level.
Identifying App Categories
Discovery categorizes apps into buckets such as "Cloud Storage," "Collaboration," "Generative AI," and "Social Media." In 2026, the Generative AI category is particularly scrutinized. Many organizations use Discovery to find employees who are pasting sensitive corporate data into unauthorized AI models that do not offer enterprise-grade privacy protections.
Comparing Discovery Methods
Choosing the right discovery method depends on your infrastructure and the location of your workforce.
| Feature | Snapshot Report | Log Collector | Endpoint Discovery (MDE) |
|---|---|---|---|
| Automation | Manual Upload | Fully Automated | Fully Automated |
| Data Recency | Point-in-time | Near Real-Time | Near Real-Time |
| Off-Network Visibility | No | No (requires VPN) | Yes (Full visibility) |
| Infrastructure Needed | None | VM with Docker | Defender for Endpoint Sensor |
| Complexity | Low | High | Very Low |
| Best For | Initial Audits | On-premises Networks | Remote/Hybrid Workforces |
Addressing Data Privacy and Scoping
A common concern with Cloud Discovery is user privacy. Because the system tracks URL requests, it can inadvertently collect data that is sensitive or governed by local privacy laws (like the GDPR in Europe).
Microsoft provides several tools to mitigate these concerns:
- Anonymization: You can choose to anonymize usernames in the reports. This allows you to see that "User X" is using a risky app without knowing their identity until a formal investigation is opened.
- Scoping: You can scope discovery to specific groups. For example, you might exclude the executive team from discovery or only monitor users in specific geographic regions.
- Data Retention: You can define how long the discovery data is stored in the portal (typically 90 days by default).
Common Implementation Mistakes to Avoid
Even with its robust automation, several pitfalls can hinder the effectiveness of Microsoft Cloud App Security Discovery.
1. Ignoring "Unsanctioned" App Alerts
Discovery is not just for viewing; it is for acting. A common mistake is identifying 500 "High Risk" apps but never moving them to the "Unsanctioned" list. Once an app is unsanctioned in the portal, Microsoft can automatically generate a block script for your firewall or trigger an automatic block via Defender for Endpoint.
2. Over-reliance on Firewall Logs
Firewalls often struggle with SSL/TLS inspection. If your firewall cannot decrypt the traffic, it might only see that a user is visiting *.google.com, rather than identifying the specific use of Google Drive vs. Google Search. For deep visibility, Endpoint Discovery or a proxy with full SSL inspection is required.
3. Failing to Update Log Formats
Firewall manufacturers occasionally update their log formats. If your Log Collector stops showing data after a firewall firmware update, the parser may need to be adjusted in the Defender portal to match the new log structure.
Frequently Asked Questions
Does Microsoft Cloud App Security Discovery work with third-party clouds like AWS?
Yes. While the name mentions "Microsoft," the tool is designed to discover usage across all cloud providers, including AWS, Google Cloud, and thousands of niche SaaS providers. It can also be integrated with AWS logs to monitor resource usage within those environments.
Can I block apps directly from the Discovery dashboard?
Yes. By marking an app as "Unsanctioned," you can automate the blocking process. If you have Defender for Endpoint integrated, the app will be blocked on the device level within minutes. For network-based blocking, you can export a block script compatible with your specific firewall vendor.
What is the difference between "Discovered Apps" and "Connected Apps"?
Discovered Apps are identified through traffic logs and are usually part of Shadow IT. Connected Apps are those you have officially authorized and linked via API (like connecting your Microsoft 365 or Salesforce instance to Defender for Cloud Apps) for deeper governance and file scanning.
Is discovery available for mobile devices?
Yes, provided those mobile devices are managed. If you use Microsoft Intune and have deployed the Defender for Endpoint app on iOS or Android, the network protection features can feed discovery data back to the portal, similar to a Windows or macOS device.
How often is the Cloud App Catalog updated?
Microsoft’s security research teams update the catalog daily. In 2026, AI-driven automation helps identify new cloud services as they launch, ensuring that even the newest startups are assigned a preliminary risk score within a short window of their emergence.
Strategic Recommendations for 2026
For organizations looking to master Microsoft Cloud App Security Discovery in 2026, the path forward is clear: prioritize Endpoint Discovery. The shift toward hybrid work and the rise of encrypted traffic make traditional firewall log collection less effective and more difficult to maintain.
Start by enabling the integration between Microsoft Defender for Endpoint and Defender for Cloud Apps. This "single-click" deployment provides the most comprehensive data set with the least amount of administrative effort. Once visibility is established, focus on the Generative AI and Cloud Storage categories, as these represent the highest risk for data exfiltration.
Finally, establish a recurring "Shadow IT Review Board." Use the Discovery data to identify popular but unmanaged apps that provide genuine value to employees. In many cases, the best response to Shadow IT is not to block it, but to bring it into the "Sanctioned" fold by purchasing enterprise licenses and applying proper security controls.
Image Gallery
Select an image to open it in a new tab.




Omar Farooq
EdTech Innovation and Virtual Pedagogy Journalist
