
Jailbreaking an iPhone involves removing software restrictions imposed by Apple, allowing users to install unauthorized applications and customize the operating system. To jailbreak in 2026, you must identify your device's chip architecture and iOS version, select a compatible tool like Dopamine or Palera1n, and follow specific sideloading or boot-level procedures.
Jailbreaking has evolved significantly from the early days of "one-click" browser exploits. In 2026, the landscape is defined by a modular approach, where the "rootless" architecture is the standard. This method modifies only the necessary variables to allow third-party code execution without altering the protected system partition. This guide provides a detailed technical overview of the prerequisites, methodologies, and risks associated with gaining elevated privileges on iOS.
Understanding the State of iOS Security in 2026
Apple’s security architecture has become increasingly sophisticated. Modern iPhones utilize a combination of hardware and software protections that make jailbreaking a complex endeavor. Two primary components define the difficulty: Pointer Authentication Codes (PAC) and the Page Protection Layer (PPL). These technologies are designed to prevent attackers—and jailbreakers—from executing arbitrary code even if they find a vulnerability in the kernel.
Because of these protections, modern jailbreaks (on A12 bionic chips and newer) are typically "semi-untethered." This means that while the jailbreak persists on the device, the kernel exploit must be re-run via an app every time the iPhone reboots. Furthermore, the industry has shifted toward rootless jailbreaks. Unlike traditional "rootful" methods, rootless jailbreaks do not touch the / (root) partition. Instead, they use a symlink-based system (often located in /var/jb) to store tweaks and binaries. This approach is safer, harder for banking apps to detect, and more compatible with Apple’s Signed System Volume (SSV) security.
Essential Prerequisites and Compatibility
Before attempting a jailbreak, you must verify your hardware and software specifications. The method you use depends entirely on the "Age of the Chip" and the specific build of iOS currently installed.
1. Identify Your Processor (SoC)
- A11 Bionic and Older (iPhone X and below): These devices are susceptible to the checkm8 exploit. This is a "bootrom" vulnerability, meaning it exists in the hardware and cannot be patched by software updates. If you have an iPhone 8 or iPhone X, you can likely jailbreak regardless of the iOS version, though some features like FaceID or Apple Pay may be disabled on newer firmware.
- A12 Bionic through A18/A19 (iPhone XR through iPhone 17): These devices require "userland" or "kernel" exploits. These are much rarer and are typically patched quickly by Apple. You must be on a specific, vulnerable version of iOS to proceed.
2. Verify Your iOS Version
Check your version under Settings > General > About. In the 2026 landscape, most active jailbreaks target versions of iOS 17 and specific early builds of iOS 18. If you have updated to the absolute latest version of iOS 19, a jailbreak may not yet be available for your specific device.
3. Basic Preparations
- Complete Backup: Always perform an encrypted backup via iCloud or a computer. Jailbreaking carries a non-zero risk of data loss.
- Disable Passcode/FaceID (For A11 Devices): On iPhone 8 and X, the checkm8 exploit conflicts with the Secure Enclave Processor (SEP). To jailbreak these specific devices on modern iOS versions, you often must factory reset the device and proceed without a passcode.
- Computer Access: Most modern methods require a macOS or Linux machine (or a specific Windows environment like Palen1x) to initial the exploit.

Comparison of Leading Jailbreak Tools
The following table outlines the primary tools utilized in 2026 for various device generations.
| Tool Name | Type | Target Hardware | iOS Compatibility | Primary Advantage |
|---|---|---|---|---|
| Dopamine | Semi-Untethered | A12 - A16+ (ARM64e) | iOS 15.0 - 18.x | Stable, rootless, high tweak compatibility. |
| Palera1n | Semi-Tethered | A8 - A11 (ARM64) | iOS 15.0 - 18.x+ | Impossible for Apple to patch via software. |
| Misaka / KFD | Package Manager | A12 - A18 | Various (Exploit-based) | Customization without a full kernel jailbreak. |
| Sideloadly | Utility | All | All | Essential for installing the jailbreak app. |
Step-by-Step Procedure: The Modern Kernel Jailbreak
This process describes the standard method for a semi-untethered jailbreak (like Dopamine) on an ARM64e device.
Step 1: Sideloading the Jailbreak Application
Because the jailbreak tool is not available on the App Store, you must "sideload" the .ipa file using a tool like AltStore or Sideloadly.
- Connect your iPhone to your computer.
- Open Sideloadly and enter your Apple ID (this is required to sign the app for a 7-day period).
- Drag the jailbreak
.ipa(e.g., Dopamine.ipa) into the tool. - Click "Start." The app will appear on your home screen.
Step 2: Trusting the Developer Profile
Apple will block the app from opening until you manually authorize it.
- Navigate to Settings > General > VPN & Device Management.
- Tap on your Apple ID under "Developer App."
- Select "Trust [Your Email]" and confirm.
Step 3: Running the Exploit
- Put your device into Airplane Mode and ensure Wi-Fi is off. This can sometimes improve exploit success rates by reducing background system activity.
- Open the jailbreak app (e.g., Dopamine).
- Tap the "Jailbreak" button.
- The app will cycle through various stages: "Finding Kernel Read/Write," "Bypassing PPL," and "Initializing Rootless Environment."
- If the device reboots unexpectedly, simply wait for it to restart and try again. Kernel exploits are not 100% reliable and may take multiple attempts.
Step 4: Initializing the Package Manager
Once the process is successful, your device will "respring" (restart the user interface). You should now see a package manager like Sileo or Zebra on your home screen. These apps act as the "App Store" for jailbroken devices. Open Sileo and perform any suggested "Essential" updates to ensure the environment is stable.
The Hardware-Based Method: Palera1n (A11 and Older)
For older devices like the iPhone X, the process involves putting the device into DFU (Device Firmware Upgrade) Mode and running an exploit over USB.
- Environment Setup: Download the Palera1n binaries on a Mac or Linux PC.
- Connection: Connect the iPhone to the computer via a USB-A cable (USB-C cables often fail to put devices into DFU mode correctly).
- DFU Entry: Follow the tool's on-screen prompts to hold the Power and Volume Down buttons in a specific sequence.
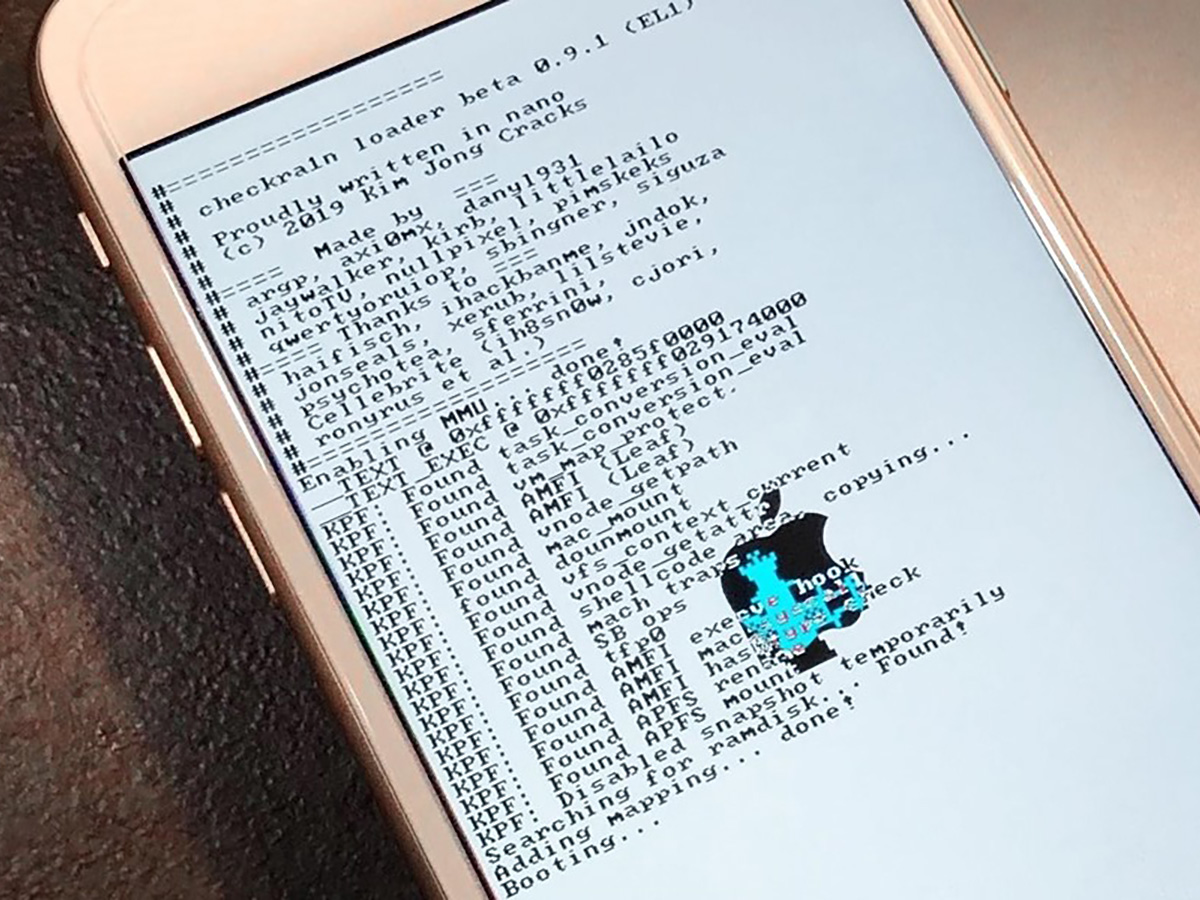
- Execution: The tool will inject the checkm8 exploit. The device will show a "verbose boot" (text scrolling on the screen).
- Loader App: Once the device boots, open the Palera1n loader app on the iPhone to install the actual jailbreak environment.
Risks, Safety, and Maintenance
Jailbreaking provides freedom, but it circumvents the "walled garden" security model that protects the average user.
Security Vulnerabilities
By gaining root (or near-root) access, you are potentially allowing malware to do the same. Never install tweaks from "piracy" repos, as these often contain injected code designed to steal iCloud credentials or financial data. Stick to reputable sources like Havoc, Chariz, or official developer GitHub pages.
Banking App Detection
Many financial applications and games (like Pokémon GO or banking apps) check for a jailbroken state. Because modern jailbreaks are rootless, they are harder to find, but you may still need "Bypass" tweaks like Choicy or Shadow to hide the jailbreak from specific apps.
System Stability and Battery Life
Poorly coded tweaks can cause "SpringBoard" crashes, leading to "Safe Mode" (where all tweaks are disabled). Additionally, excessive UI customization can lead to increased CPU cycles, which significantly drains battery life. Monitor your battery health in Settings after installing new tweaks.
The 7-Day Signing Limit
If you do not have a paid Apple Developer account ($99/year), the jailbreak app you sideloaded will expire every seven days. You must re-sign it using your computer, or use a tool like AltDaemon once jailbroken to re-sign the app on the device itself.
Troubleshooting Common Issues
- Boot Loops: If your device gets stuck on the Apple logo, perform a hard reset (Volume Up, Volume Down, then hold Power). Since the jailbreak is semi-untethered, the device will boot into a non-jailbroken state, allowing you to delete the problematic tweak.
- "Unable to Verify App": This usually means the 7-day certificate has expired. Re-sideload the app using Sideloadly.
- Exploit Failing: If the jailbreak app crashes or restarts the phone constantly, try clearing your RAM (Volume Up, Down, then hold Power until the slider appears, then hold the Home button/Home bar) or waiting 30 seconds after a reboot before hitting the "Jailbreak" button.
Frequently Asked Questions
Is jailbreaking legal in 2026?
In the United States, the Digital Millennium Copyright Act (DMCA) provides exemptions that generally allow for the jailbreaking of smartphones to enable software interoperability. However, the legality can vary by jurisdiction. Jailbreaking does void your hardware warranty with Apple, though you can usually "undo" a jailbreak by restoring the device to factory settings.
Can I still use Apple Pay and iCloud?
On modern ARM64e devices (iPhone XR and newer), Apple Pay and iCloud usually remain fully functional. On older A11 devices (iPhone 8/X) using the Palera1n jailbreak on newer iOS versions, you often have to disable the passcode and SEP features, which effectively disables Apple Pay and FaceID.
Does jailbreaking allow for free apps?
While the technical capability exists, the primary purpose of the modern jailbreak community is customization, system-level enhancements, and privacy controls. The use of jailbreaking for software piracy is widely discouraged by the developer community and increases the risk of malware infection.
How do I remove a jailbreak?
For rootless jailbreaks, most apps have an "Uninstall Jailbreak" or "Remove Jailbreak" button within the app itself. This will delete the /var/jb folder and restore the system to its original state. For a complete "clean" state, performing an iCloud factory reset or a full DFU restore via a computer is recommended.
Will I still receive iOS updates?
A jailbroken device can still see Apple's software updates, but installing one will almost certainly remove the jailbreak and may cause the device to hang during the update process. It is standard practice to disable "Automatic Updates" in Settings immediately after jailbreaking.
Recommended Next Steps
If you have confirmed your device is compatible, the best course of action is to:
- Check the "Can I Jailbreak?" community hubs on platforms like Reddit or specialized Discord servers to ensure your specific iOS build has a stable exploit.
- Download Sideloadly on your computer and obtain the latest version of Dopamine from the official GitHub repository.
- Start with essential tweaks that improve the experience without overtaxing the system, such as gesture enhancers or notification redesigns.
Image Gallery
Select an image to open it in a new tab.


Celine Dubois
Contemporary Living and Global Arts Columnist
