Why Cloud Resilience Security Providers Matter for Modern Enterprises
Modern enterprises rely on cloud resilience security providers to bridge the critical gap between disaster recovery, high availability, and continuous threat mitigation, ensuring that complex multi-cloud infrastructures can withstand sophisticated cyberattacks and operational outages without catastrophic data loss or prolonged downtime.
As organizations migrate core workloads, customer-facing applications, and sensitive databases to distributed cloud environments, traditional perimeter-based security measures fall short. Modern enterprises face a threat landscape defined by automated ransomware, distributed denial-of-service (DDoS) attacks, supply chain compromises, and human configuration errors. Cloud resilience security providers deliver integrated architectures that combine automated threat detection, real-time data replication, immutable backups, and rapid failover orchestration. By partnering with these specialized providers, enterprises transform reactive disaster recovery into proactive operational resilience, safeguarding revenue, maintaining customer trust, and complying with stringent regulatory mandates.
The Evolution of Cloud Infrastructure and Emerging Vulnerabilities
The rapid acceleration of cloud adoption has fundamentally transformed how modern enterprises build, scale, and deliver software. Moving away from monolithic on-premises data centers, organizations now orchestrate microservices across multi-cloud and hybrid environments. While this decentralization unlocks unprecedented agility and speed-to-market, it simultaneously expands the enterprise attack surface. Each cloud region, application programming interface (API), container cluster, and third-party integration introduces potential vectors for exploitation and operational failure.
Traditional security models relied on the concept of a trusted internal network protected by a sturdy perimeter firewall. In contrast, modern enterprise architectures are boundaryless. Remote workforces, edge computing nodes, and interconnected software supply chains mean that data and applications exist everywhere. Consequently, malicious actors no longer need to breach a physical perimeter; instead, they target misconfigured cloud storage buckets, compromise compromised developer credentials, or exploit vulnerabilities in open-source software libraries.
Furthermore, cloud environments are susceptible to non-malicious disruptions. Software bugs, faulty updates, infrastructure misconfigurations by internal personnel, and regional outages from major cloud service providers (CSPs) can bring an enterprise to a standstill. The shared responsibility model dictates that while CSPs secure the underlying infrastructure, the customer remains entirely responsible for securing their data, identity access management, and application logic. Bridging this operational gap requires specialized expertise that internal IT teams often struggle to maintain at scale.
Defining Cloud Resilience Security Providers
Cloud resilience security providers are specialized firms and platforms that integrate cybersecurity defense mechanisms with operational resilience and disaster recovery frameworks. Unlike traditional cybersecurity vendors that focus solely on threat prevention, or legacy disaster recovery vendors that focus exclusively on data backup, resilience security providers treat security and continuity as two sides of the same coin.
Core Capabilities of Resilience Security Providers
To understand why these providers are indispensable, it is necessary to examine the foundational capabilities they offer to enterprise clients:
- Continuous Threat Intelligence and Mitigation: Advanced monitoring tools that utilize machine learning to identify anomalous behavior, lateral movement, and zero-day exploits within cloud networks before attackers can exfiltrate data.
- Automated Backup and Immutable Storage: Creating write-once-read-many (WORM) data vaults that are cryptographically isolated from the primary production environment, rendering ransomware encryption ineffective.
- Orchestrated Failover and Recovery: Software-defined recovery workflows that automatically spin up secondary cloud regions or alternative environments in the event of a primary infrastructure failure or severe cyber incident.
- Configuration and Posture Management: Continuous scanning of cloud infrastructure-as-code (IaC) and running environments to detect compliance drifts, overly permissive access policies, and security misconfigurations.
By synthesizing these elements, resilience security providers ensure that an enterprise can absorb a severe shock—whether a targeted cyberattack or a massive regional power outage—and maintain operational continuity with minimal recovery time objectives (RTO) and recovery point objectives (RPO).
Financial, Operational, and Regulatory Drivers for Enterprises
The decision to partner with a dedicated cloud resilience security provider is driven by converging financial, operational, and regulatory pressures. In the current economic climate, downtime is measured not just in lost productivity, but in millions of dollars of lost revenue, reputational damage, and regulatory penalties.
Quantifying the Cost of Downtime and Data Loss
For modern enterprises, applications are the business. Whether dealing with financial transactions, healthcare records, or e-commerce checkouts, every minute of unplanned downtime translates directly to lost revenue and frustrated users. According to industry analyses, enterprise downtime frequently costs tens of thousands of dollars per minute, excluding long-term customer churn and brand erosion.
Beyond availability, the financial impact of a successful ransomware attack or data breach has escalated dramatically. Extortion demands, forensic investigation costs, legal fees, and mandatory notification expenses can destabilize even a Fortune 500 company. Cloud resilience security providers mitigate these financial risks by ensuring that even if a network is compromised, clean, uncorrupted data can be restored rapidly, bypassing the need to negotiate with cybercriminals.
Navigating Complex Regulatory Compliance
Regulatory frameworks across the globe have grown increasingly stringent regarding data protection, privacy, and operational resilience. Regulations such as the European Union’s Digital Operational Resilience Act (DORA), the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), and various state-level privacy laws demand rigorous proof of business continuity and data security measures.
Failure to meet these compliance standards results in severe financial penalties and legal liability. Cloud resilience security providers assist enterprises by embedding compliance directly into the infrastructure lifecycle. They maintain detailed audit trails, enforce strict access controls, and ensure that data sovereignty and residency requirements are rigorously upheld across multi-cloud deployments.
Key Features to Evaluate in a Cloud Resilience Security Partner
Selecting the appropriate cloud resilience security provider requires a systematic evaluation of technical capabilities, architectural alignment, and service-level agreements (SLAs). Not all providers offer the same depth of integration or coverage across diverse cloud ecosystems.
| Evaluation Criterion | Description | Key Enterprise Consideration |
|---|---|---|
| Multi-Cloud Compatibility | Ability to protect and recover workloads across AWS, Azure, Google Cloud, and private data centers. | Avoids vendor lock-in and ensures uniform security posture across heterogeneous environments. |
| Recovery Speed (RTO/RPO) | The speed at which systems can be restored (RTO) and the maximum acceptable data loss measured in time (RPO). | Must align with mission-critical application requirements and business continuity SLAs. |
| Immutability and Air-Gapping | Protection mechanisms that prevent backup data from being altered, deleted, or encrypted by ransomware. | Essential defense against sophisticated double-extortion ransomware campaigns. |
| Automation and Orchestration | The degree of human intervention required to execute a failover or initiate recovery procedures. | Minimizes human error during high-stress incident response scenarios. |
| Compliance and Auditability | Built-in reporting, logging, and governance frameworks aligned with industry standards. | Simplifies regulatory audits and proves due diligence to stakeholders and insurers. |
Architectural Integration and Vendor Lock-In
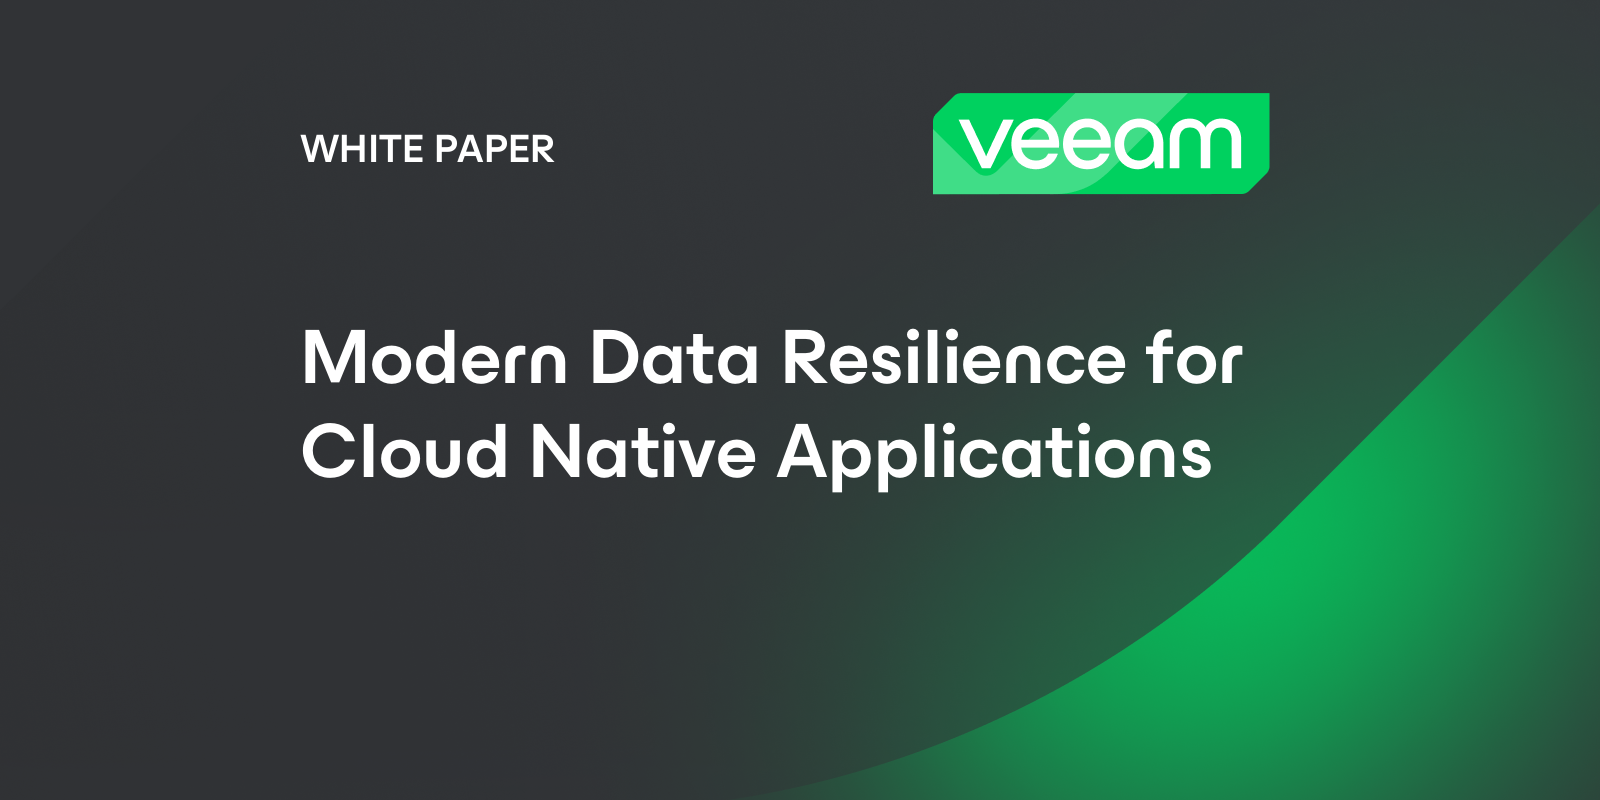
A common pitfall during provider selection is failing to examine how deeply the security solution integrates with existing enterprise architecture. Enterprises must ensure that the provider supports their preferred DevOps pipelines, infrastructure-as-code tools, and container orchestration platforms like Kubernetes. Furthermore, organizations should verify that data portability is maintained, preventing the provider from locking enterprise data into proprietary formats that complicate future migrations.
Common Mistakes Enterprises Make in Cloud Resilience
Despite recognizing the importance of cloud security and business continuity, many enterprises stumble during implementation due to recurring strategic and tactical errors. Identifying these pitfalls allows organizations to fortify their security posture before an incident occurs.
Relying Solely on Native Cloud Provider Tools
Many enterprises assume that by utilizing tier-one cloud providers (such as Amazon Web Services, Microsoft Azure, or Google Cloud Platform), they are automatically protected against all operational failures and cyber threats. While these hyperscalers offer robust foundational security tools and native backup options, relying exclusively on them creates a single point of failure. If a widespread regional outage impacts the primary cloud provider, native backup mechanisms hosted within that same ecosystem may also be inaccessible. Independent cloud resilience security providers offer an essential layer of redundancy by externalizing and diversifying backup and security operations.
Failing to Test Recovery Procedures
Having a disaster recovery plan on paper is vastly different from executing it successfully under pressure. A frequent mistake among enterprises is treating disaster recovery as a set-and-forget task. Without regular, automated testing and table-top simulation exercises, IT teams often discover critical flaws—such as expired credentials, missing configuration files, or incompatible dependencies—only when a real outage or cyberattack is underway.
Neglecting Insider Threats and Configuration Drift
Organizations often invest heavily in perimeter defenses against external attackers while neglecting internal security hygiene. Misconfigurations caused by manual changes or inadequate access controls account for a substantial percentage of cloud security incidents. Resilience security providers help mitigate this by enforcing continuous compliance monitoring and zero-trust access architectures, ensuring that permissions are continuously audited and restricted to the principle of least privilege.
Practical Steps to Implement Cloud Resilience in the Enterprise
Integrating a robust cloud resilience security framework requires a structured, multi-phase approach that involves cross-functional alignment between security teams, cloud architects, and business unit leaders.
- Assess and Classify Data and Workloads: Conduct a comprehensive inventory of all enterprise applications and data repositories. Categorize them based on criticality, regulatory requirements, and financial impact should they experience downtime or data loss.
- Define Target RTO and RPO Metrics: Establish clear, measurable recovery time objectives and recovery point objectives for each workload category in collaboration with business stakeholders.
- Evaluate and Select a Specialized Provider: Issue a request for proposal (RFP) targeting cloud resilience security providers that match your multi-cloud environment, compliance needs, and budget constraints.
- Implement Immutable Backups and Air-Gapping: Deploy secondary, cryptographically isolated data vaults that cannot be modified or deleted by unauthorized users or ransomware algorithms.
- Automate and Test Failover Workflows: Build automated orchestration scripts for disaster recovery and schedule regular, unannounced disaster simulation tests to validate operational readiness.
- Establish Continuous Monitoring and Posture Management: Deploy continuous configuration scanning tools to detect security drift, compliance gaps, and unauthorized access attempts in real time.
Frequently Asked Questions
What is the difference between standard cloud backup and cloud resilience security?
Standard cloud backup focuses strictly on creating copies of data for restoration after accidental deletion or hardware failure. Cloud resilience security, by contrast, integrates automated backup with proactive threat hunting, ransomware defense, immutable storage, and orchestrated failover capabilities, ensuring the enterprise remains operational during active cyberattacks or major infrastructure outages.
How do cloud resilience providers protect against ransomware?
These providers utilize immutable storage vaults, also known as WORM (Write Once, Read Many) storage, which make backup copies completely unalterable and undeletable for a defined retention period. Additionally, they employ behavioral analytics to detect ransomware encryption activity early, allowing security teams to isolate compromised systems before malware spreads to backups.
Can small and mid-sized enterprises (SMEs) benefit from these providers?
Yes. While large enterprises face complex multi-cloud management challenges, SMEs often lack dedicated internal security operations centers (SOCs) and disaster recovery specialists. Cloud resilience security providers offer scalable, subscription-based managed services that grant smaller organizations enterprise-grade protection without requiring massive internal staffing investments.
How often should an enterprise test its cloud disaster recovery plan?
Best practices recommend conducting automated recovery testing continuously or at least quarterly, alongside full-scale manual simulation exercises semi-annually. Regular testing ensures that recovery scripts remain functional as application architectures evolve and verifies that personnel are familiar with incident response protocols.
What is the shared responsibility model in cloud security?
The shared responsibility model defines security obligations between the cloud service provider (CSP) and the customer. The CSP is responsible for securing the underlying cloud infrastructure (hardware, physical data centers, host operating systems). The customer is responsible for securing everything they put on the cloud, including data, customer access, application code, and identity management configurations.
Conclusion and Strategic Next Actions
Modern enterprises operate in a digital environment where disruptions—whether driven by malicious cybercriminals or unforeseen technical failures—are an inevitability rather than a possibility. Relying on outdated perimeter security or basic, unverified backup routines is no longer sufficient to guarantee business continuity. Cloud resilience security providers play an indispensable role by unifying threat mitigation, immutable data protection, and automated disaster recovery into a cohesive operational strategy.
To secure their organization's future, technology leaders must immediately audit their current cloud infrastructure vulnerabilities, establish rigorous RTO and RPO metrics, and engage specialized resilience partners to build a secure, adaptable, and highly available enterprise ecosystem.
Image Gallery
Select an image to open it in a new tab.
Vivian Cho
Executive IT and Emerging Technologies Reporter
