Understanding the Cloud Native Software Security Handbook

A cloud native software security handbook is a comprehensive technical guide or framework designed to provide security practitioners, developers, and DevOps engineers with standardized patterns, threat models, and operational strategies for securing applications built for dynamic, distributed cloud environments. These handbooks serve as a bridge between high-level security compliance mandates and the granular, automated requirements of microservices architectures.
The Evolution of Cloud Native Security Documentation
In the era of legacy infrastructure, security documentation often focused on perimeter defense, static firewalls, and manual patch management. As enterprises transitioned to cloud native architectures—characterized by containerization, orchestrators like Kubernetes, and ephemeral serverless functions—the complexity of the attack surface grew exponentially. A modern cloud native software security handbook addresses this by shifting the focus from static host-level security to identity-centric, automated, and observable security postures.
These handbooks are rarely just theoretical textbooks. They function as "living documentation," often maintained within organizations or by open-source communities to address the rapid cycle of software releases. They synthesize best practices from standards bodies and industry frameworks, such as the Cloud Native Computing Foundation (CNCF) Security Technical Advisory Group or the OWASP Foundation, and translate them into actionable workflows for teams adopting DevSecOps.
Core Components and Themes
A robust security handbook for cloud native software typically centers on several fundamental pillars. Understanding these is essential for any technical team attempting to operationalize security within their deployment pipelines.
1. Shift-Left Security Integration
The most prominent theme in these handbooks is the integration of security controls early in the development lifecycle. Instead of waiting for a security audit at the end of a sprint, the handbook defines how developers should use static analysis (SAST), software composition analysis (SCA) for dependency management, and infrastructure-as-code (IaC) scanning before any code is committed or deployed to a container registry.
2. Identity and Access Management (IAM)
In a cloud native environment, the network perimeter is effectively dissolved. Handbooks emphasize "zero-trust" architectures where identity is the new perimeter. This includes detailed guidance on implementing fine-grained Role-Based Access Control (RBAC), workload identity (such as SPIFFE), and the secure rotation of secrets and service accounts.
3. Supply Chain Integrity
As software is composed of numerous open-source libraries and container images, the supply chain has become a primary target for attackers. Security handbooks provide specific instructions on how to implement Software Bill of Materials (SBOM) tracking, image signing using tools like Sigstore, and the enforcement of binary authorization to ensure that only trusted, scanned images run in production clusters.
4. Observability and Runtime Protection
Cloud native systems require active monitoring. These handbooks cover the implementation of eBPF-based security tools for runtime threat detection, audit logging for Kubernetes API traffic, and automated incident response workflows. The goal is to move from reactive log analysis to proactive detection of anomalies in microservice behavior.
Comparison of Security Approaches
To grasp the utility of a security handbook, it is helpful to compare the transition from traditional security models to cloud native security patterns.
| Feature | Traditional Infrastructure | Cloud Native Architecture |
|---|---|---|
| Trust Model | Perimeter-based (Inside/Outside) | Zero-trust (Assume breach) |
| Asset Lifecycle | Long-lived (Months/Years) | Ephemeral (Minutes/Hours) |
| Security Control | Manual/Gatekeeper | Automated/Policy-as-Code |
| Policy Enforcement | Checklists and Audits | Admission Controllers |
| Visibility | Network traffic monitoring | Service mesh/distributed tracing |
Why Organizations Need a Dedicated Handbook
Adopting cloud native technologies without a centralized security handbook often leads to "configuration drift" and fragmented security postures. When individual engineering squads implement security controls in isolation, they often miss critical interactions between microservices.
A handbook provides:
- Consistency: Ensures that all microservices follow the same authentication and encryption standards.
- Reduced Cognitive Load: Developers do not need to rediscover security requirements; they can reference the documented standard for common tasks like secret injection or sidecar configuration.
- Auditability: A documented handbook serves as evidence of security maturity for compliance regulators, demonstrating that the organization has a defined strategy for managing cloud risks.
- Accelerated Onboarding: New engineers can quickly familiarize themselves with the specific security patterns expected in the production environment.
Prerequisites for Implementing Handbook Guidance
Before an organization can effectively utilize a security handbook, certain foundational elements must be in place. Attempting to enforce high-level security patterns without these prerequisites usually results in friction and non-compliance.
- Infrastructure as Code (IaC) Adoption: Security handbooks assume the environment is defined in code (e.g., Terraform, Helm, or Crossplane). Without IaC, it is impossible to apply automated security guardrails consistently.
- Containerization Maturity: The team must have a standardized way of building and deploying containers. If teams are using wildly different base images or inconsistent runtime environments, the handbook’s recommendations for container hardening will be difficult to enforce.
- Automation Culture: The team must be committed to CI/CD pipelines. Security controls in a cloud native handbook are designed to be executed by the pipeline. Manual security reviews are effectively incompatible with the scale of modern cloud native deployments.
Addressing Common Implementation Mistakes
Even with a handbook in place, organizations often stumble during the operational phase. Recognizing these pitfalls is a key part of the handbook's "lessons learned" or "best practices" sections.
- Over-reliance on Tooling: A common mistake is buying security tools (e.g., a commercial Kubernetes security platform) while ignoring the underlying policy documentation. Tools should implement the policy, not replace the need for clear standards.
- Permissive RBAC Policies: Developers frequently use "admin" or "cluster-admin" roles to avoid troubleshooting permission issues. A strong handbook mandates a path toward least-privilege access, even if it adds temporary operational friction during development.
- Ignoring Service-to-Service Traffic: Many organizations focus on ingress security but neglect the east-west traffic between microservices. Handbooks emphasize the use of a service mesh to enforce mutual TLS (mTLS) for all internal communication.
Selecting the Right Material for Your Team
As of 2026, the market offers several types of "Cloud Native Software Security Handbooks." Some are authored by individual cloud providers (such as AWS, Google Cloud, or Azure security whitepapers), while others are industry-agnostic books published by organizations like O’Reilly Media or the CNCF.
- Vendor-Specific Guides: Best for teams deeply committed to a single cloud provider. They provide specific instructions on using native tools like AWS IAM, Azure Policy, or Google Workload Identity.
- Vendor-Neutral Frameworks: Best for multi-cloud or hybrid-cloud environments. These focus on universal patterns like OPA (Open Policy Agent) or SPIFFE/SPIRE, which work across different infrastructures.
Frequently Asked Questions
1. Is a cloud native security handbook the same as a policy document? While they overlap, a handbook is more practical. A policy document states what is required, whereas a handbook provides the "how-to" implementation details, including configuration examples and architecture diagrams to achieve that policy.
2. Should developers write the handbook or security teams? The most effective handbooks are written collaboratively. If security teams write it alone, it may be technically impractical; if developers write it, it may lack sufficient security rigor. Co-authorship ensures that the security controls are both effective and developer-friendly.
3. How often should these handbooks be updated? In a 2026 cloud native context, a static document is often obsolete within six months. Teams should treat the handbook as a version-controlled repository (GitOps style), allowing for frequent updates as software versions, APIs, and threat landscapes evolve.
4. Can this handbook help with compliance audits like SOC2 or ISO 27001? Yes. By mapping your documented patterns in the handbook to specific controls required by compliance frameworks, you can significantly streamline the audit process. It demonstrates to auditors that you have a proactive, automated, and repeatable process for securing your infrastructure.
Next Steps for Implementation
To begin implementing these principles within your organization, start by auditing your existing development workflow against a recognized security baseline. Create a central repository for your "Cloud Native Security Handbook," utilizing a Markdown-based format that is easy for developers to search and contribute to. Begin with high-impact areas, such as standardizing your container image base or implementing a service mesh for mTLS. As your team matures, expand the handbook to cover edge cases, incident response playbooks, and continuous threat modeling.
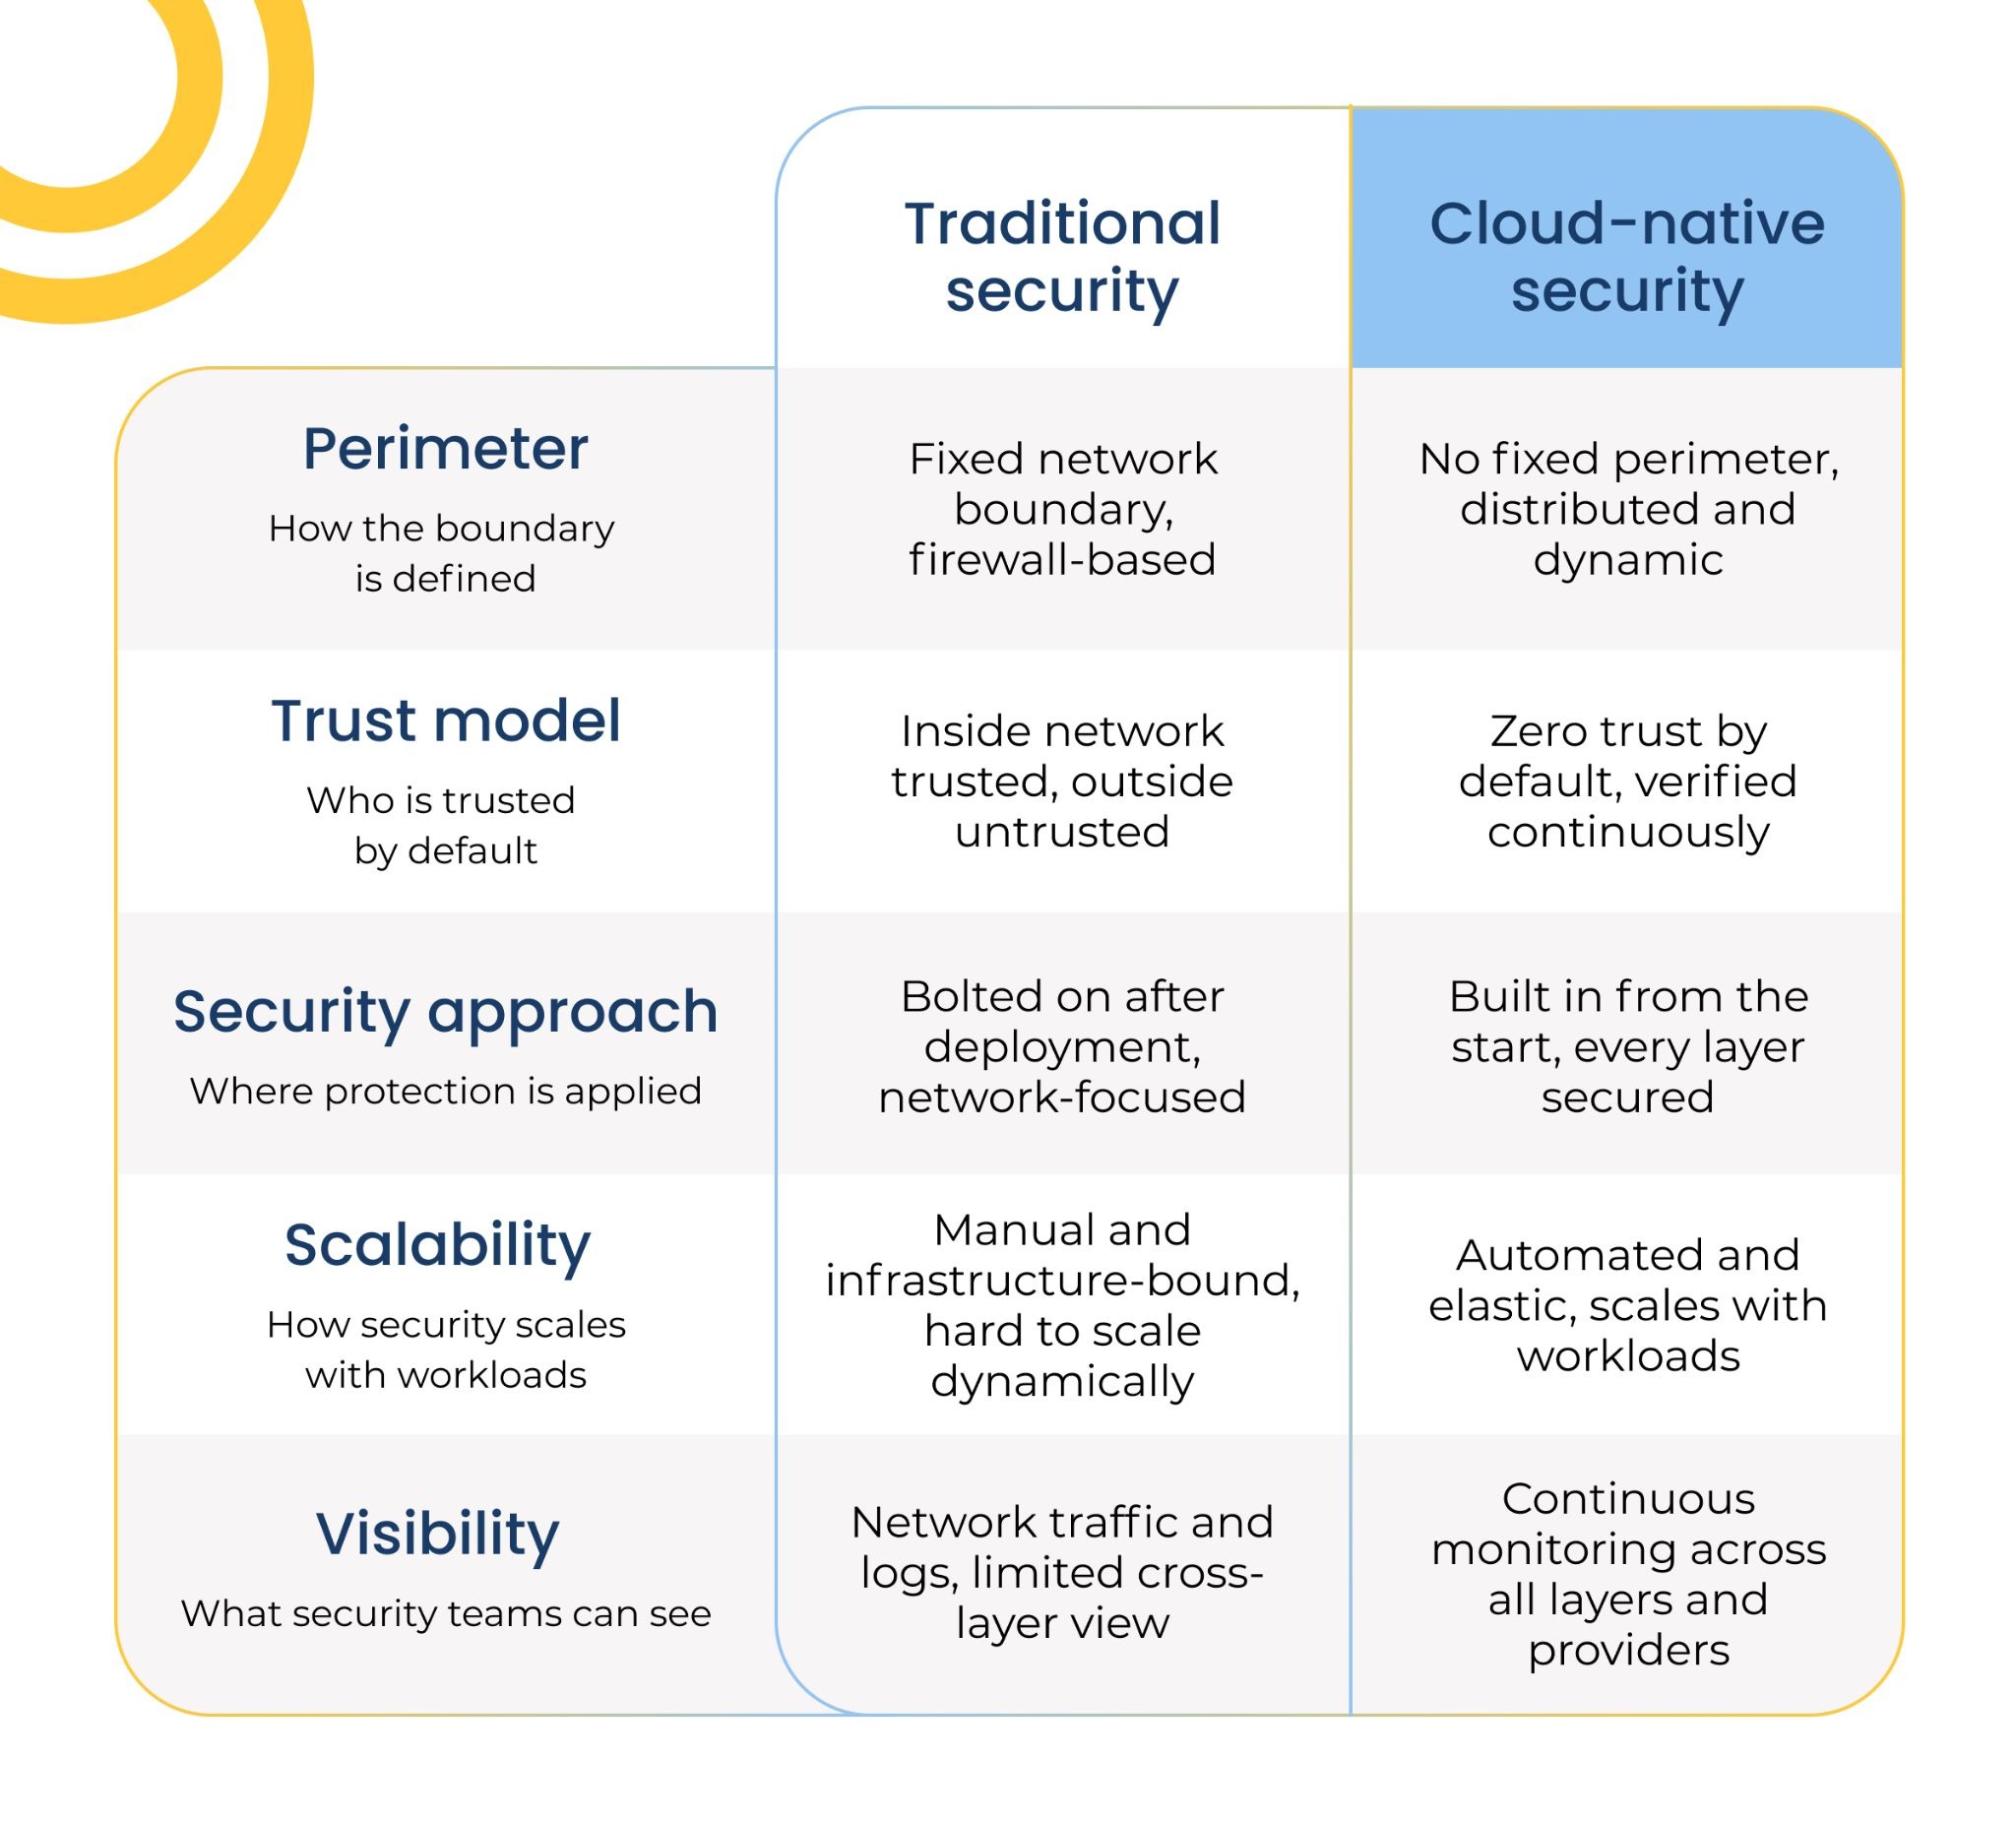
Image Gallery
Select an image to open it in a new tab.

Omar Farooq
EdTech Innovation and Virtual Pedagogy Journalist
